ostering.com
  • Threat Taxonomies
    • Email Infrastructure
      • Delivery pipeline (DP)
      • Authentication protocols (AU)
      • Client protocols (CP)
      • SMTP (SM)
      • MIME and S/MIME (MI)
      • DNS layer (DN)
      • Content scanners (CS)
      • Human-facing layer (HF)
      • Operations and storage (OP)
      • Structural hazards (T)
    • Software Factory
      • Line 1
      • Workstation and Agents (WS)
      • Version Control (VC)
      • Pipeline Definition (PD)
      • Runners (RN)
      • Pipeline Identity and Secrets (ID)
      • Build Systems (BS)
      • Dependency Resolution (DR)
      • Scanners and Gates (SG)
      • Provenance and Attestation (PV)
      • Line 2
      • Registries (RG)
      • Firewall and Quarantine (FW)
      • SBOM and VEX (BM)
      • Infrastructure as Code (IC)
      • Container Images (IM)
      • Container Runtime (RT)
      • Orchestration (OR)
      • Delivery and Deployment (DL)
      • Structural hazards (T)
  • Threat Modeling
  • Supply Chain Security
  • AI Security
  • Posts
  • Talks
  • Privacy

Tagged in: CWE (1)

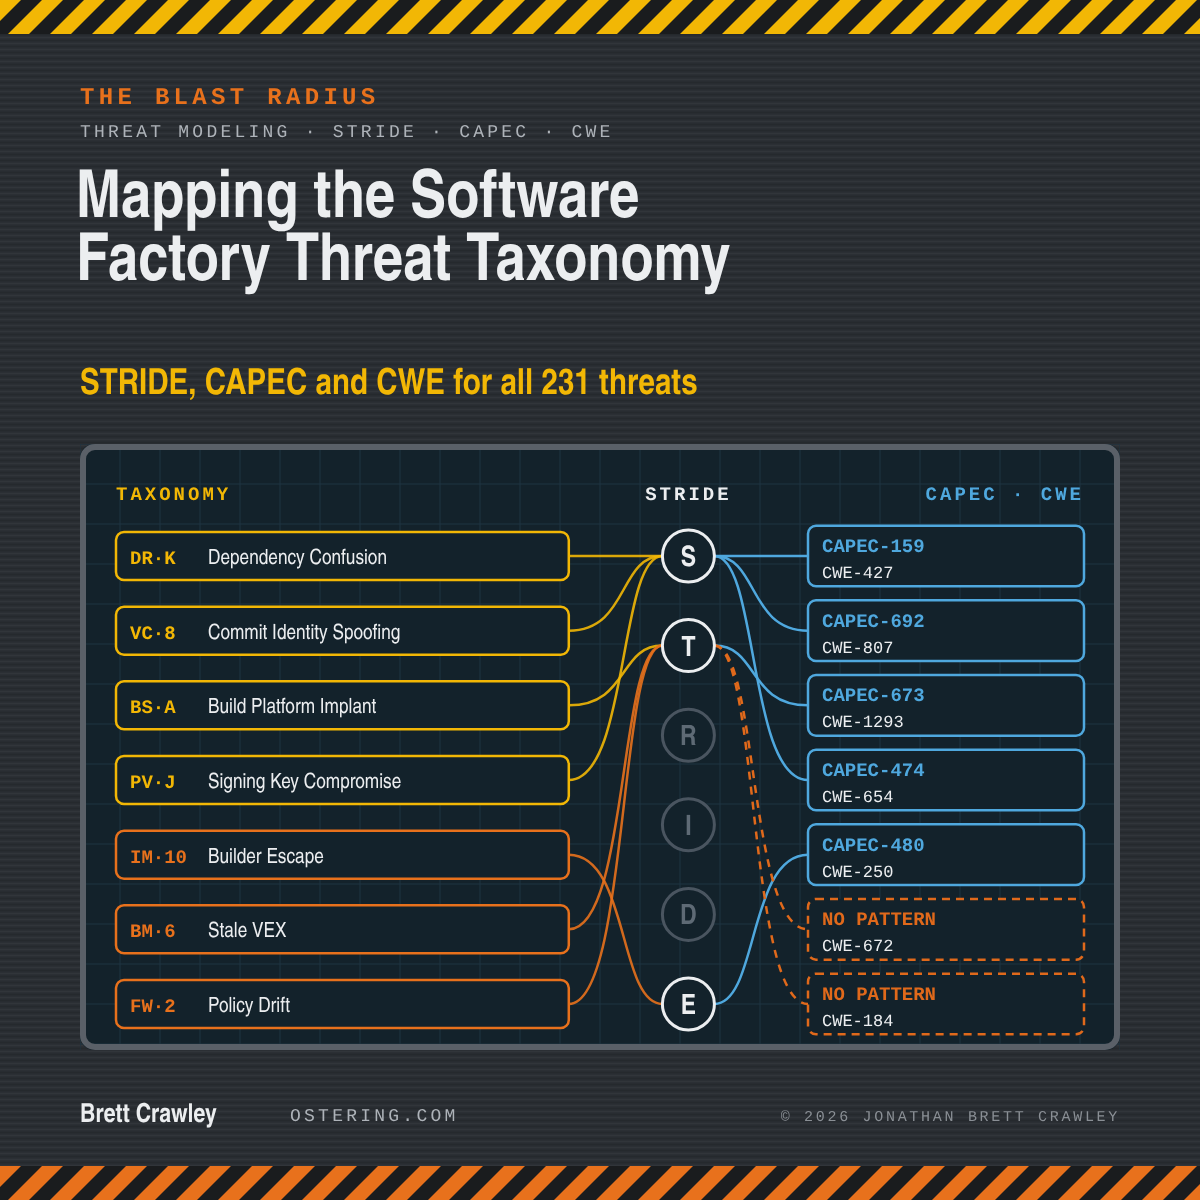
Mapping the Software Factory Threat Taxonomy: STRIDE, CAPEC and CWE for all 231 threats. Seven real entries from the mapping linked to their STRIDE letter, CAPEC 3.9 pattern and CWE 4.20 weakness; two, Stale VEX and Policy Drift, have no CAPEC pattern but do have a CWE weakness.

Mapping the Software Factory Threat Taxonomy

Mapping the Software Factory Threat Taxonomy to STRIDE,...

October 31, 2026

Browse all Topics

  • Agentic AI
  • AI Security
  • Application Security
  • Auth
  • AWS
  • CAPEC
  • Catasto
  • Change
  • Claude Code Security
  • Cloud Security
  • Compliance
  • CRA
  • Cryptography
  • Culture
  • Cursor AI
  • CWE
  • Cybersecurity
  • Dark Patterns
  • DevSecOps
  • DIY
  • DORA
  • Elevation of Privilege
  • Email Security
  • Games
  • Garden Wildlife
  • Graph Analysis
  • Hedgehog
  • Inner-Source
  • Java
  • JavaScript
  • KMS
  • languages
  • learning
  • Miro
  • Mitre
  • Model Context Protocol
  • NIS2
  • Open-Source
  • Origins
  • Osteria
  • OWASP
  • Post Quantum Cryptography
  • Privacy
  • Privacy by Design
  • Python
  • Risk
  • Running
  • SAST
  • SBOM
  • scarno
  • Secure by Design
  • Security
  • Security by Design
  • Security Culture
  • Security Maturity
  • SLSA
  • Social Engineering
  • Software Architecture
  • Software Design
  • Software Development
  • Software Engineering
  • Software Quality
  • src2sink
  • Strategy
  • STRIDE
  • Supply Chain Security
  • Technical Dept
  • Threat Modeling
  • TRIM
  • Woodworking
ostering.com

{Osteria}{Running}

Copyright 2026 Brett Crawley


This website uses cookies
Select which cookies to opt-in to via the checkboxes below; our website uses cookies to examine site traffic and user activity while on our site, and to provide social media functionality. Privacy Policy
Cookie settings
We use cookies to enhance your browsing experience, serve content, and analyze our traffic. By clicking "Accept All", you consent to our use of cookies. Privacy Policy
  • Required

    These cookies are used to enhance your browsing experience, and serve content.

  • analytics

    Our site anonymizes all of its tracking data, making it fully GDPR-compliant