DNS layer (DN)
Taxonomies › Email infrastructure › DNS layer
Layer 06 of 09 · 13 threats · prefix DN
DNS decides where mail goes and who may send it, so whoever controls or falsifies an answer controls the mail. These entries cover the records the platform publishes, hosts for tenants and resolves.
Scope: The records and resolvers that say where mail goes and who may send it.
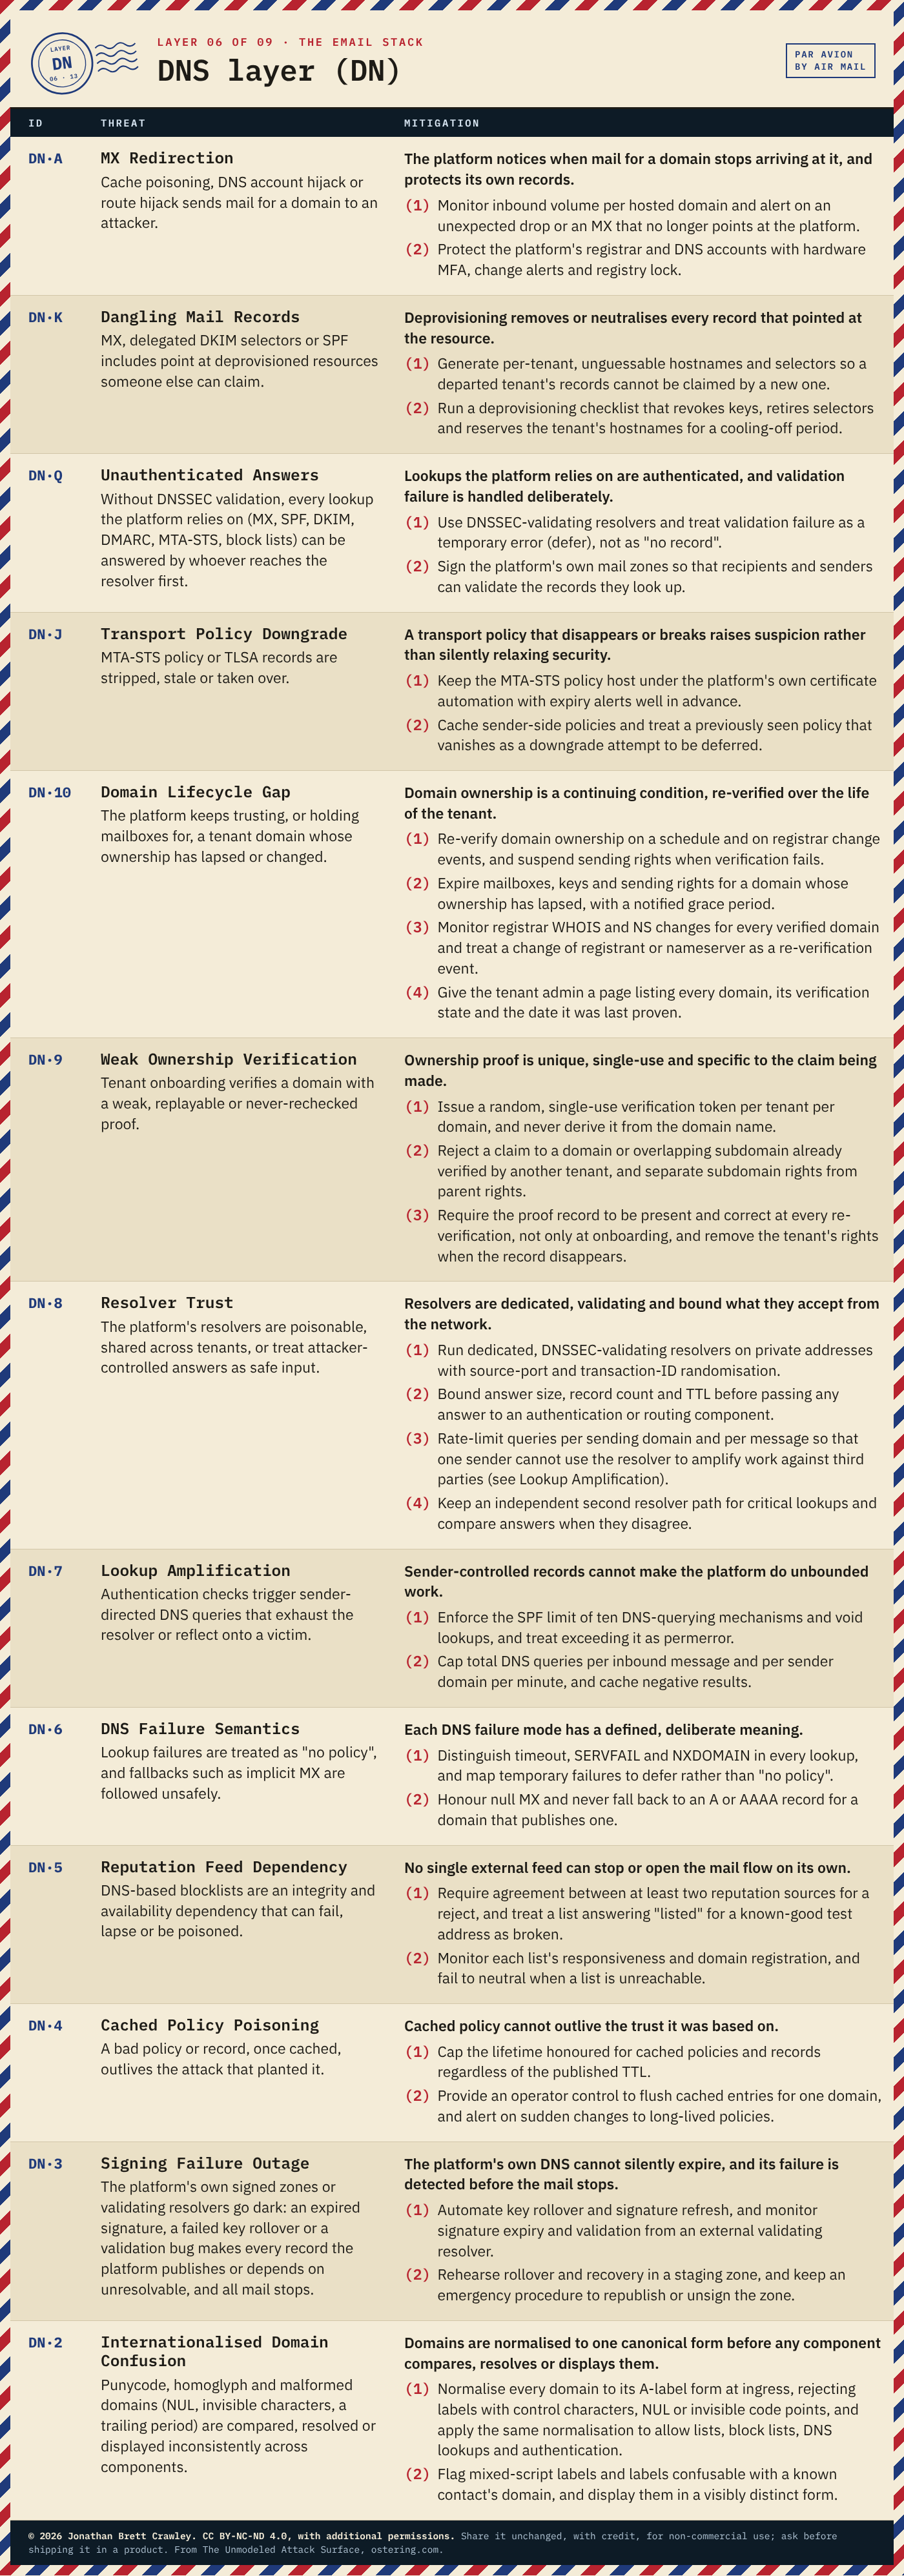
Text version: every entry on this page is in the PDF and Excel downloads on the overview page, where it can be searched and copied.
The threats
- DN·A MX Redirection
- DN·K Dangling Mail Records
- DN·Q Unauthenticated Answers
- DN·J Transport Policy Downgrade
- DN·10 Domain Lifecycle Gap
- DN·9 Weak Ownership Verification
- DN·8 Resolver Trust
- DN·7 Lookup Amplification
- DN·6 DNS Failure Semantics
- DN·5 Reputation Feed Dependency
- DN·4 Cached Policy Poisoning
- DN·3 Signing Failure Outage
- DN·2 Internationalised Domain Confusion
Where this layer touches others
- Authentication and DNS: DNS covers who can control or falsify an answer. Authentication covers what a genuine answer can be made to mean.
- Operations and the other layers: delivery pipeline, client protocols and DNS each cover a corner of operations (admin routing changes in DP·2, mailbox state in CP·10, dangling records in DN·K). Operations and storage covers the stores and tooling around the message path: the copies, the credentials and the people with access.
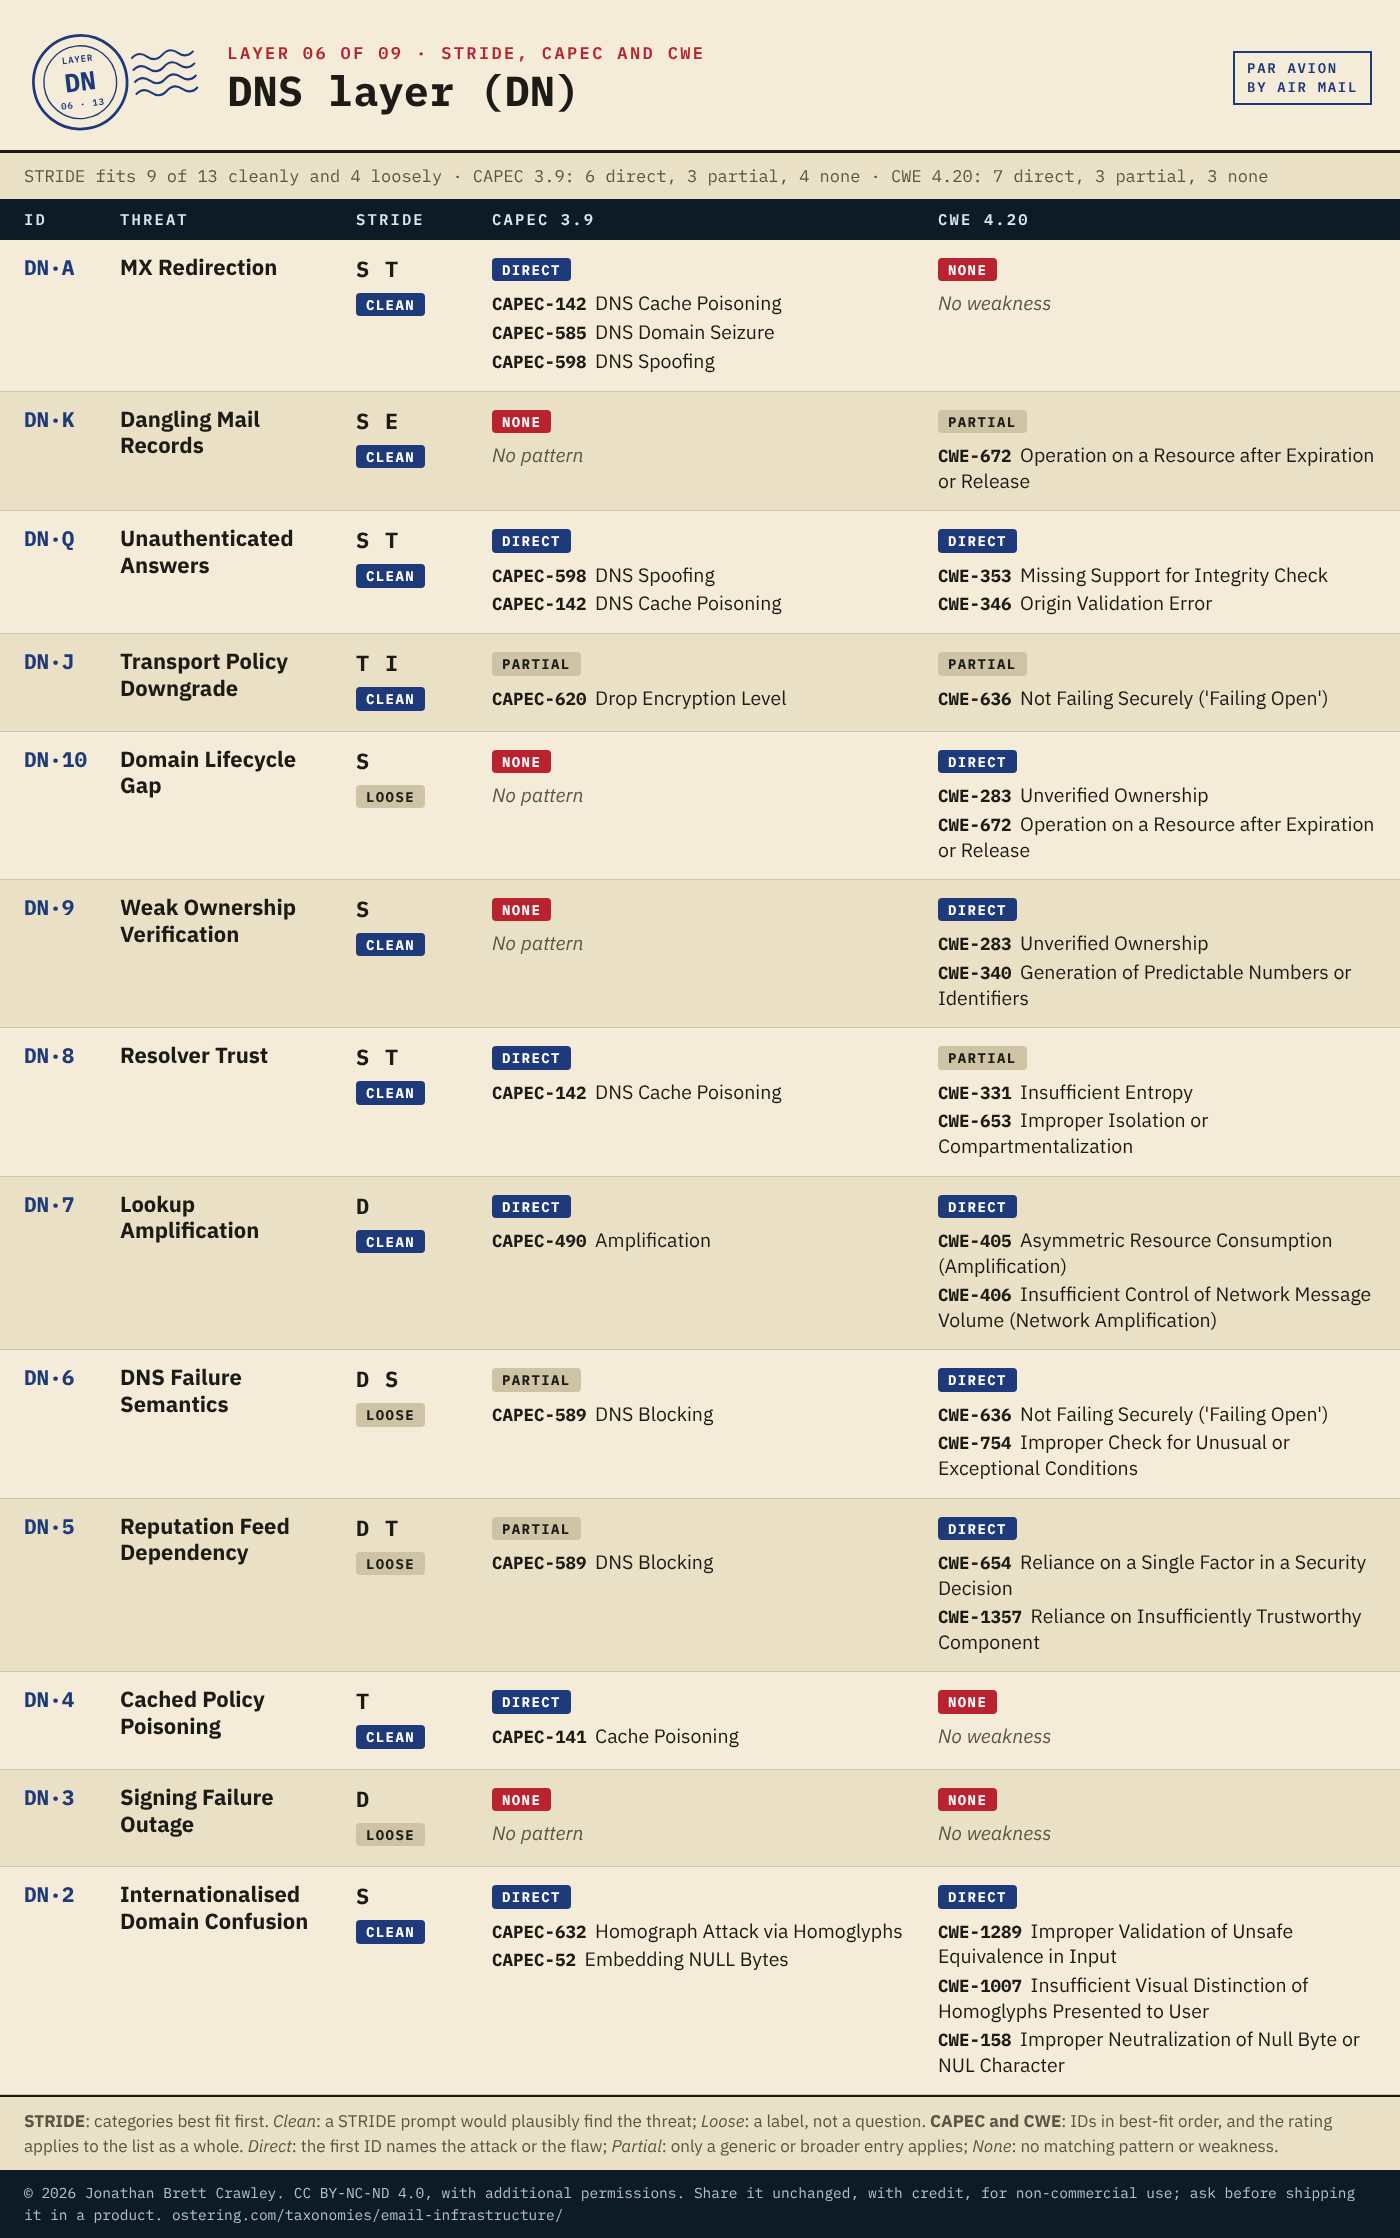
STRIDE, CAPEC and CWE
Of the 13 entries here, STRIDE fits 9 cleanly and 4 only loosely. CAPEC 3.9 has a pattern that describes 6 of them directly, only a generic parent pattern for 3, and nothing for 4. CWE 4.20 names the weakness directly for 7, has only a broader weakness for 3, and nothing for 3. The table below gives the mapping entry by entry, with the names of the CAPEC patterns and CWE weaknesses; what the mapping shows across the whole taxonomy is in Mapping the Email Threat Taxonomy to STRIDE, CAPEC and CWE. The Excel, SKOS and STIX downloads carry the same mapping as text.
← MIME and S/MIME (MI) · Email infrastructure overview · Content scanners (CS) →
© 2026 Jonathan Brett Crawley. Licensed under CC BY-NC-ND 4.0 with additional permissions: see the licence on the email infrastructure overview.