Provenance and Attestation (PV)
Taxonomies › Software factory › Provenance and Attestation
Station 09 of 17 · Line 1, Source to Artifact · 13 threats · prefix PV
Provenance is only worth what its verifier enforces and only as honest as the platform that wrote it. These cards cover SLSA provenance, in-toto attestations, artifact signing, Sigstore and transparency logs, and the verification that is meant to act on them.
Scope: SLSA provenance, in-toto attestations, signing, Sigstore, transparency logs, verification.
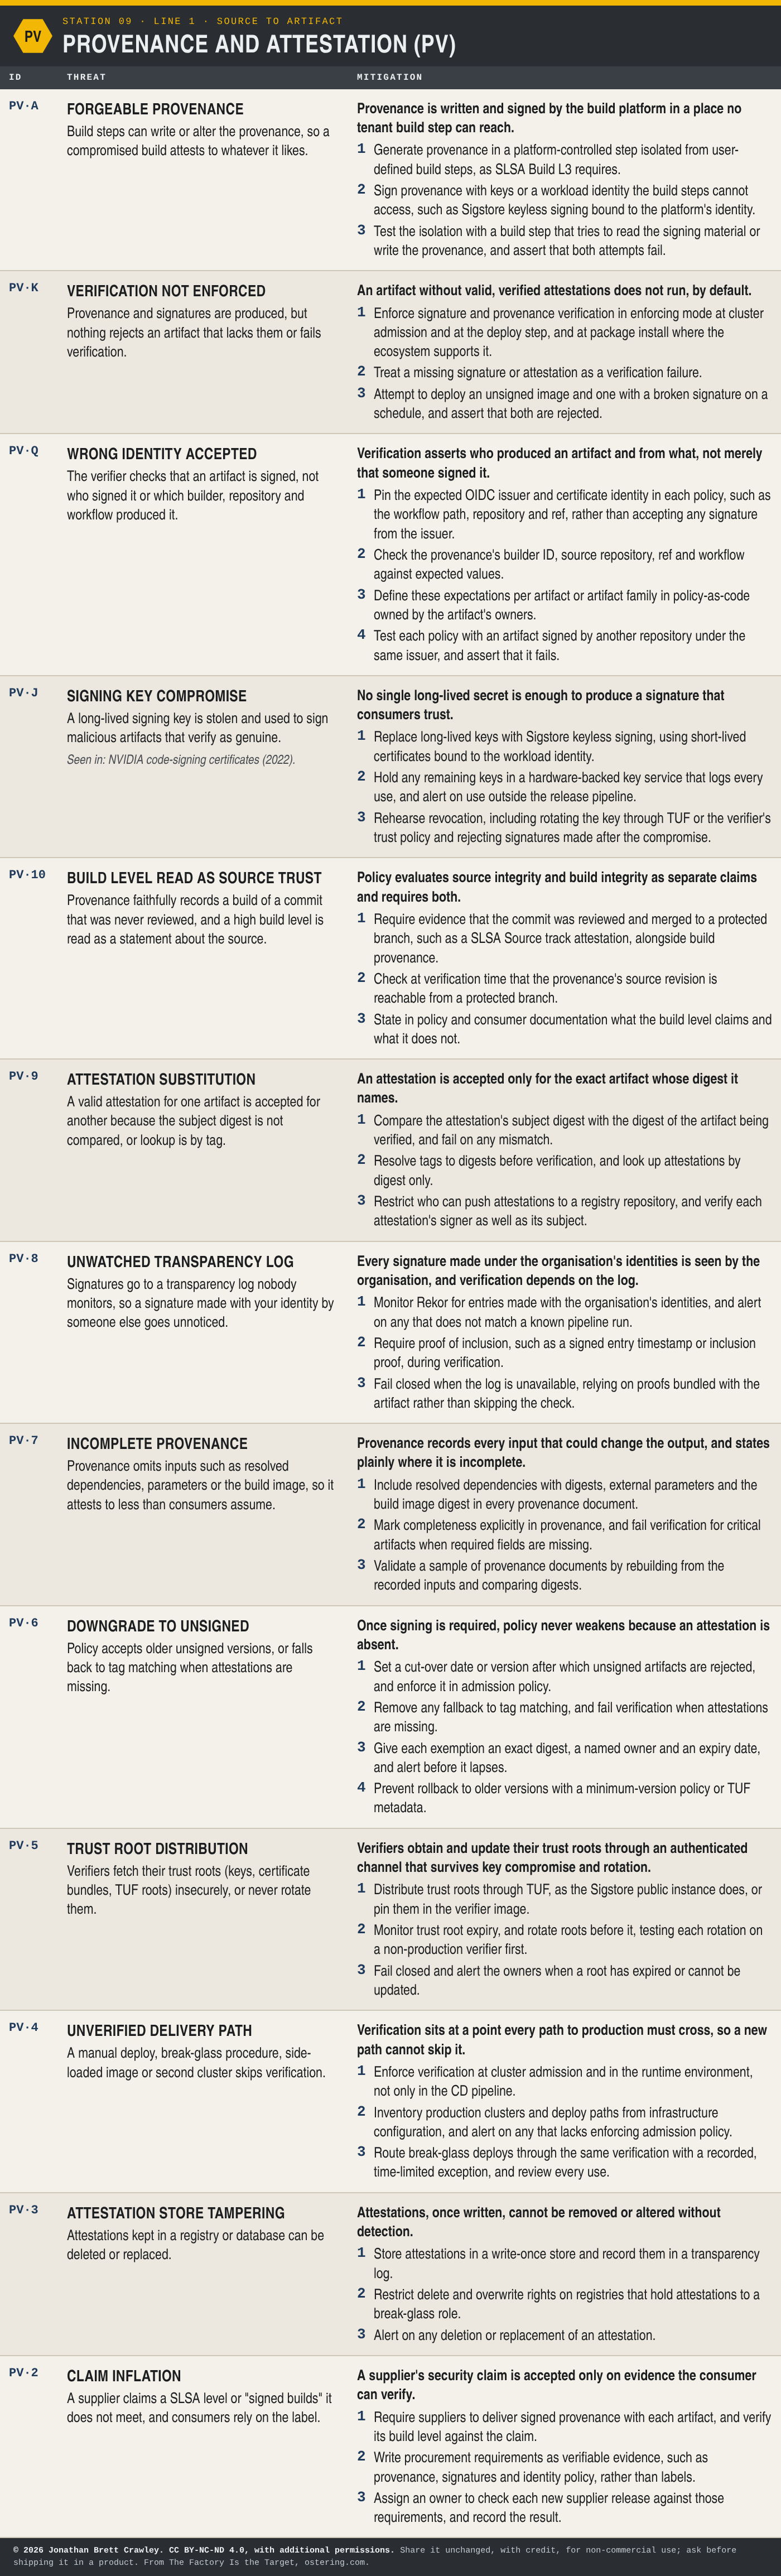
Text version: every entry on this page is in the PDF and Excel downloads on the overview page, where it can be searched and copied.
The threats
- PV·A Forgeable Provenance
- PV·K Verification Not Enforced
- PV·Q Wrong Identity Accepted
- PV·J Signing Key Compromise
- PV·10 Build Level Read as Source Trust
- PV·9 Attestation Substitution
- PV·8 Unwatched Transparency Log
- PV·7 Incomplete Provenance
- PV·6 Downgrade to Unsigned
- PV·5 Trust Root Distribution
- PV·4 Unverified Delivery Path
- PV·3 Attestation Store Tampering
- PV·2 Claim Inflation
Where this station touches others
- Provenance and Attestation and SBOM and VEX: provenance says how an artifact was made; the SBOM says what is in it. A verifier needs both to be true and both to describe the same artifact.
Seen in the wild
- PV·J Signing Key Compromise: NVIDIA code-signing certificates (2022).
Sources for each case are listed on the overview page.
STRIDE, CAPEC and CWE
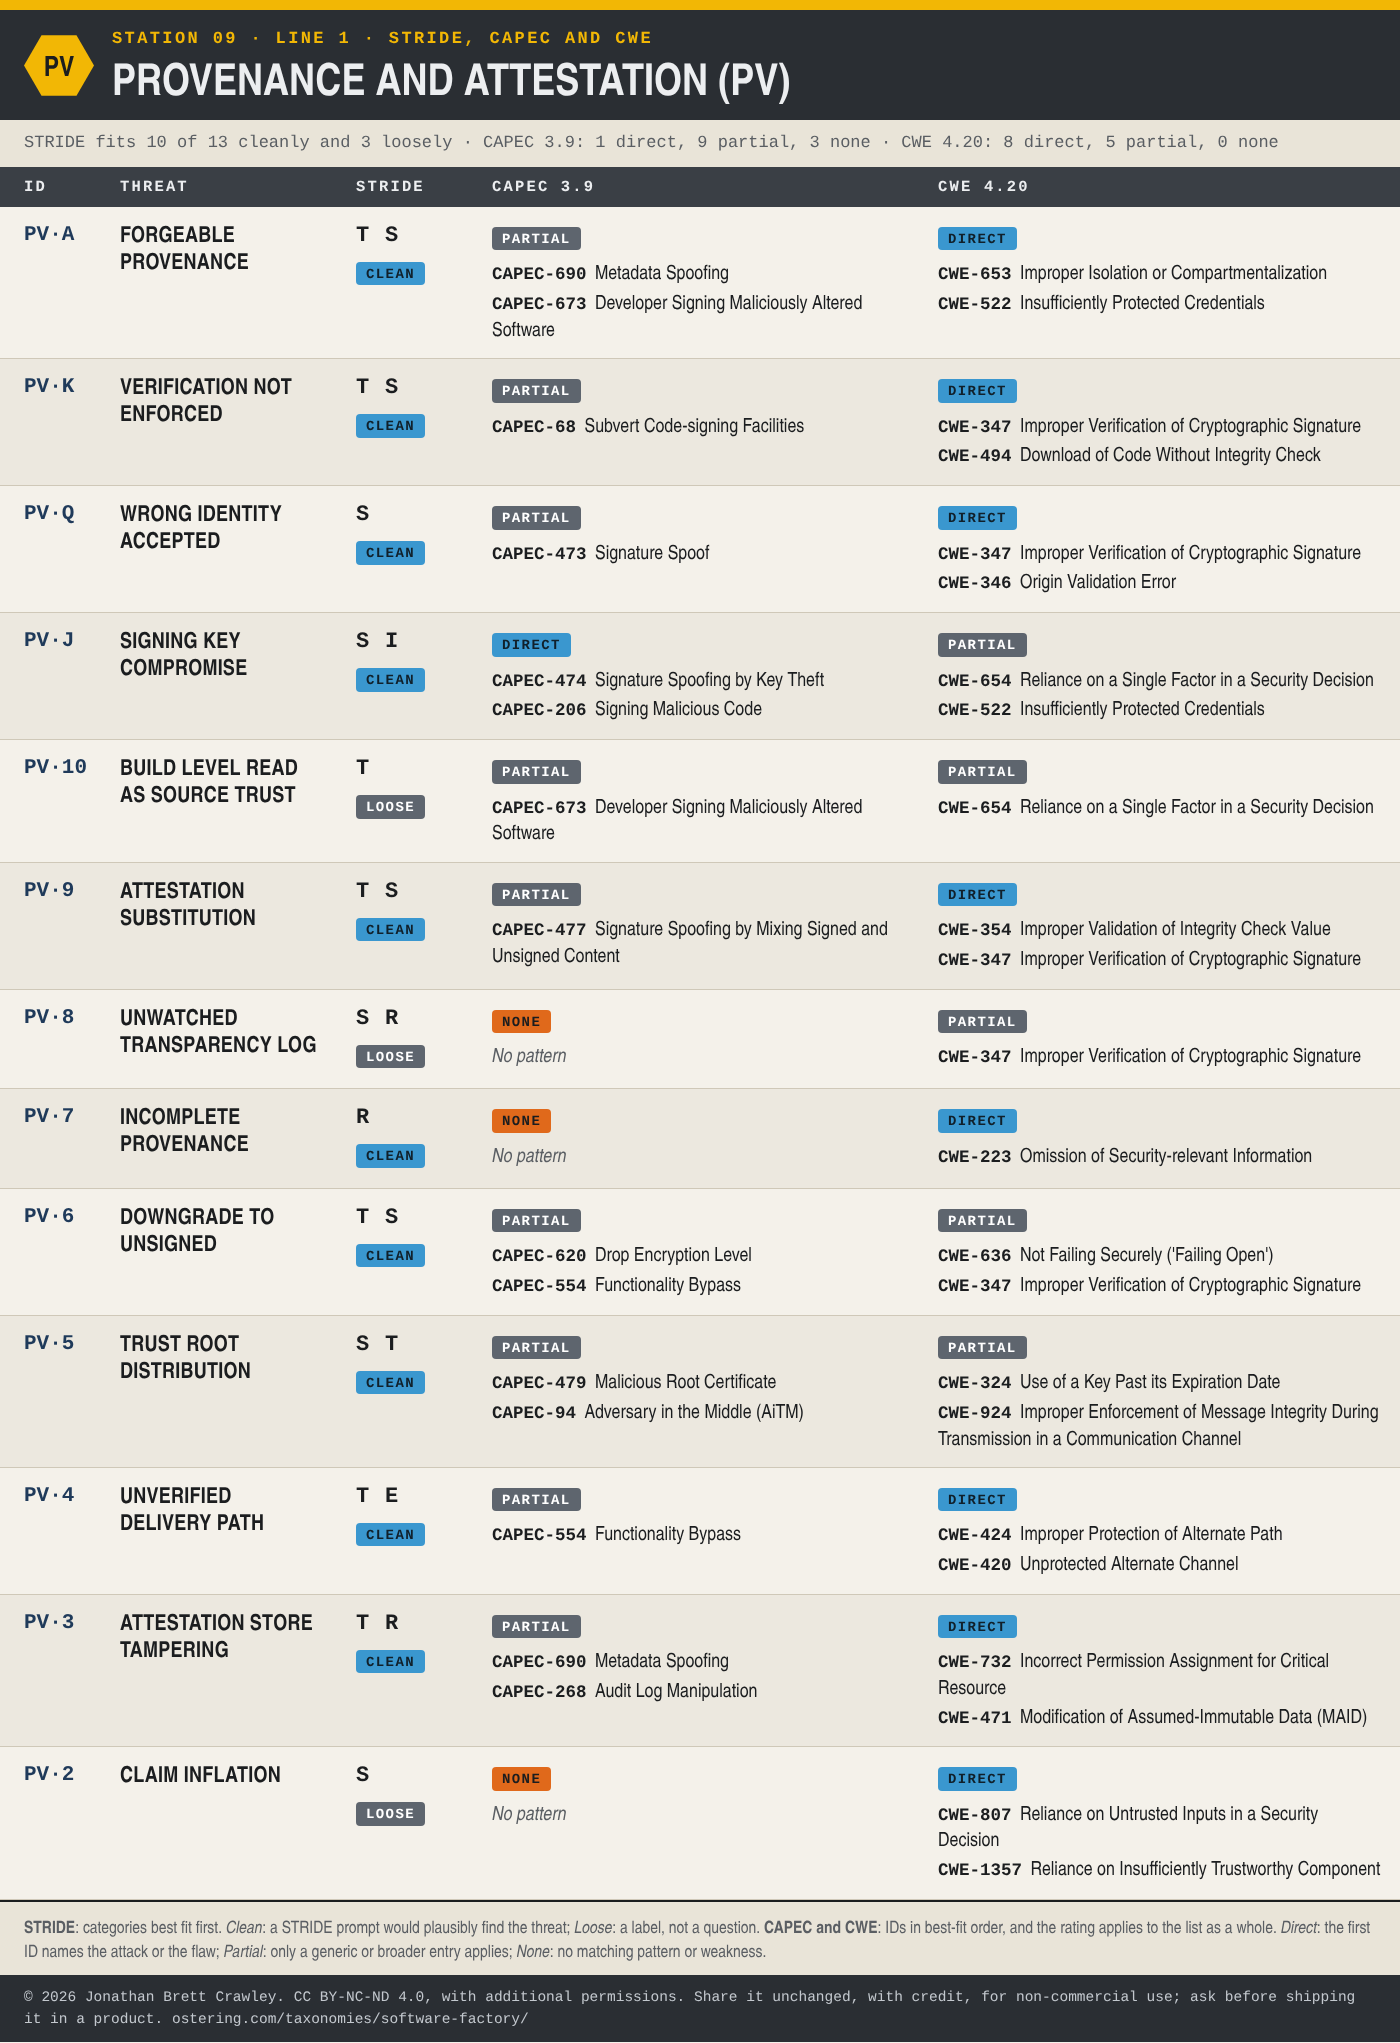
Of the 13 entries here, STRIDE fits 10 cleanly and 3 only loosely. CAPEC 3.9 has a pattern that describes 1 of them directly, only a generic parent pattern for 9, and nothing for 3. CWE 4.20 names the weakness directly for 8, has only a broader weakness for 5,. The table below gives the mapping entry by entry, with the names of the CAPEC patterns and CWE weaknesses; what the mapping shows across the whole taxonomy is in Mapping the Software Factory Threat Taxonomy to STRIDE, CAPEC and CWE. The Excel, SKOS and STIX downloads carry the same mapping as text.
← Scanners and Gates (SG) · Software factory overview · Registries (RG) →
© 2026 Jonathan Brett Crawley. Licensed under CC BY-NC-ND 4.0 with additional permissions: see the licence on the software factory overview.