SMTP (SM)
Taxonomies › Email infrastructure › SMTP
Layer 04 of 09 · 13 threats · prefix SM
SMTP accepts whatever identity a peer asserts and secures each hop only if both ends insist. These entries cover the MTA-to-MTA conversation: identity, relay, transport security and parsing.
Scope: The MTA-to-MTA conversation: identity, relay, transport security, parsing.
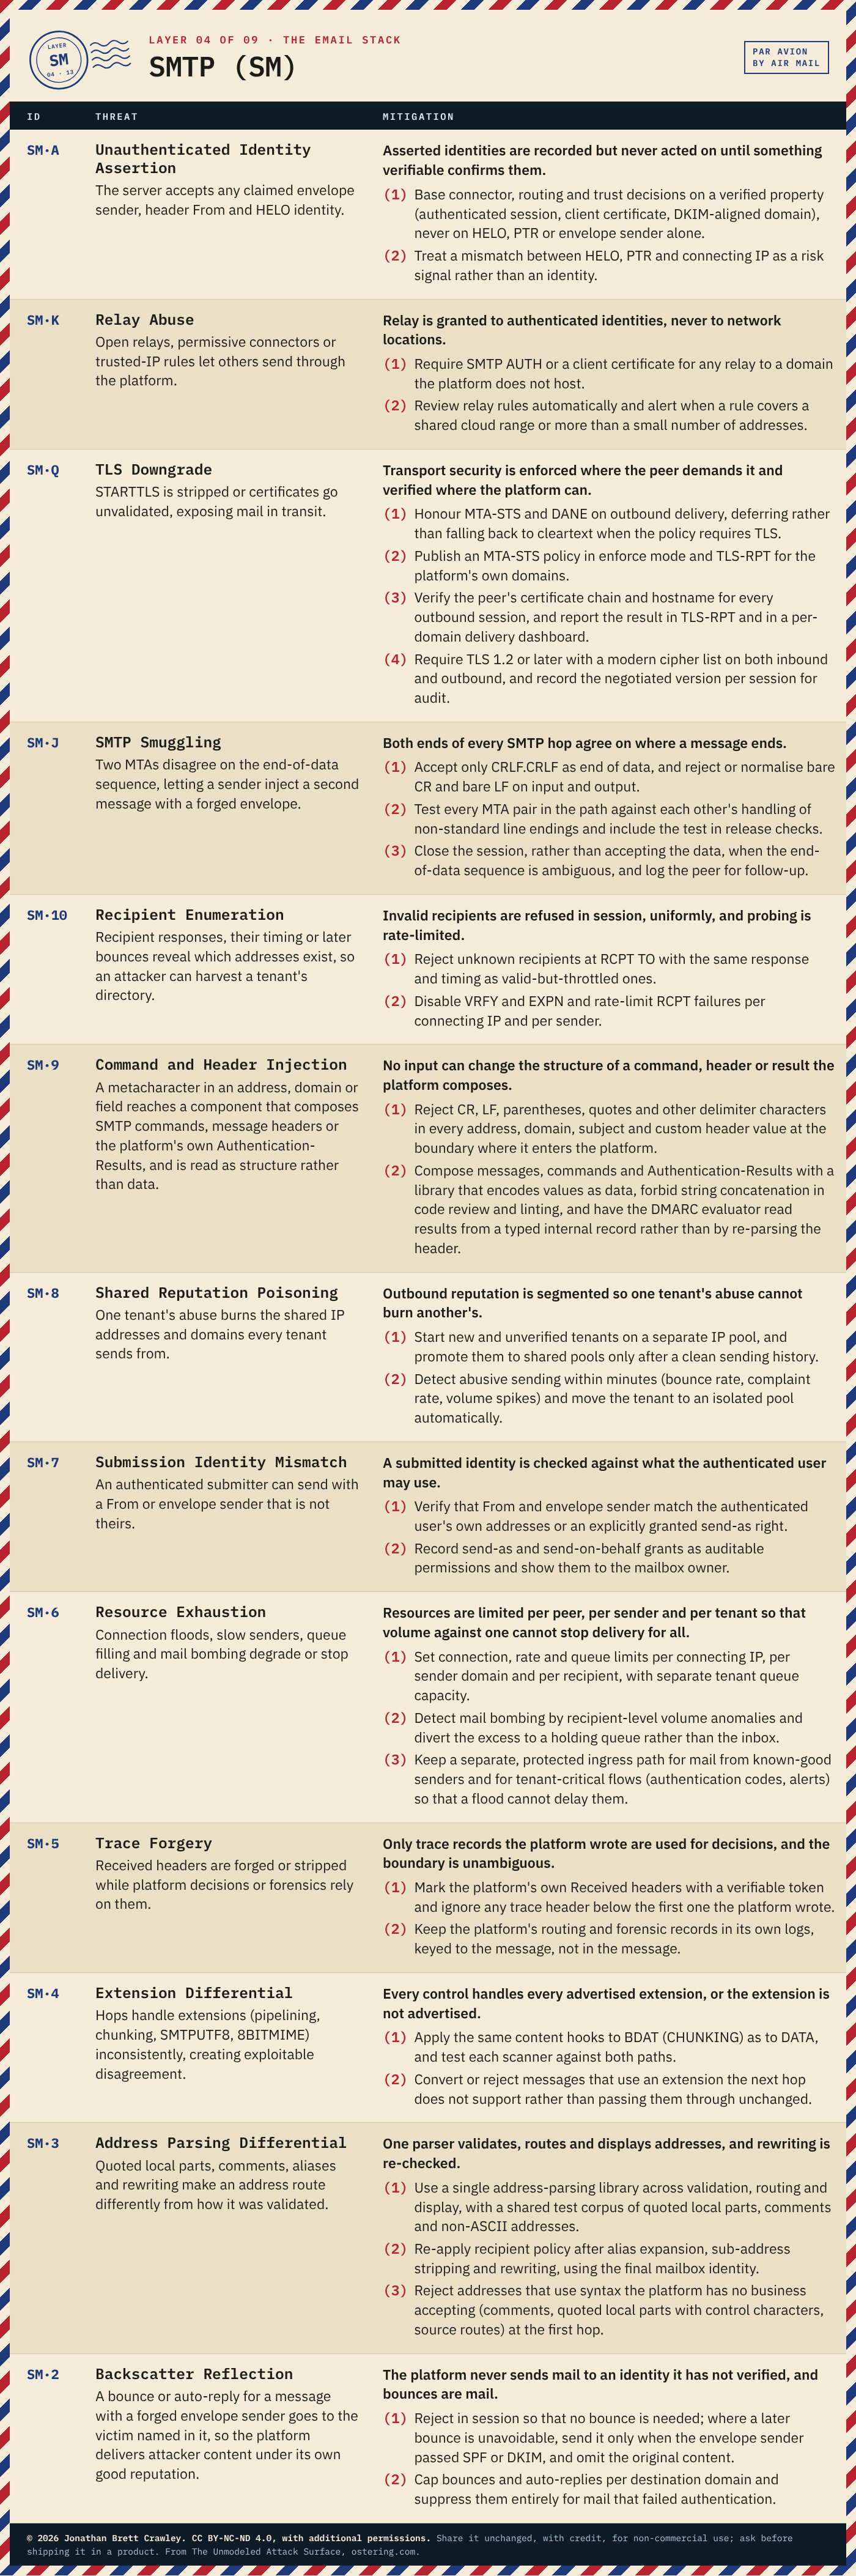
Text version: every entry on this page is in the PDF and Excel downloads on the overview page, where it can be searched and copied.
The threats
- SM·A Unauthenticated Identity Assertion
- SM·K Relay Abuse
- SM·Q TLS Downgrade
- SM·J SMTP Smuggling
- SM·10 Recipient Enumeration
- SM·9 Command and Header Injection
- SM·8 Shared Reputation Poisoning
- SM·7 Submission Identity Mismatch
- SM·6 Resource Exhaustion
- SM·5 Trace Forgery
- SM·4 Extension Differential
- SM·3 Address Parsing Differential
- SM·2 Backscatter Reflection
Where this layer touches others
- SMTP and delivery pipeline: SMTP is a single hop’s conversation. The pipeline is the composition of hops.
- Tenancy: Tenant Confusion (DP·7), Cross-Tenant Identity (AU·K) and Shared Reputation Poisoning (SM·8) each cover a different face of shared infrastructure (configuration, identity, reputation). Shared Infrastructure, Shared Fate (T2) is the structural hazard behind all three.
STRIDE, CAPEC and CWE
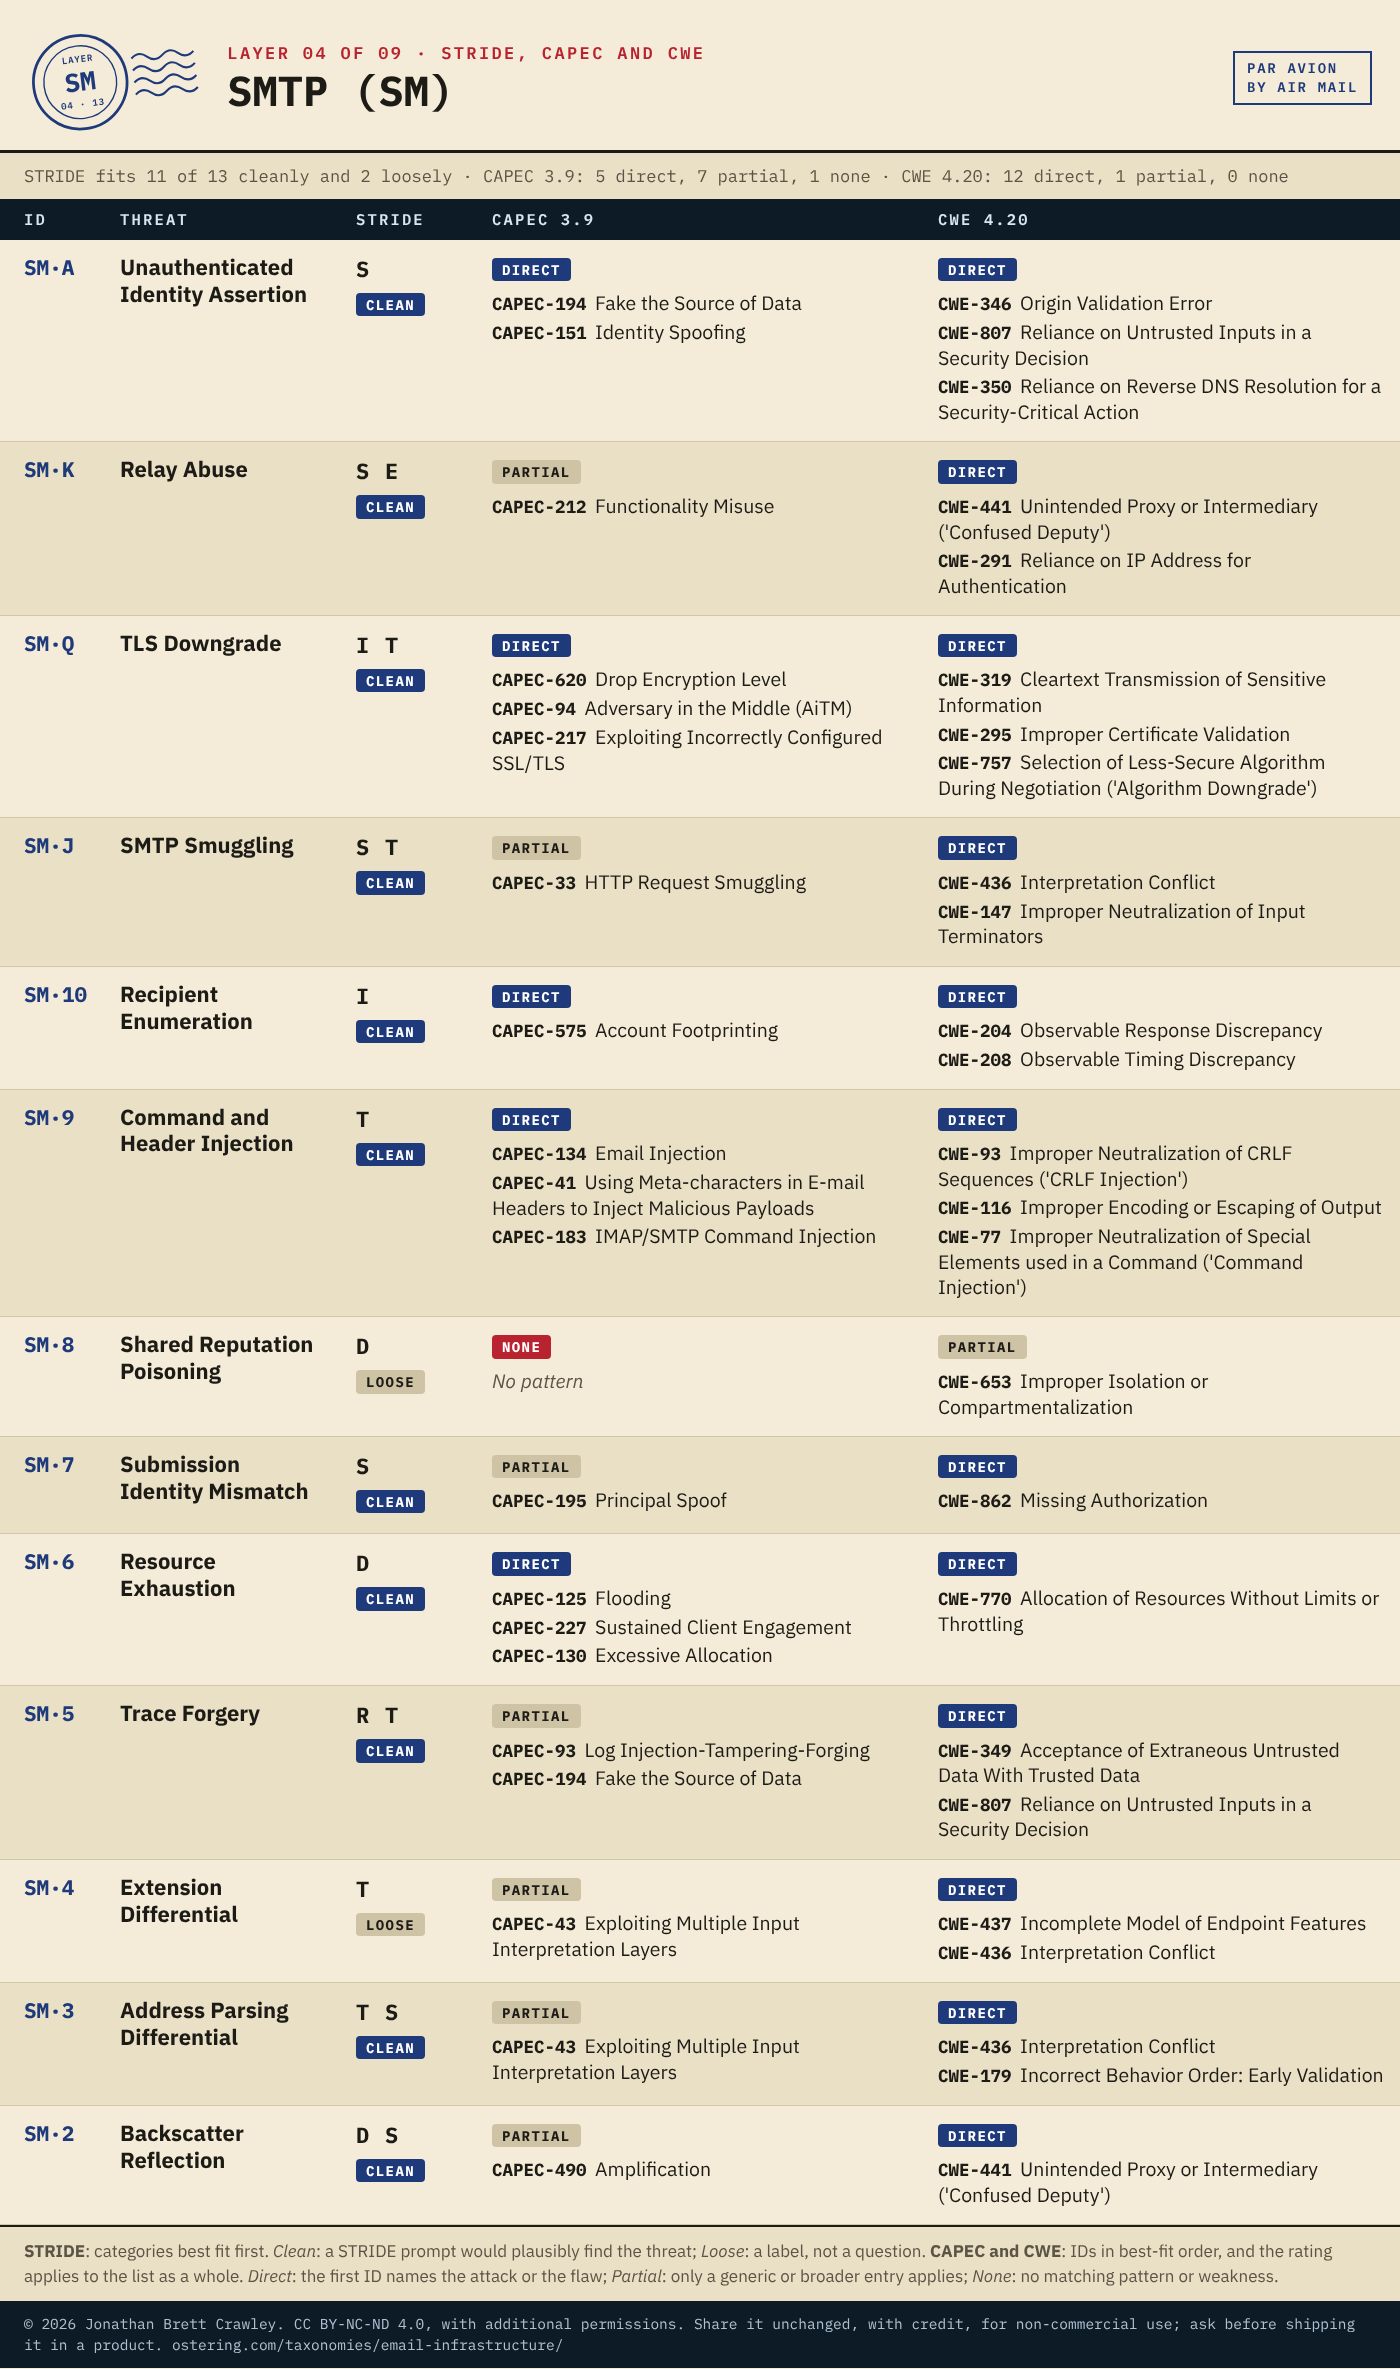
Of the 13 entries here, STRIDE fits 11 cleanly and 2 only loosely. CAPEC 3.9 has a pattern that describes 5 of them directly, only a generic parent pattern for 7, and nothing for 1. CWE 4.20 names the weakness directly for 12, has only a broader weakness for 1,. The table below gives the mapping entry by entry, with the names of the CAPEC patterns and CWE weaknesses; what the mapping shows across the whole taxonomy is in Mapping the Email Threat Taxonomy to STRIDE, CAPEC and CWE. The Excel, SKOS and STIX downloads carry the same mapping as text.
← Client protocols (CP) · Email infrastructure overview · MIME and S/MIME (MI) →
© 2026 Jonathan Brett Crawley. Licensed under CC BY-NC-ND 4.0 with additional permissions: see the licence on the email infrastructure overview.