Scanners and Gates (SG)
Taxonomies › Software factory › Scanners and Gates
Station 08 of 17 · Line 1, Source to Artifact · 13 threats · prefix SG
A scanner is privileged code that reads everything and decides what ships, so it is both a control and a target. These cards cover SAST, SCA, secrets, IaC, container, licence and DAST scanners, AI reviewers, and the gates that act on their results.
Scope: SAST, SCA, secrets, IaC, container, licence and DAST scanners; quality gates; policy checks.
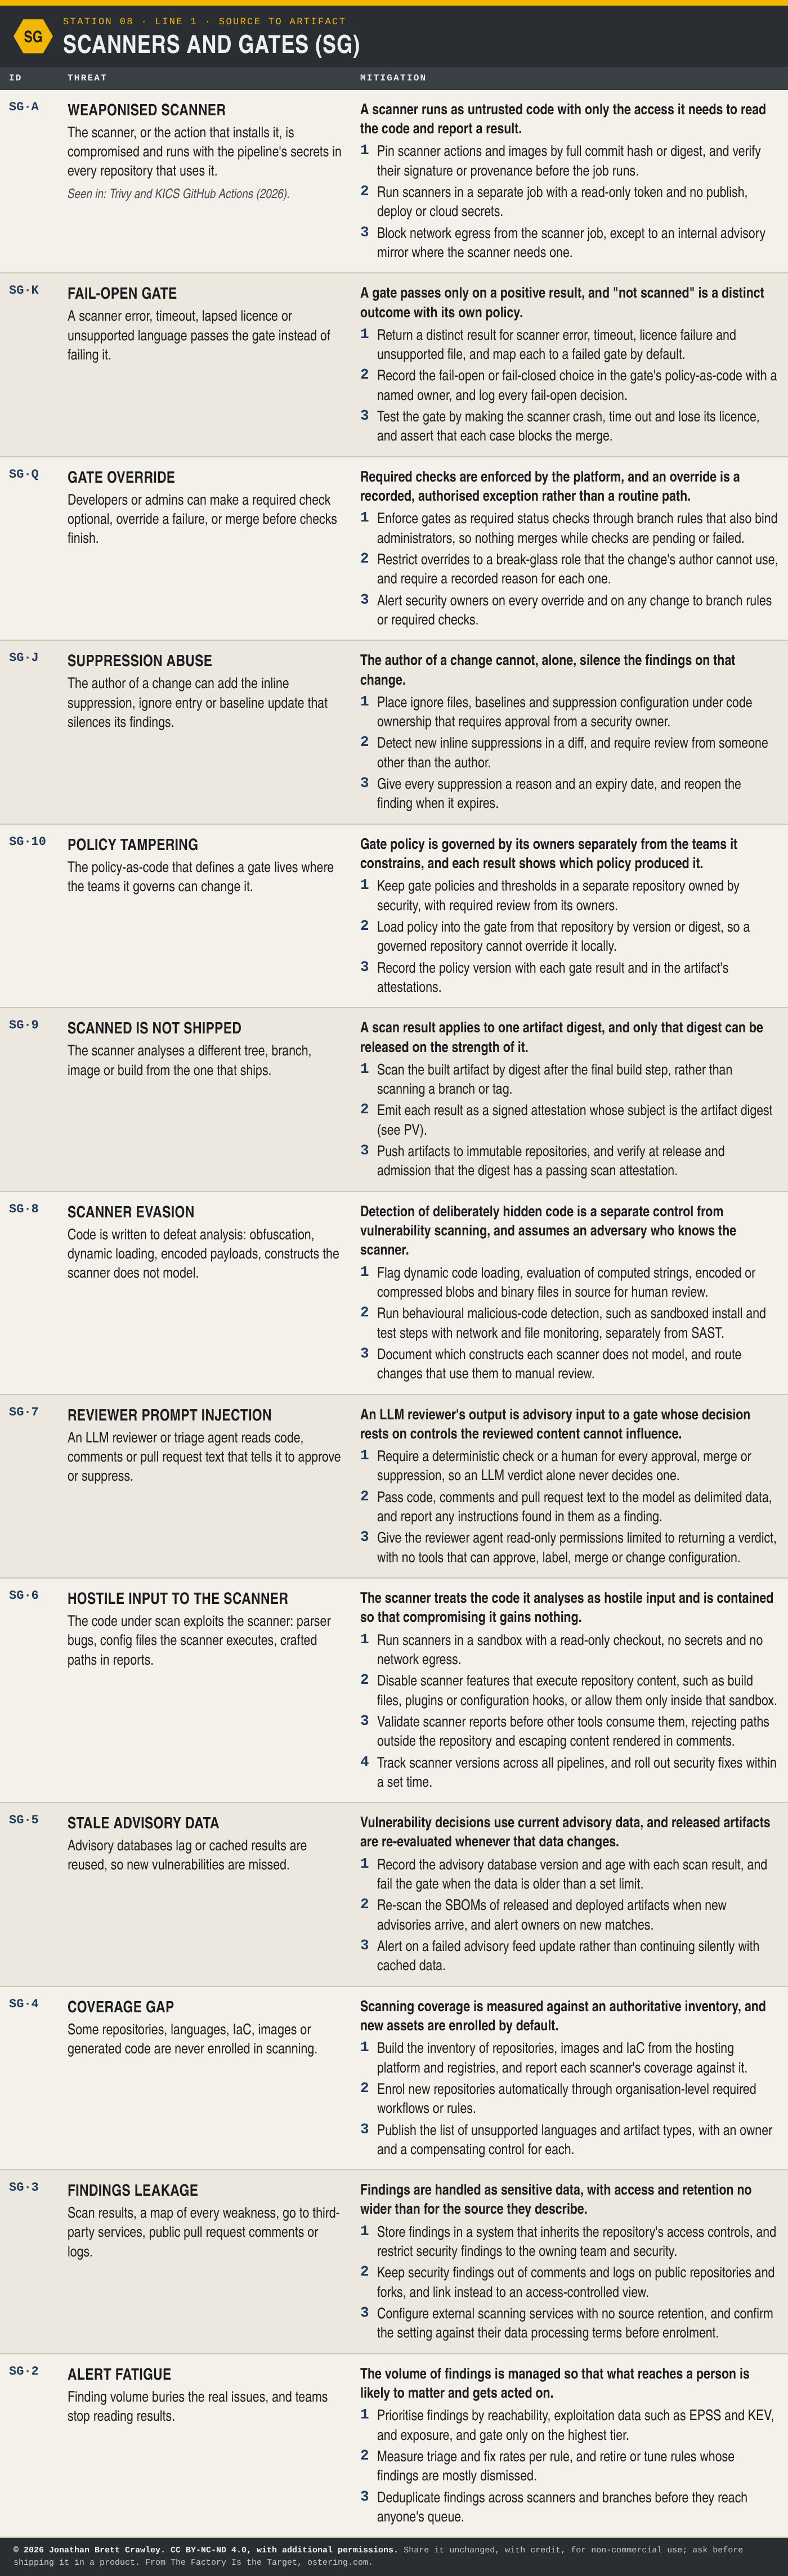
Text version: every entry on this page is in the PDF and Excel downloads on the overview page, where it can be searched and copied.
The threats
- SG·A Weaponised Scanner
- SG·K Fail-Open Gate
- SG·Q Gate Override
- SG·J Suppression Abuse
- SG·10 Policy Tampering
- SG·9 Scanned Is Not Shipped
- SG·8 Scanner Evasion
- SG·7 Reviewer Prompt Injection
- SG·6 Hostile Input to the Scanner
- SG·5 Stale Advisory Data
- SG·4 Coverage Gap
- SG·3 Findings Leakage
- SG·2 Alert Fatigue
Where this station touches others
- Scanners and Gates and Firewall and Quarantine: scanners judge what the factory makes; the firewall judges what comes in from outside. Both stations treat the control itself as a component that can fail or be attacked.
Seen in the wild
- SG·A Weaponised Scanner: Trivy and KICS GitHub Actions (2026).
Sources for each case are listed on the overview page.
STRIDE, CAPEC and CWE
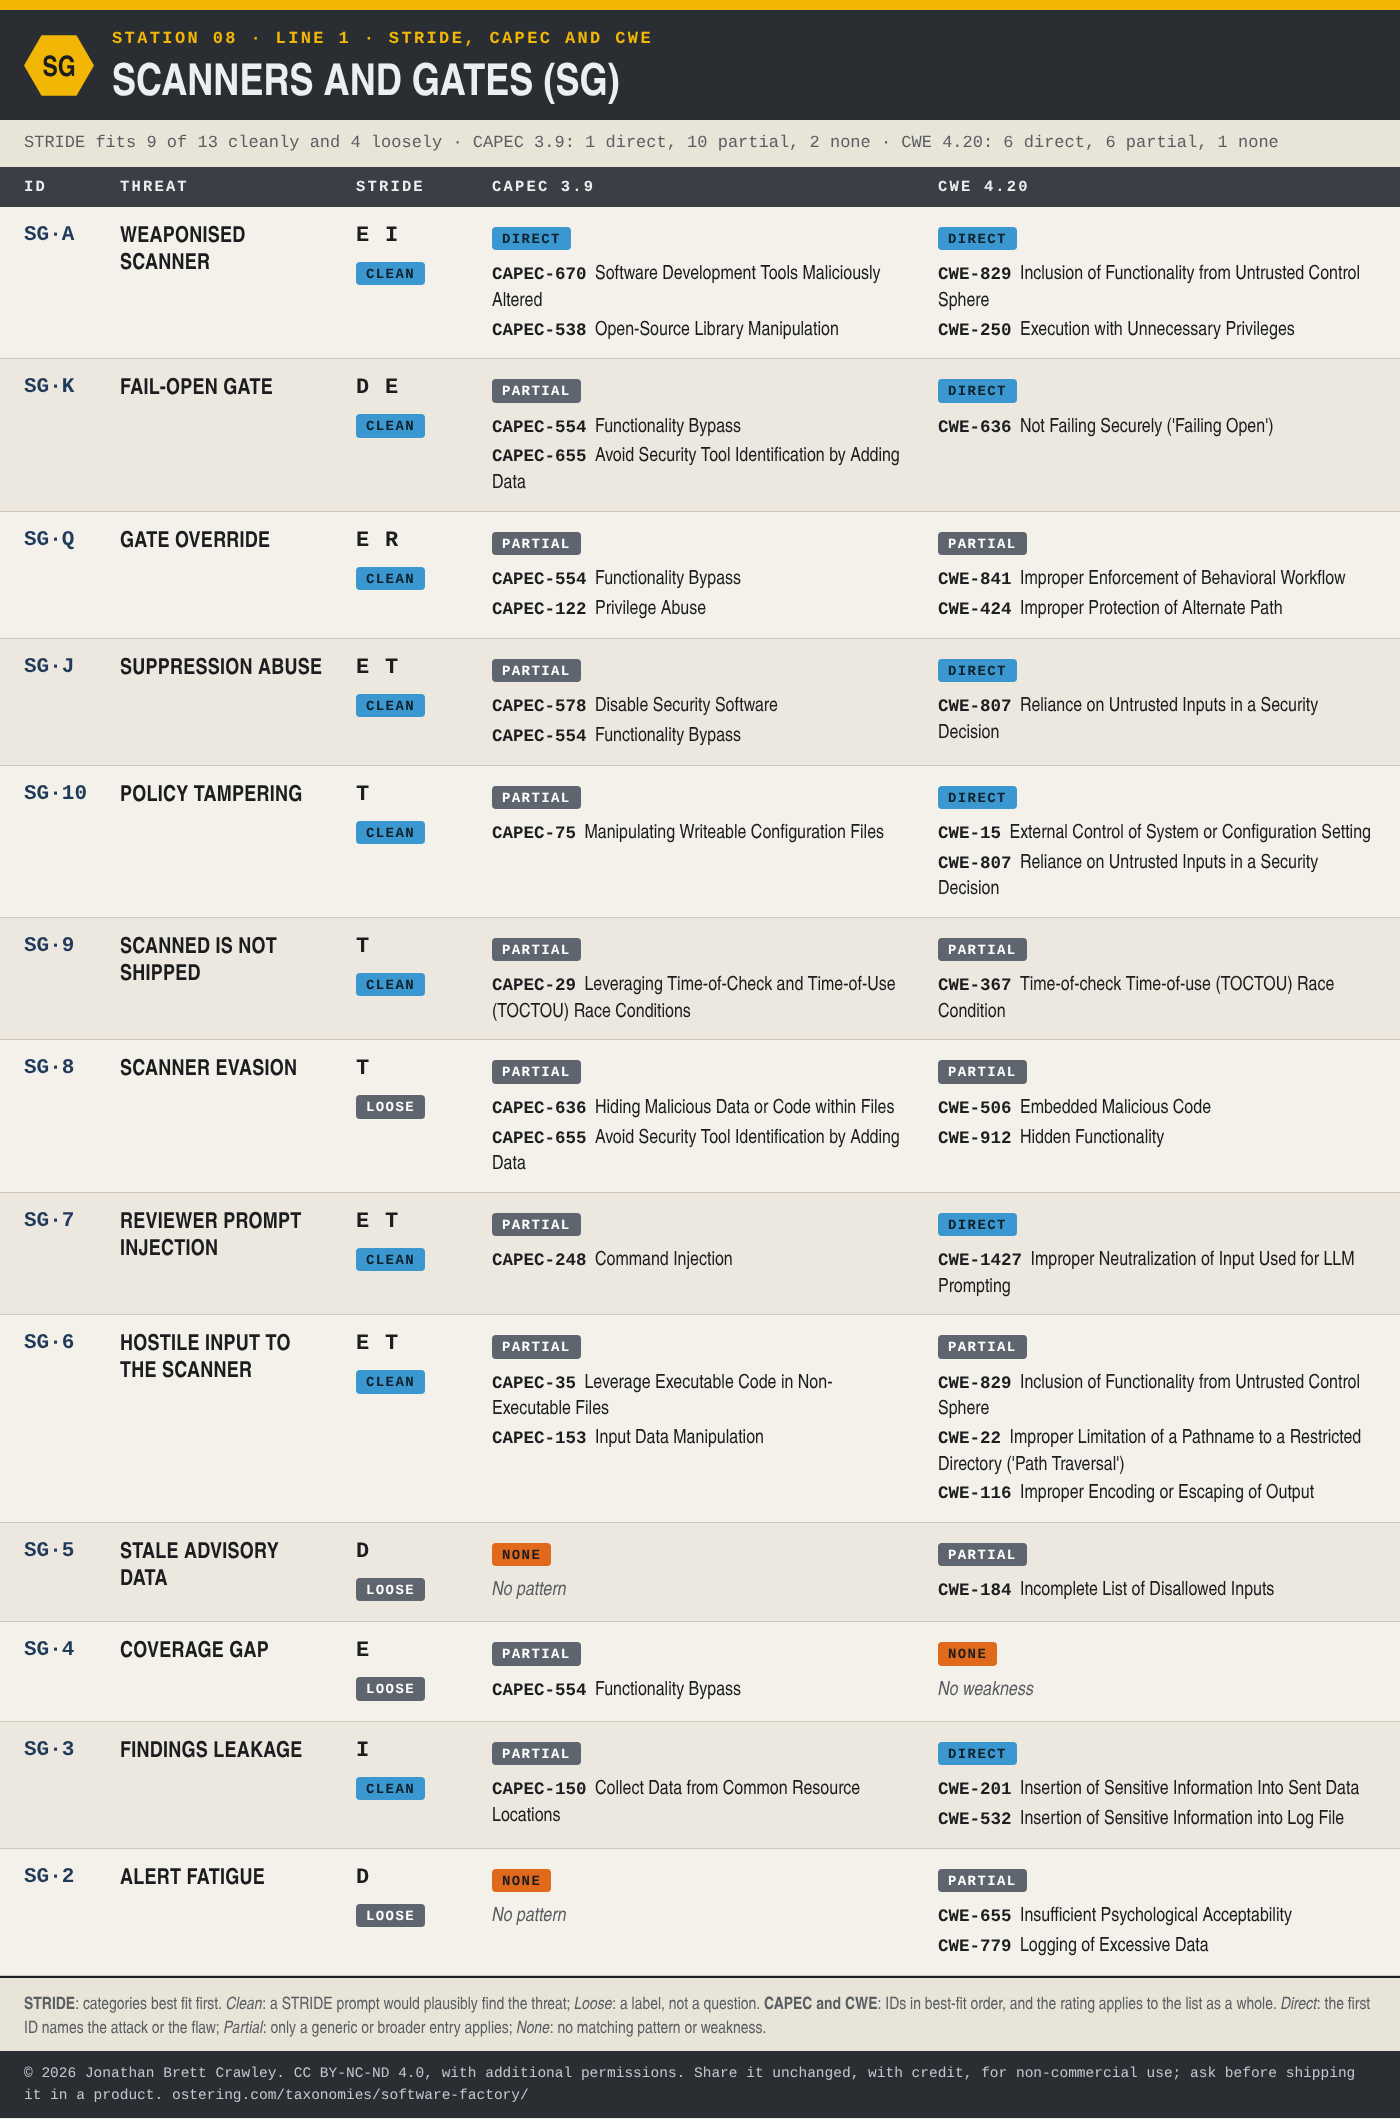
Of the 13 entries here, STRIDE fits 9 cleanly and 4 only loosely. CAPEC 3.9 has a pattern that describes 1 of them directly, only a generic parent pattern for 10, and nothing for 2. CWE 4.20 names the weakness directly for 6, has only a broader weakness for 6, and nothing for 1. The table below gives the mapping entry by entry, with the names of the CAPEC patterns and CWE weaknesses; what the mapping shows across the whole taxonomy is in Mapping the Software Factory Threat Taxonomy to STRIDE, CAPEC and CWE. The Excel, SKOS and STIX downloads carry the same mapping as text.
← Dependency Resolution (DR) · Software factory overview · Provenance and Attestation (PV) →
© 2026 Jonathan Brett Crawley. Licensed under CC BY-NC-ND 4.0 with additional permissions: see the licence on the software factory overview.