Container Runtime (RT)
Taxonomies › Software factory › Container Runtime
Station 15 of 17 · Line 2, Artifact to Runtime · 13 threats · prefix RT
A container is a set of kernel features, not a security boundary unless it is configured as one. These cards cover container runtimes, isolation, the host kernel and sandboxes.
Scope: Runtimes, isolation boundaries, the host kernel, sandboxes.
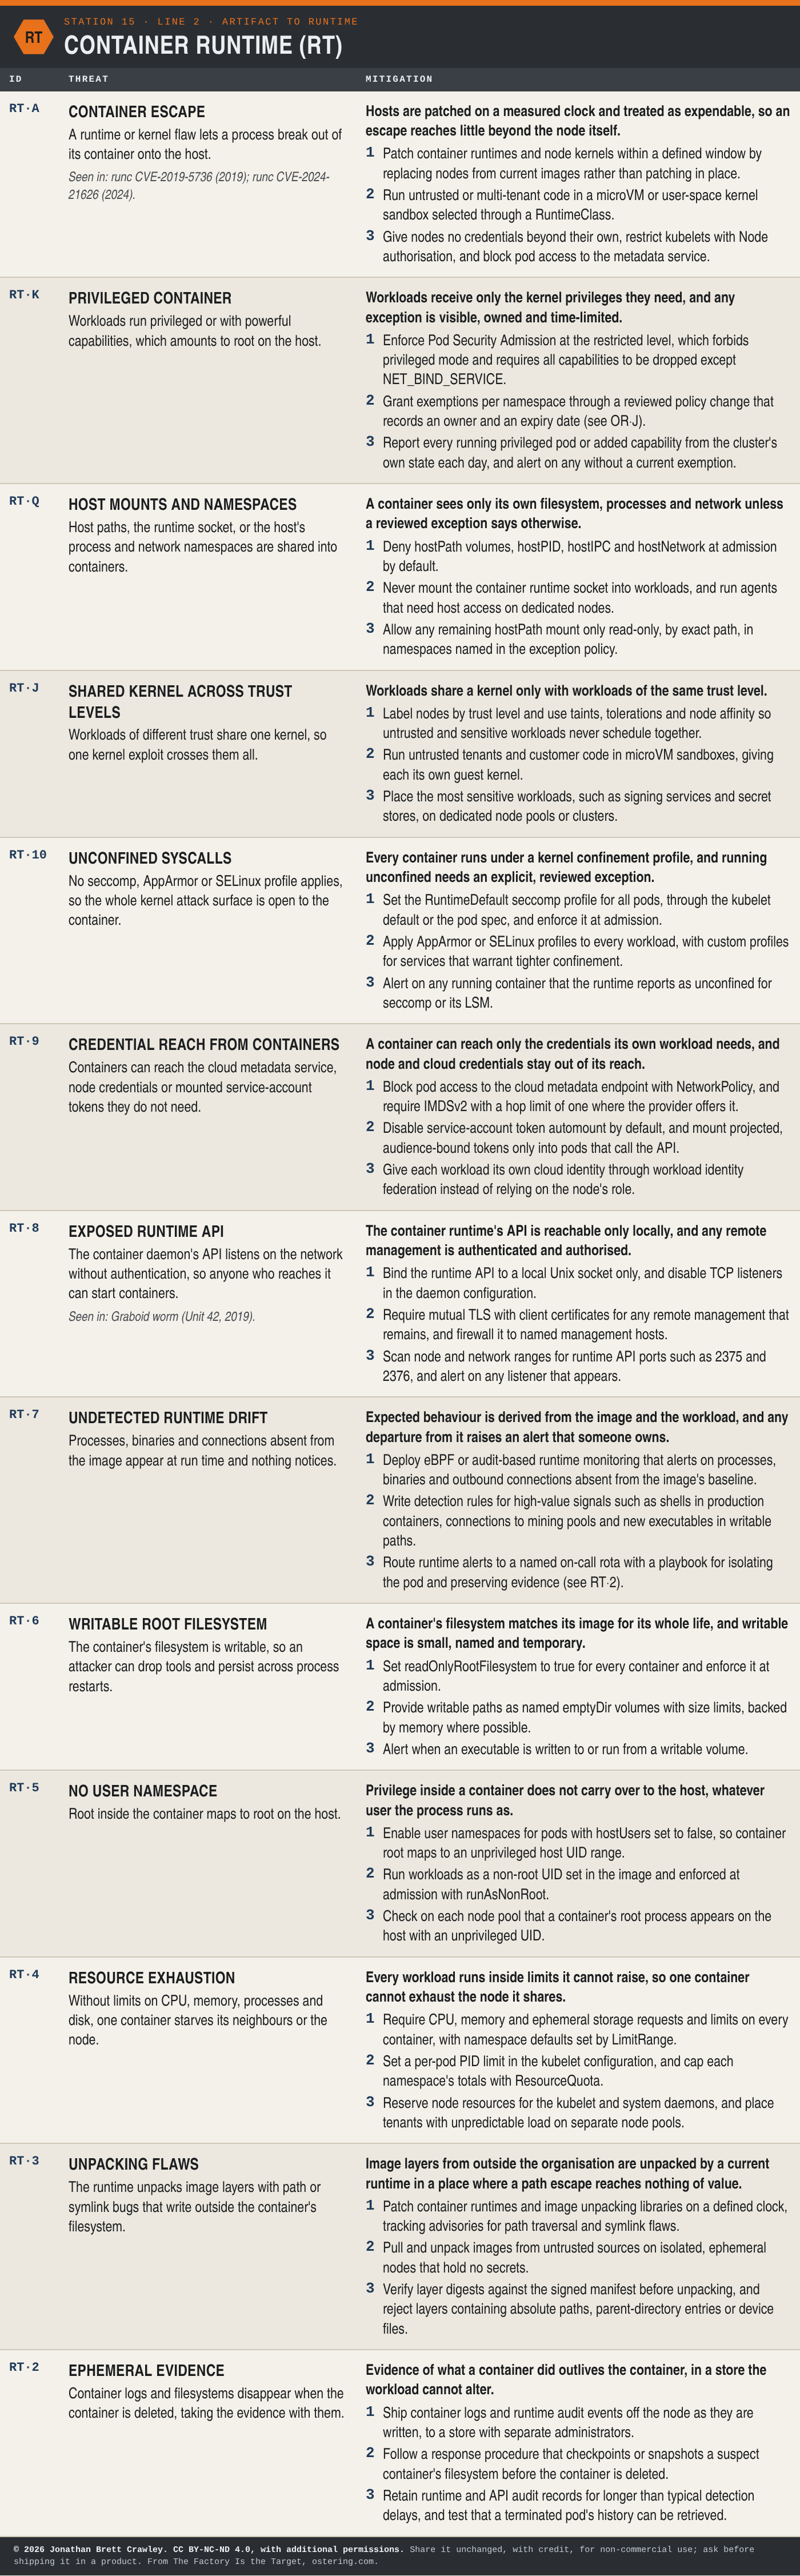
Text version: every entry on this page is in the PDF and Excel downloads on the overview page, where it can be searched and copied.
The threats
- RT·A Container Escape
- RT·K Privileged Container
- RT·Q Host Mounts and Namespaces
- RT·J Shared Kernel Across Trust Levels
- RT·10 Unconfined Syscalls
- RT·9 Credential Reach from Containers
- RT·8 Exposed Runtime API
- RT·7 Undetected Runtime Drift
- RT·6 Writable Root Filesystem
- RT·5 No User Namespace
- RT·4 Resource Exhaustion
- RT·3 Unpacking Flaws
- RT·2 Ephemeral Evidence
Where this station touches others
- Container Images and Container Runtime: the image is what is packaged; the runtime is how it is contained.
Seen in the wild
- RT·A Container Escape: runc CVE-2019-5736 (2019); runc CVE-2024-21626 (2024).
- RT·8 Exposed Runtime API: Graboid worm (Unit 42, 2019).
Sources for each case are listed on the overview page.
STRIDE, CAPEC and CWE
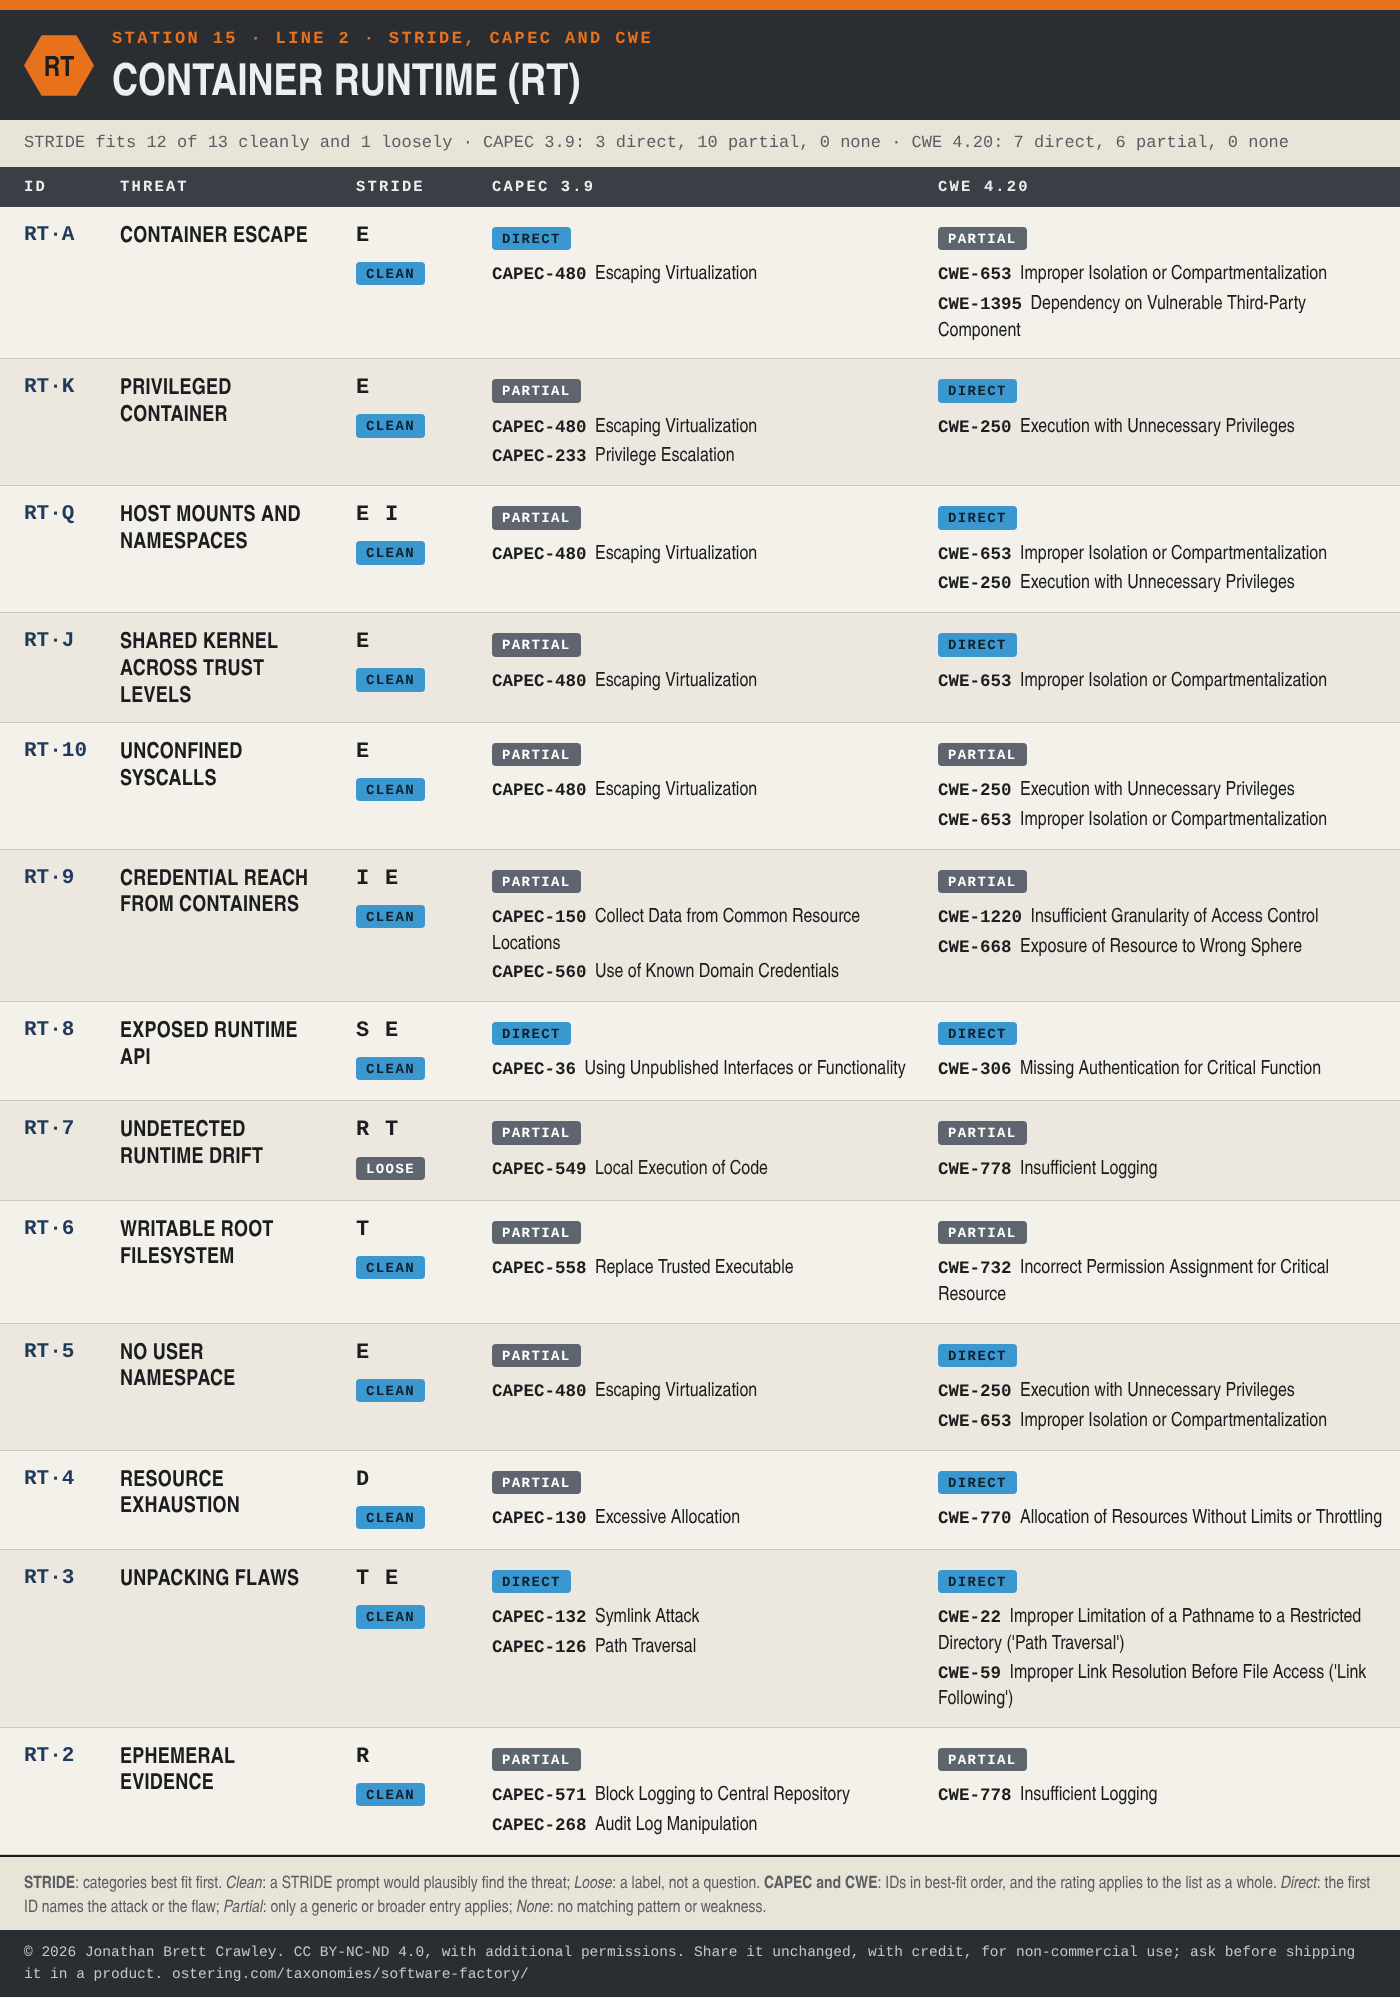
Of the 13 entries here, STRIDE fits 12 cleanly and 1 only loosely. CAPEC 3.9 has a pattern that describes 3 of them directly, and only a generic parent pattern for 10. CWE 4.20 names the weakness directly for 7, has only a broader weakness for 6,. The table below gives the mapping entry by entry, with the names of the CAPEC patterns and CWE weaknesses; what the mapping shows across the whole taxonomy is in Mapping the Software Factory Threat Taxonomy to STRIDE, CAPEC and CWE. The Excel, SKOS and STIX downloads carry the same mapping as text.
← Container Images (IM) · Software factory overview · Orchestration (OR) →
© 2026 Jonathan Brett Crawley. Licensed under CC BY-NC-ND 4.0 with additional permissions: see the licence on the software factory overview.