Registries (RG)
Taxonomies › Software factory › Registries
Station 10 of 17 · Line 2, Artifact to Runtime · 13 threats · prefix RG
A registry turns a name into bytes, and every consumer trusts that the name still means what it meant yesterday. These cards cover public package and image registries, internal artifact repositories, and the proxies and mirrors between them.
Scope: Public package and image registries, internal artifact repositories, proxies and mirrors.
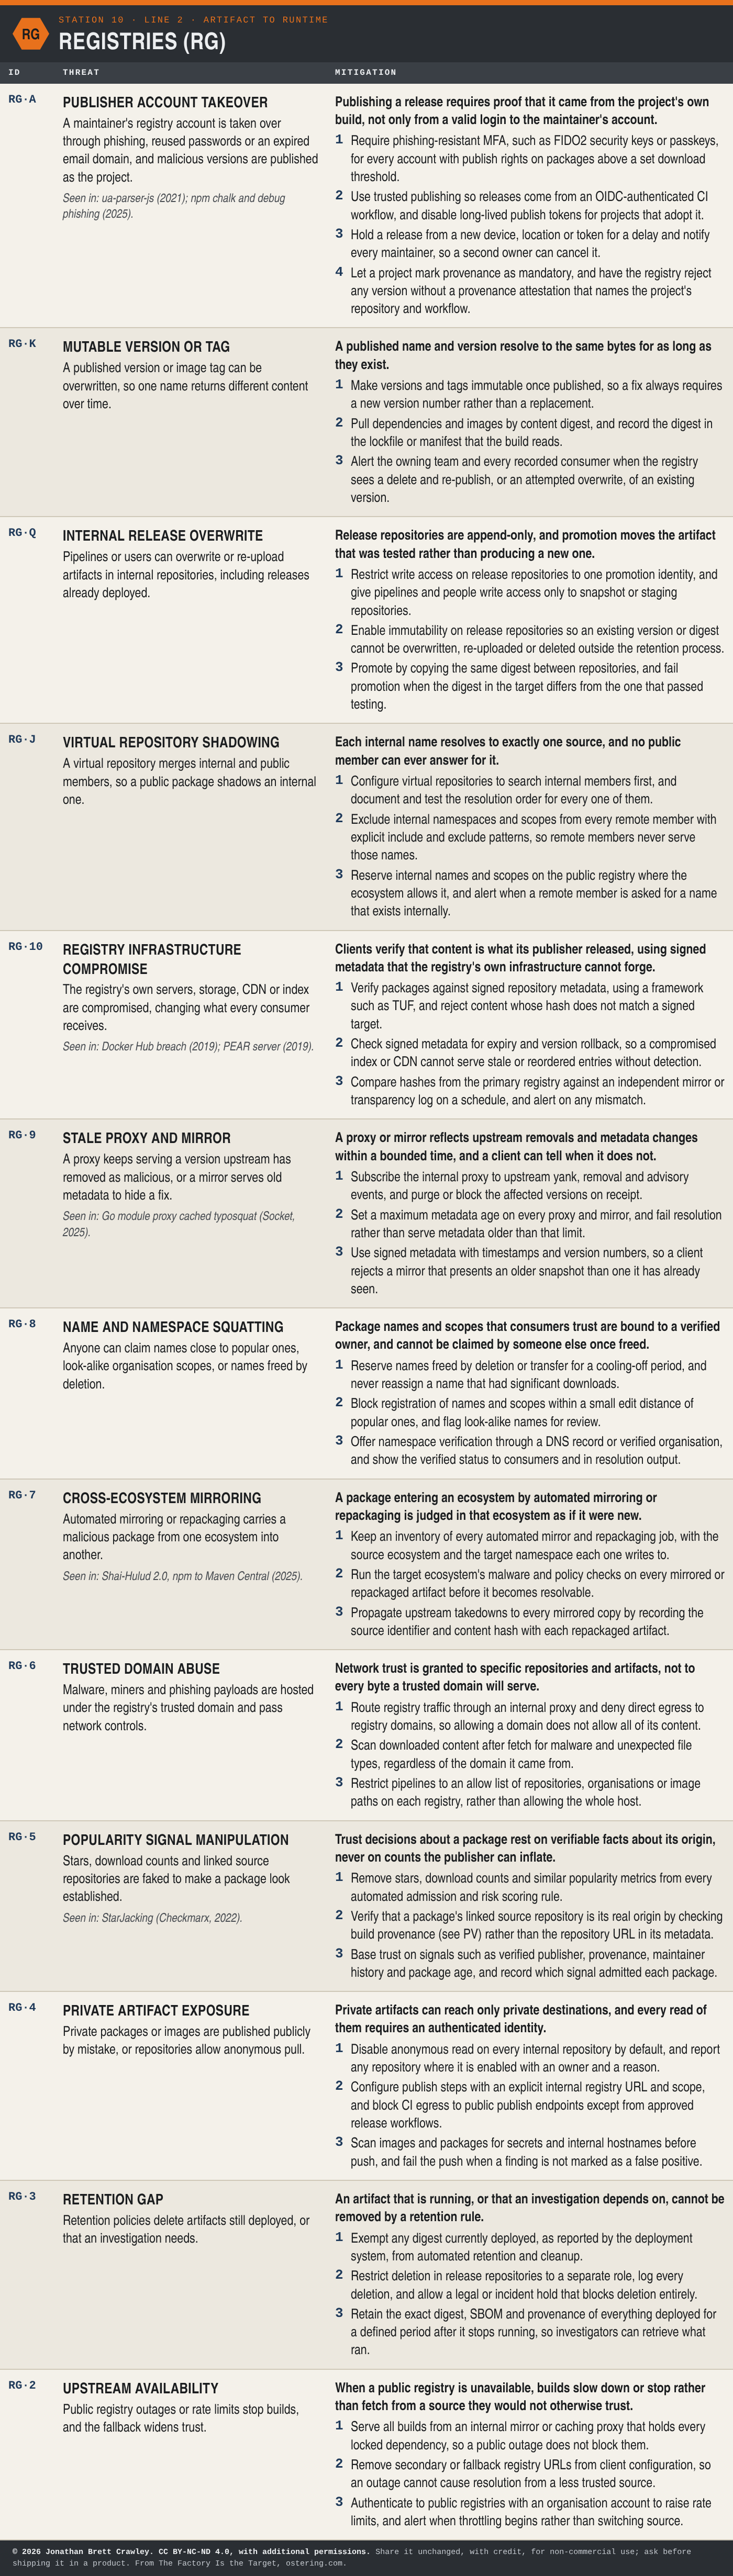
Text version: every entry on this page is in the PDF and Excel downloads on the overview page, where it can be searched and copied.
The threats
- RG·A Publisher Account Takeover
- RG·K Mutable Version or Tag
- RG·Q Internal Release Overwrite
- RG·J Virtual Repository Shadowing
- RG·10 Registry Infrastructure Compromise
- RG·9 Stale Proxy and Mirror
- RG·8 Name and Namespace Squatting
- RG·7 Cross-Ecosystem Mirroring
- RG·6 Trusted Domain Abuse
- RG·5 Popularity Signal Manipulation
- RG·4 Private Artifact Exposure
- RG·3 Retention Gap
- RG·2 Upstream Availability
Where this station touches others
- Registries and Firewall and Quarantine: the registry is where components live; the firewall decides which of them reach a build.
Seen in the wild
- RG·A Publisher Account Takeover: ua-parser-js (2021); npm chalk and debug phishing (2025).
- RG·10 Registry Infrastructure Compromise: Docker Hub breach (2019); PEAR server (2019).
- RG·9 Stale Proxy and Mirror: Go module proxy cached typosquat (Socket, 2025).
- RG·7 Cross-Ecosystem Mirroring: Shai-Hulud 2.0, npm to Maven Central (2025).
- RG·5 Popularity Signal Manipulation: StarJacking (Checkmarx, 2022).
Sources for each case are listed on the overview page.
STRIDE, CAPEC and CWE
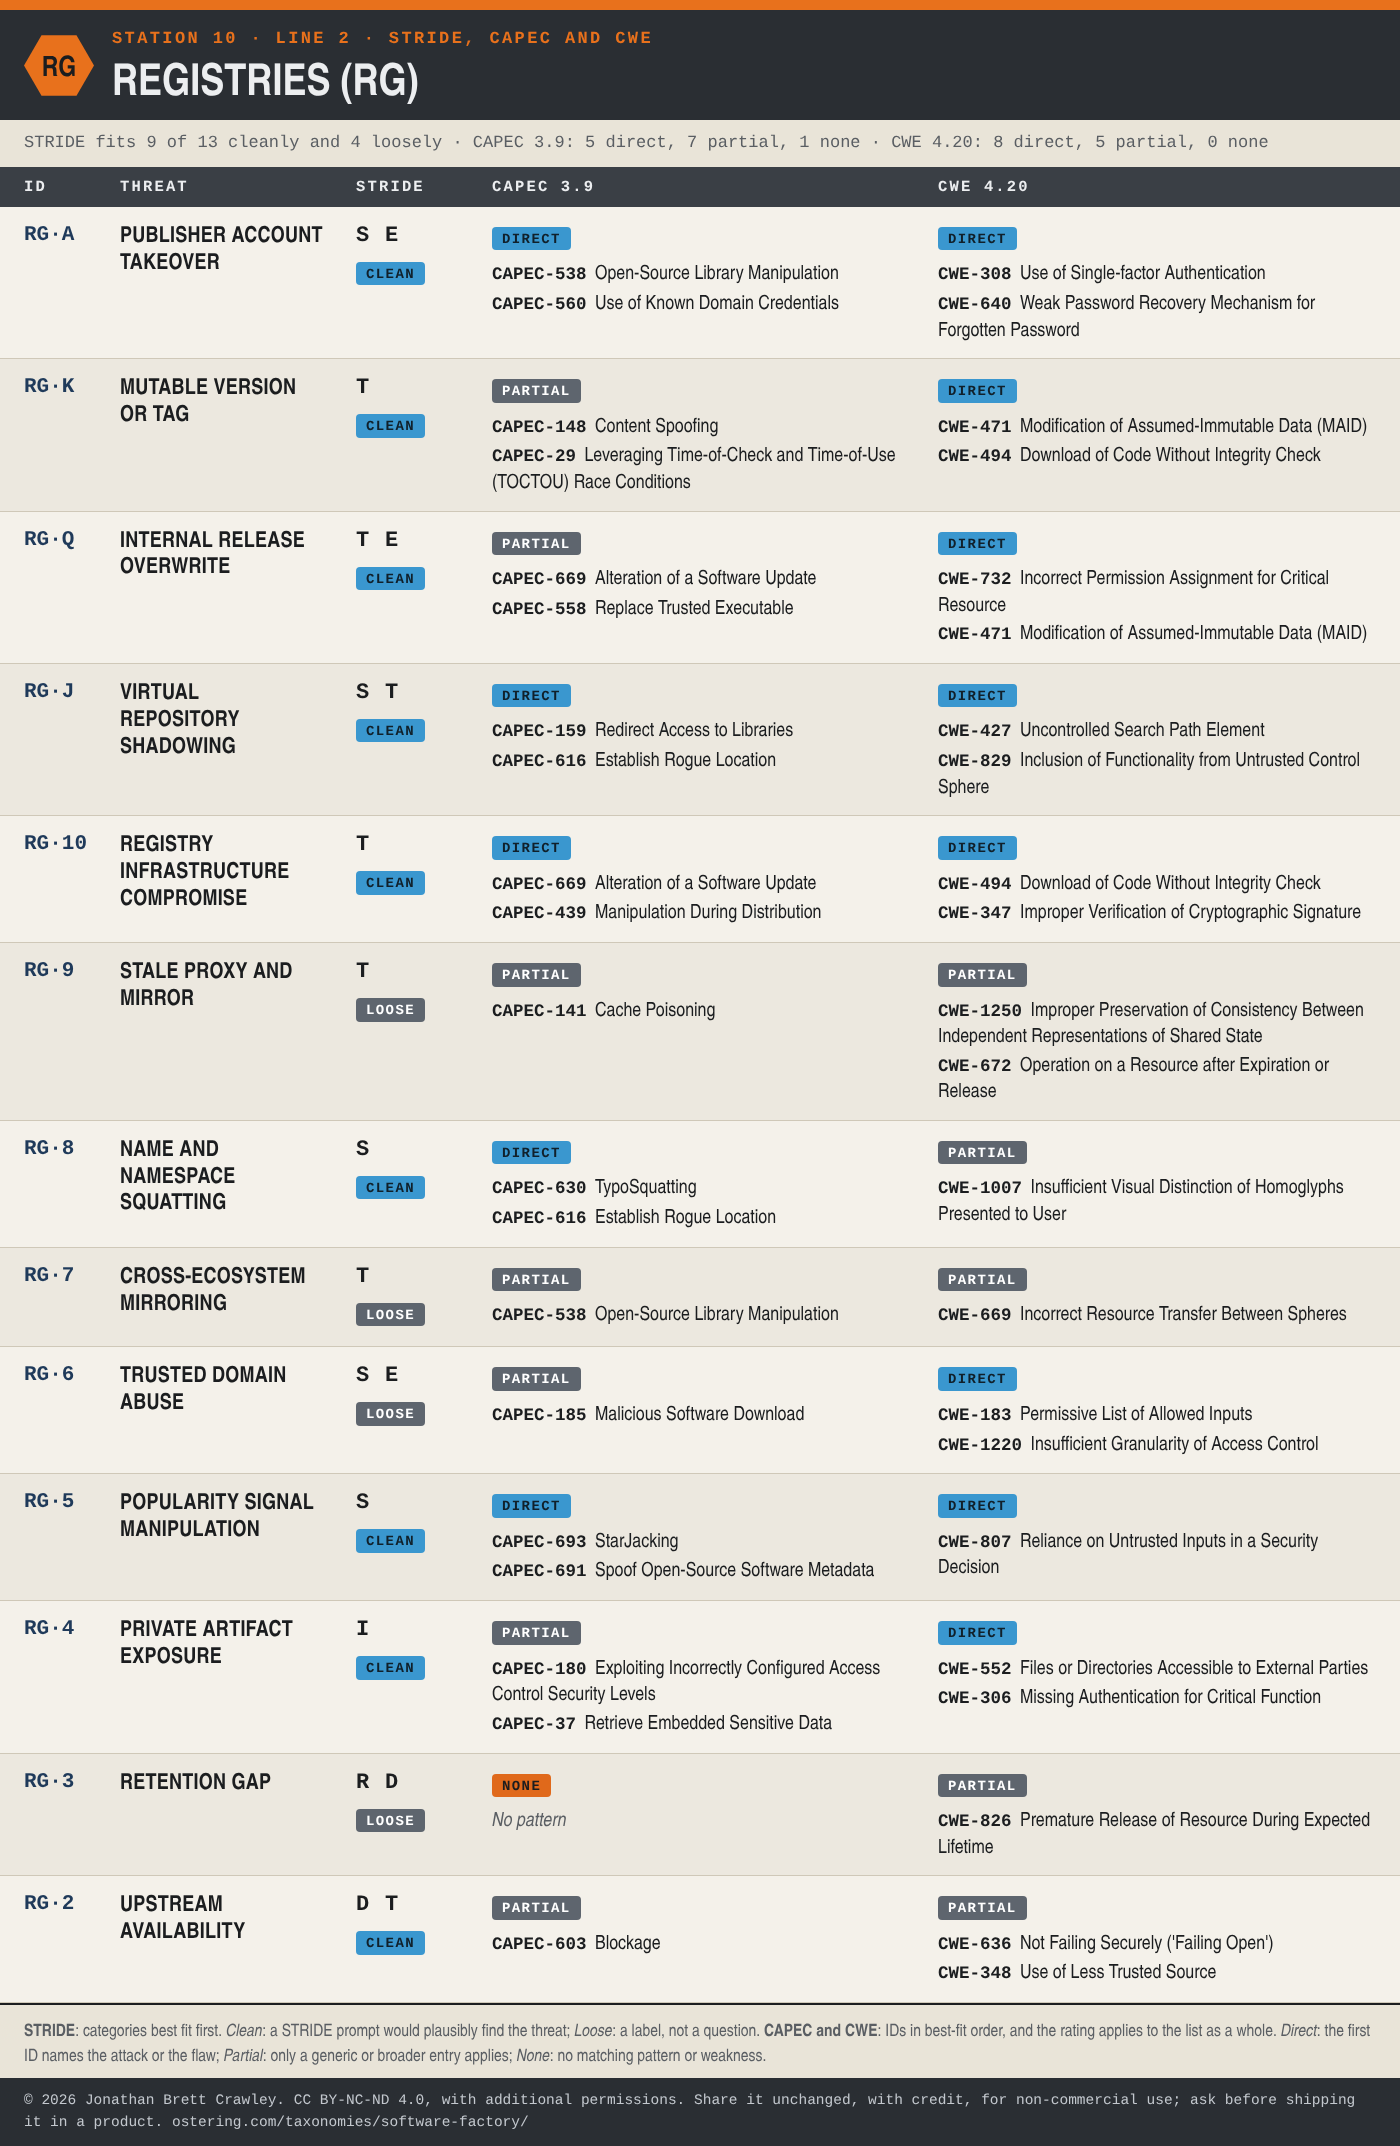
Of the 13 entries here, STRIDE fits 9 cleanly and 4 only loosely. CAPEC 3.9 has a pattern that describes 5 of them directly, only a generic parent pattern for 7, and nothing for 1. CWE 4.20 names the weakness directly for 8, has only a broader weakness for 5,. The table below gives the mapping entry by entry, with the names of the CAPEC patterns and CWE weaknesses; what the mapping shows across the whole taxonomy is in Mapping the Software Factory Threat Taxonomy to STRIDE, CAPEC and CWE. The Excel, SKOS and STIX downloads carry the same mapping as text.
← Provenance and Attestation (PV) · Software factory overview · Firewall and Quarantine (FW) →
© 2026 Jonathan Brett Crawley. Licensed under CC BY-NC-ND 4.0 with additional permissions: see the licence on the software factory overview.