Build Systems (BS)
Taxonomies › Software factory › Build Systems
Station 06 of 17 · Line 1, Source to Artifact · 13 threats · prefix BS
A build should turn exactly the reviewed source into exactly one output, and every threat here breaks that link. These cards cover build tools, build scripts, plugins, compilers and toolchains, and remote caches and executors.
Scope: Make, Maven, Gradle, Bazel, compilers, toolchains, build plugins, remote cache and execution.
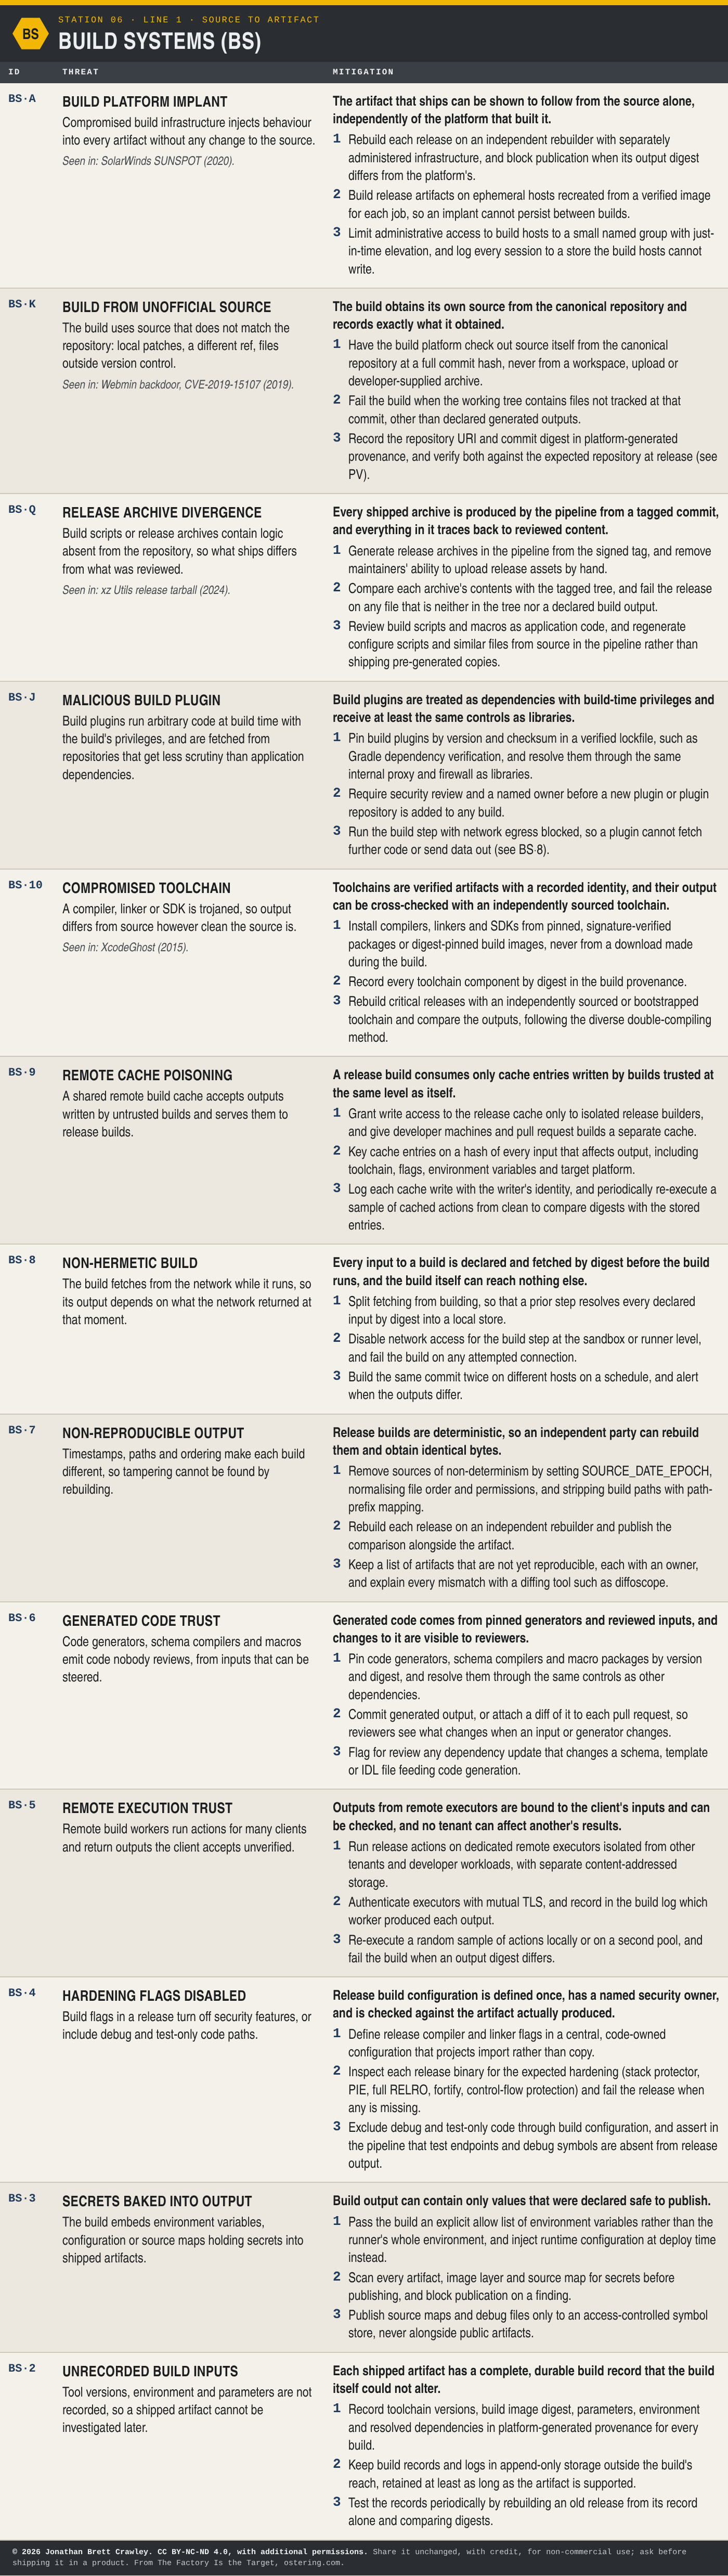
Text version: every entry on this page is in the PDF and Excel downloads on the overview page, where it can be searched and copied.
The threats
- BS·A Build Platform Implant
- BS·K Build from Unofficial Source
- BS·Q Release Archive Divergence
- BS·J Malicious Build Plugin
- BS·10 Compromised Toolchain
- BS·9 Remote Cache Poisoning
- BS·8 Non-Hermetic Build
- BS·7 Non-Reproducible Output
- BS·6 Generated Code Trust
- BS·5 Remote Execution Trust
- BS·4 Hardening Flags Disabled
- BS·3 Secrets Baked into Output
- BS·2 Unrecorded Build Inputs
Where this station touches others
- Build Systems and Dependency Resolution: the build system runs the build logic and fetches its own plugins; resolution chooses the application’s components.
Seen in the wild
- BS·A Build Platform Implant: SolarWinds SUNSPOT (2020).
- BS·K Build from Unofficial Source: Webmin backdoor, CVE-2019-15107 (2019).
- BS·Q Release Archive Divergence: xz Utils release tarball (2024).
- BS·10 Compromised Toolchain: XcodeGhost (2015).
Sources for each case are listed on the overview page.
STRIDE, CAPEC and CWE
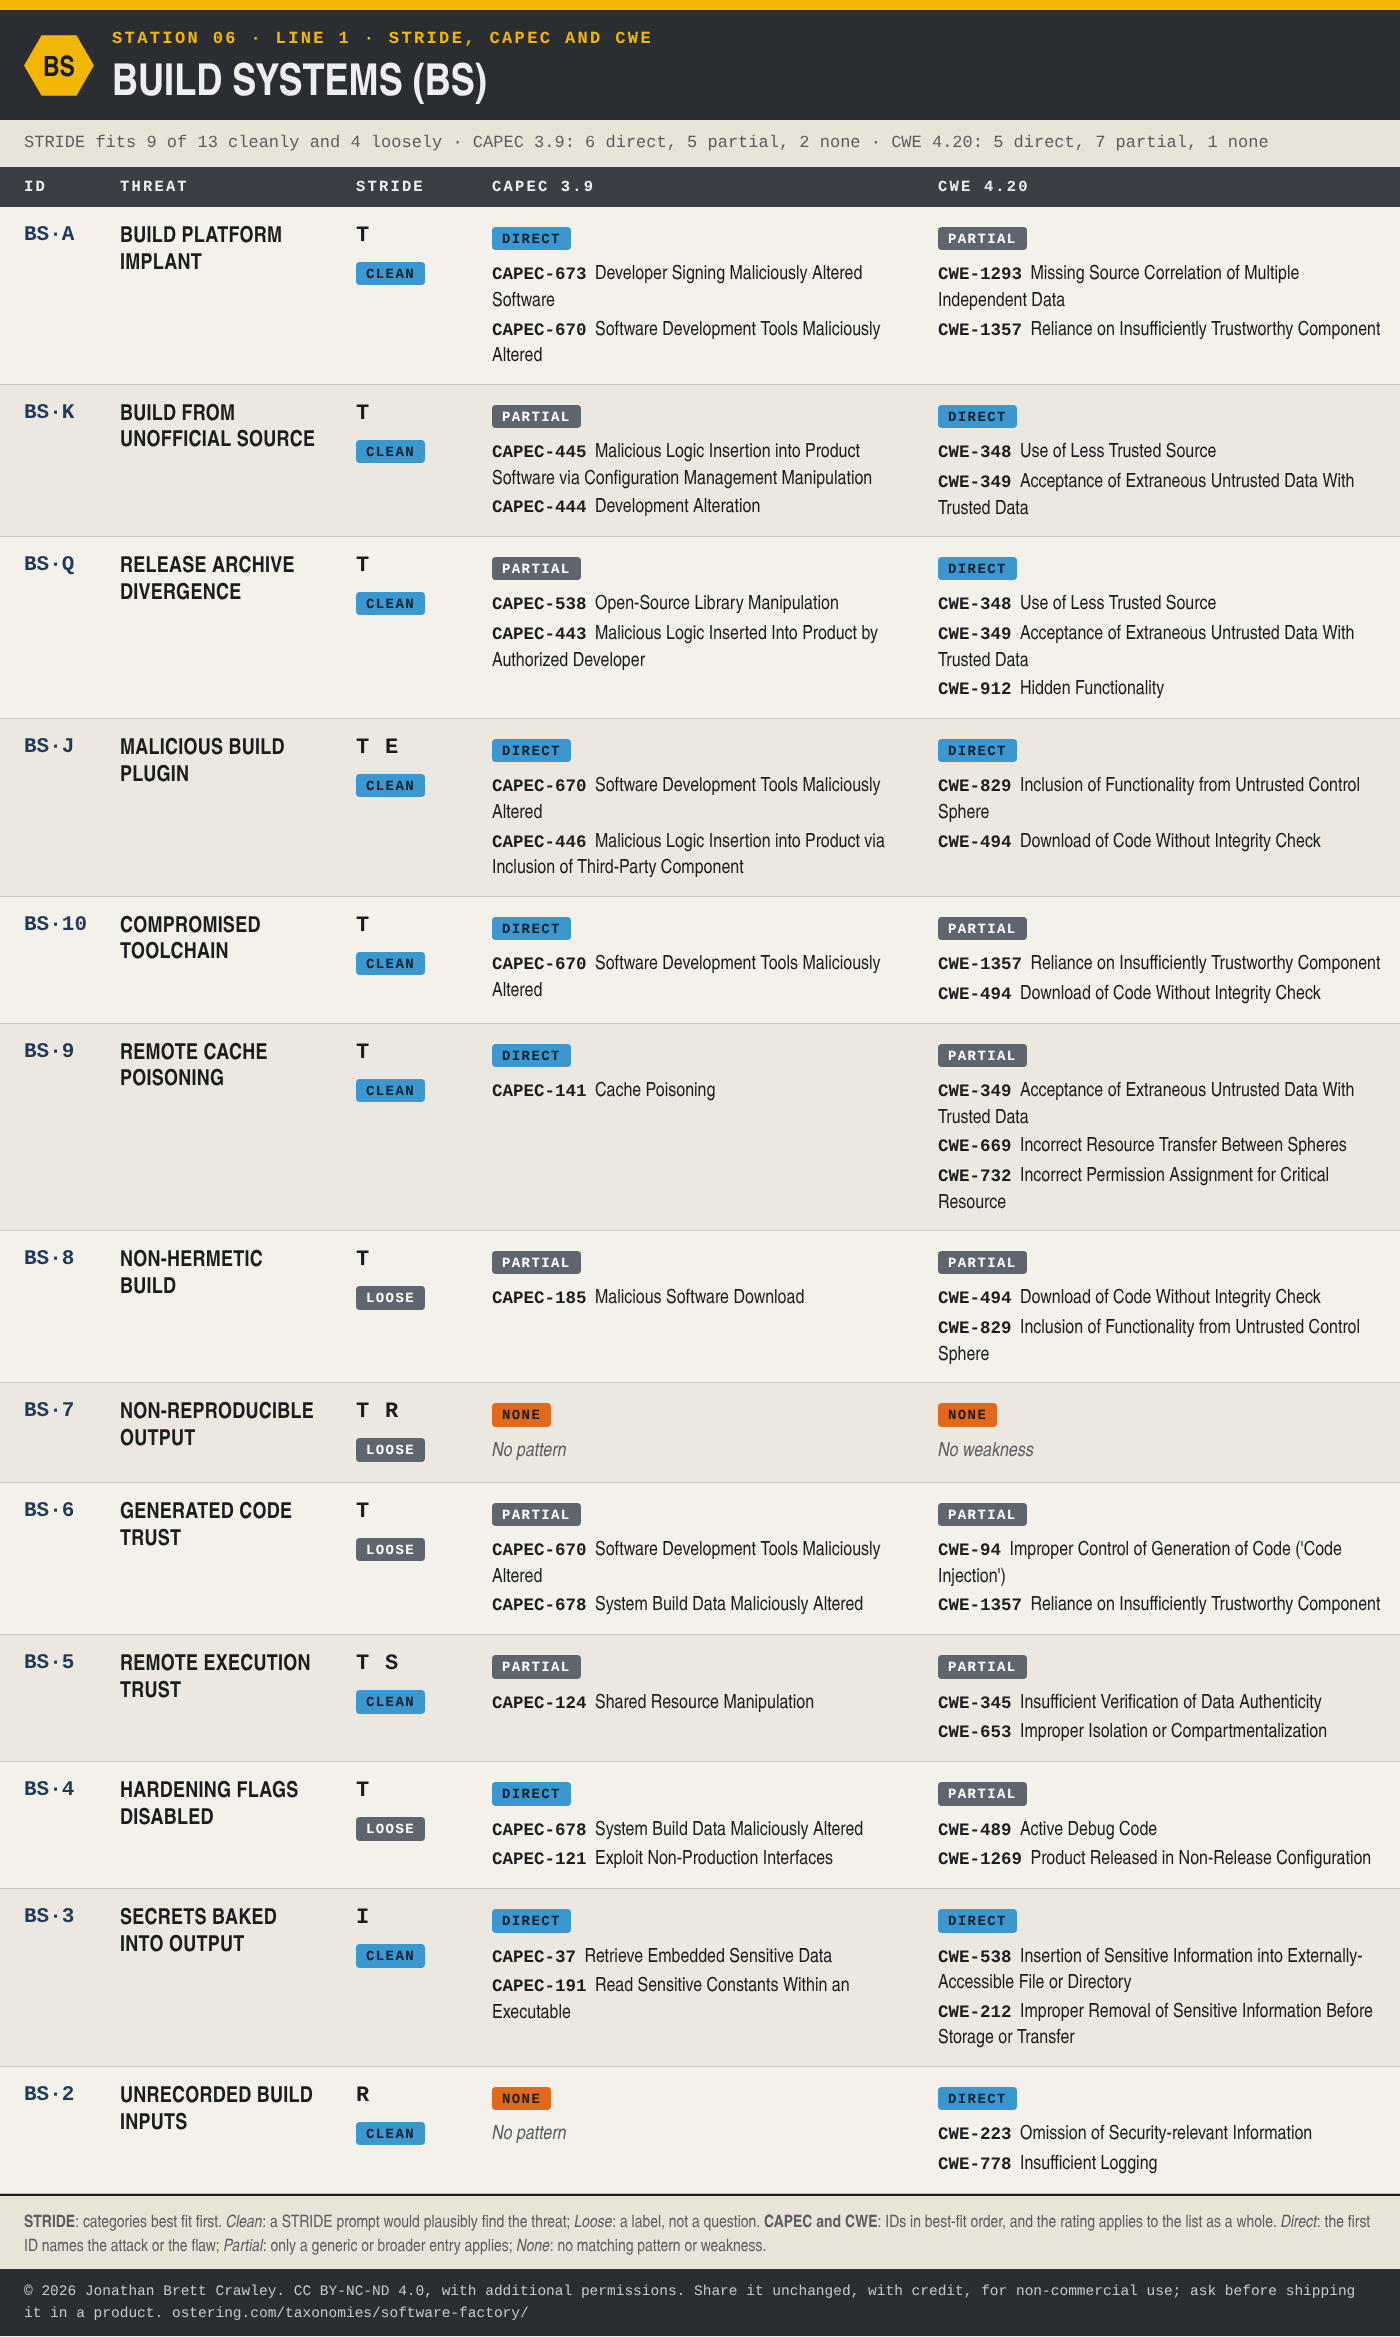
Of the 13 entries here, STRIDE fits 9 cleanly and 4 only loosely. CAPEC 3.9 has a pattern that describes 6 of them directly, only a generic parent pattern for 5, and nothing for 2. CWE 4.20 names the weakness directly for 5, has only a broader weakness for 7, and nothing for 1. The table below gives the mapping entry by entry, with the names of the CAPEC patterns and CWE weaknesses; what the mapping shows across the whole taxonomy is in Mapping the Software Factory Threat Taxonomy to STRIDE, CAPEC and CWE. The Excel, SKOS and STIX downloads carry the same mapping as text.
← Pipeline Identity and Secrets (ID) · Software factory overview · Dependency Resolution (DR) →
© 2026 Jonathan Brett Crawley. Licensed under CC BY-NC-ND 4.0 with additional permissions: see the licence on the software factory overview.