Version Control (VC)
Taxonomies › Software factory › Version Control
Station 02 of 17 · Line 1, Source to Artifact · 13 threats · prefix VC
The repository is the system of record for intent: every later control assumes that what is in it is what its owners meant. These cards cover repositories, branches, tags, review, identities and the hosting platform itself.
Scope: Repositories, branches, tags, review, forks, the hosting platform, its apps and bots.
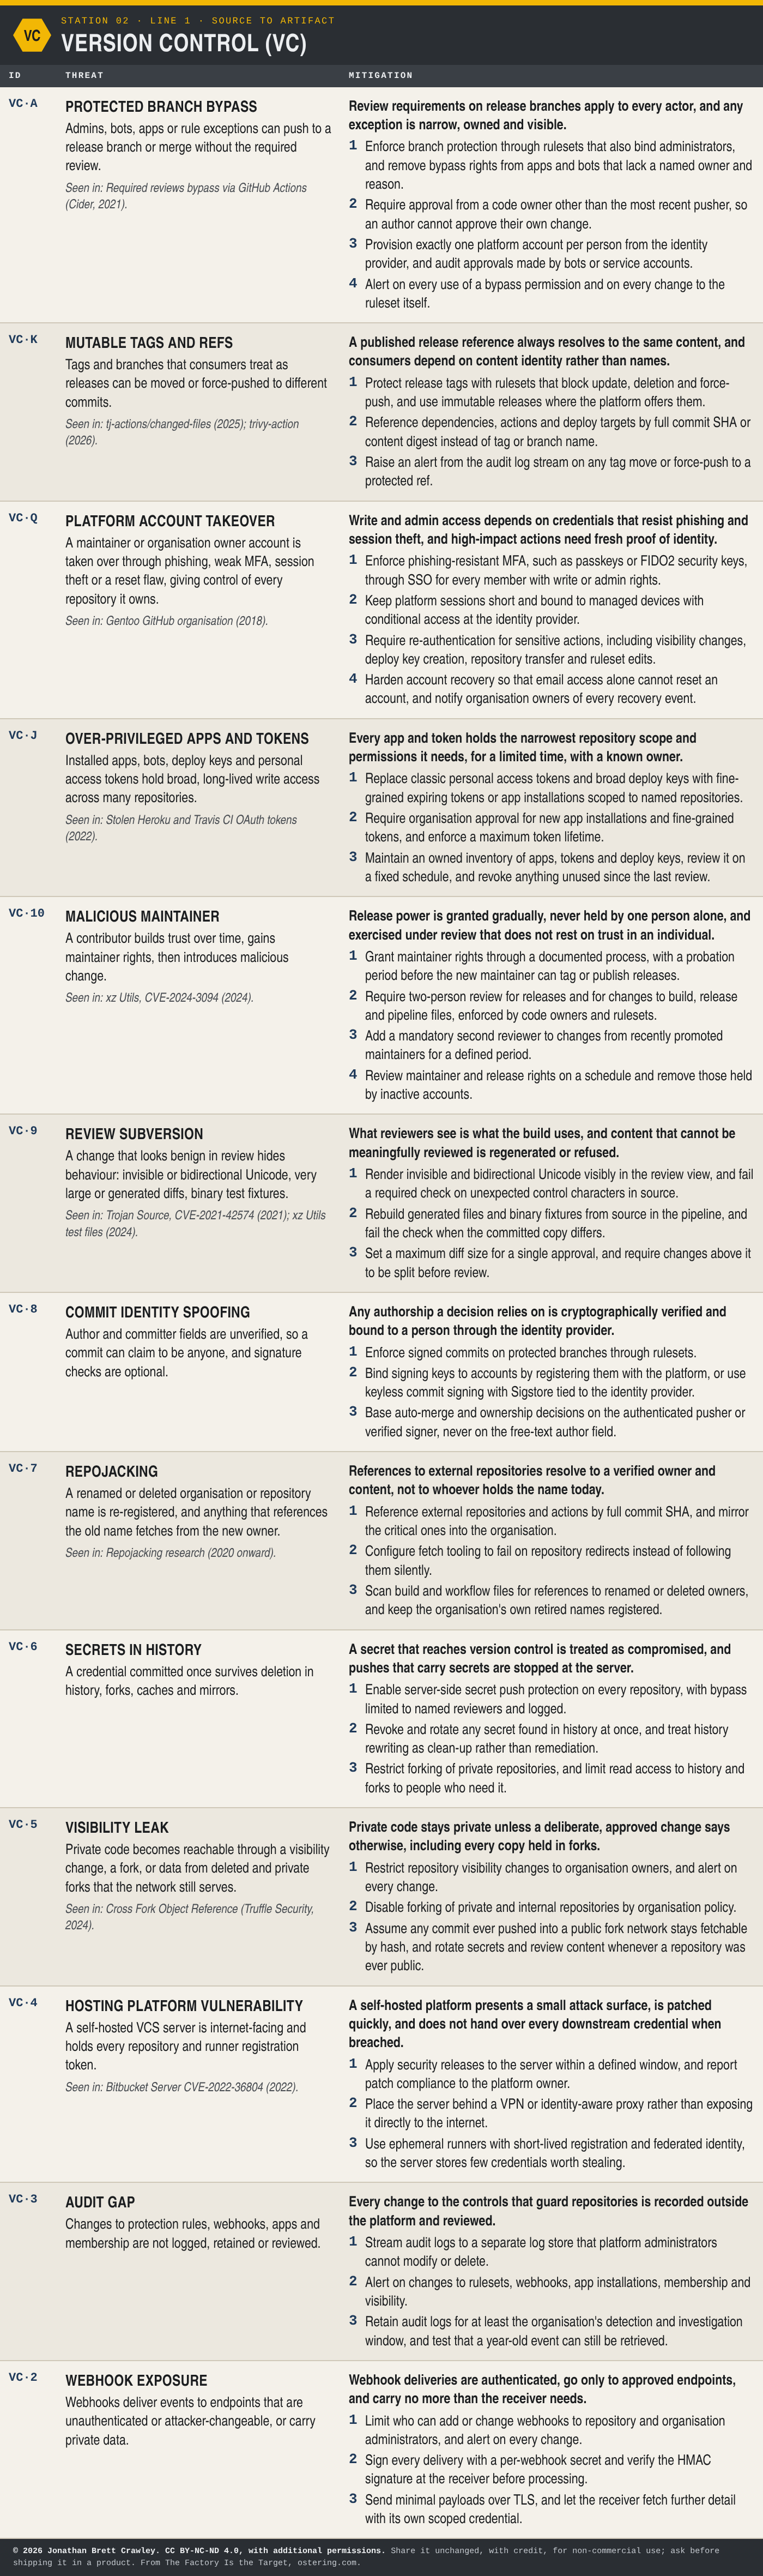
Text version: every entry on this page is in the PDF and Excel downloads on the overview page, where it can be searched and copied.
The threats
- VC·A Protected Branch Bypass
- VC·K Mutable Tags and Refs
- VC·Q Platform Account Takeover
- VC·J Over-Privileged Apps and Tokens
- VC·10 Malicious Maintainer
- VC·9 Review Subversion
- VC·8 Commit Identity Spoofing
- VC·7 Repojacking
- VC·6 Secrets in History
- VC·5 Visibility Leak
- VC·4 Hosting Platform Vulnerability
- VC·3 Audit Gap
- VC·2 Webhook Exposure
Seen in the wild
- VC·A Protected Branch Bypass: Required reviews bypass via GitHub Actions (Cider, 2021).
- VC·K Mutable Tags and Refs: tj-actions/changed-files (2025); trivy-action (2026).
- VC·Q Platform Account Takeover: Gentoo GitHub organisation (2018).
- VC·J Over-Privileged Apps and Tokens: Stolen Heroku and Travis CI OAuth tokens (2022).
- VC·10 Malicious Maintainer: xz Utils, CVE-2024-3094 (2024).
- VC·9 Review Subversion: Trojan Source, CVE-2021-42574 (2021); xz Utils test files (2024).
- VC·7 Repojacking: Repojacking research (2020 onward).
- VC·5 Visibility Leak: Cross Fork Object Reference (Truffle Security, 2024).
- VC·4 Hosting Platform Vulnerability: Bitbucket Server CVE-2022-36804 (2022).
Sources for each case are listed on the overview page.
STRIDE, CAPEC and CWE
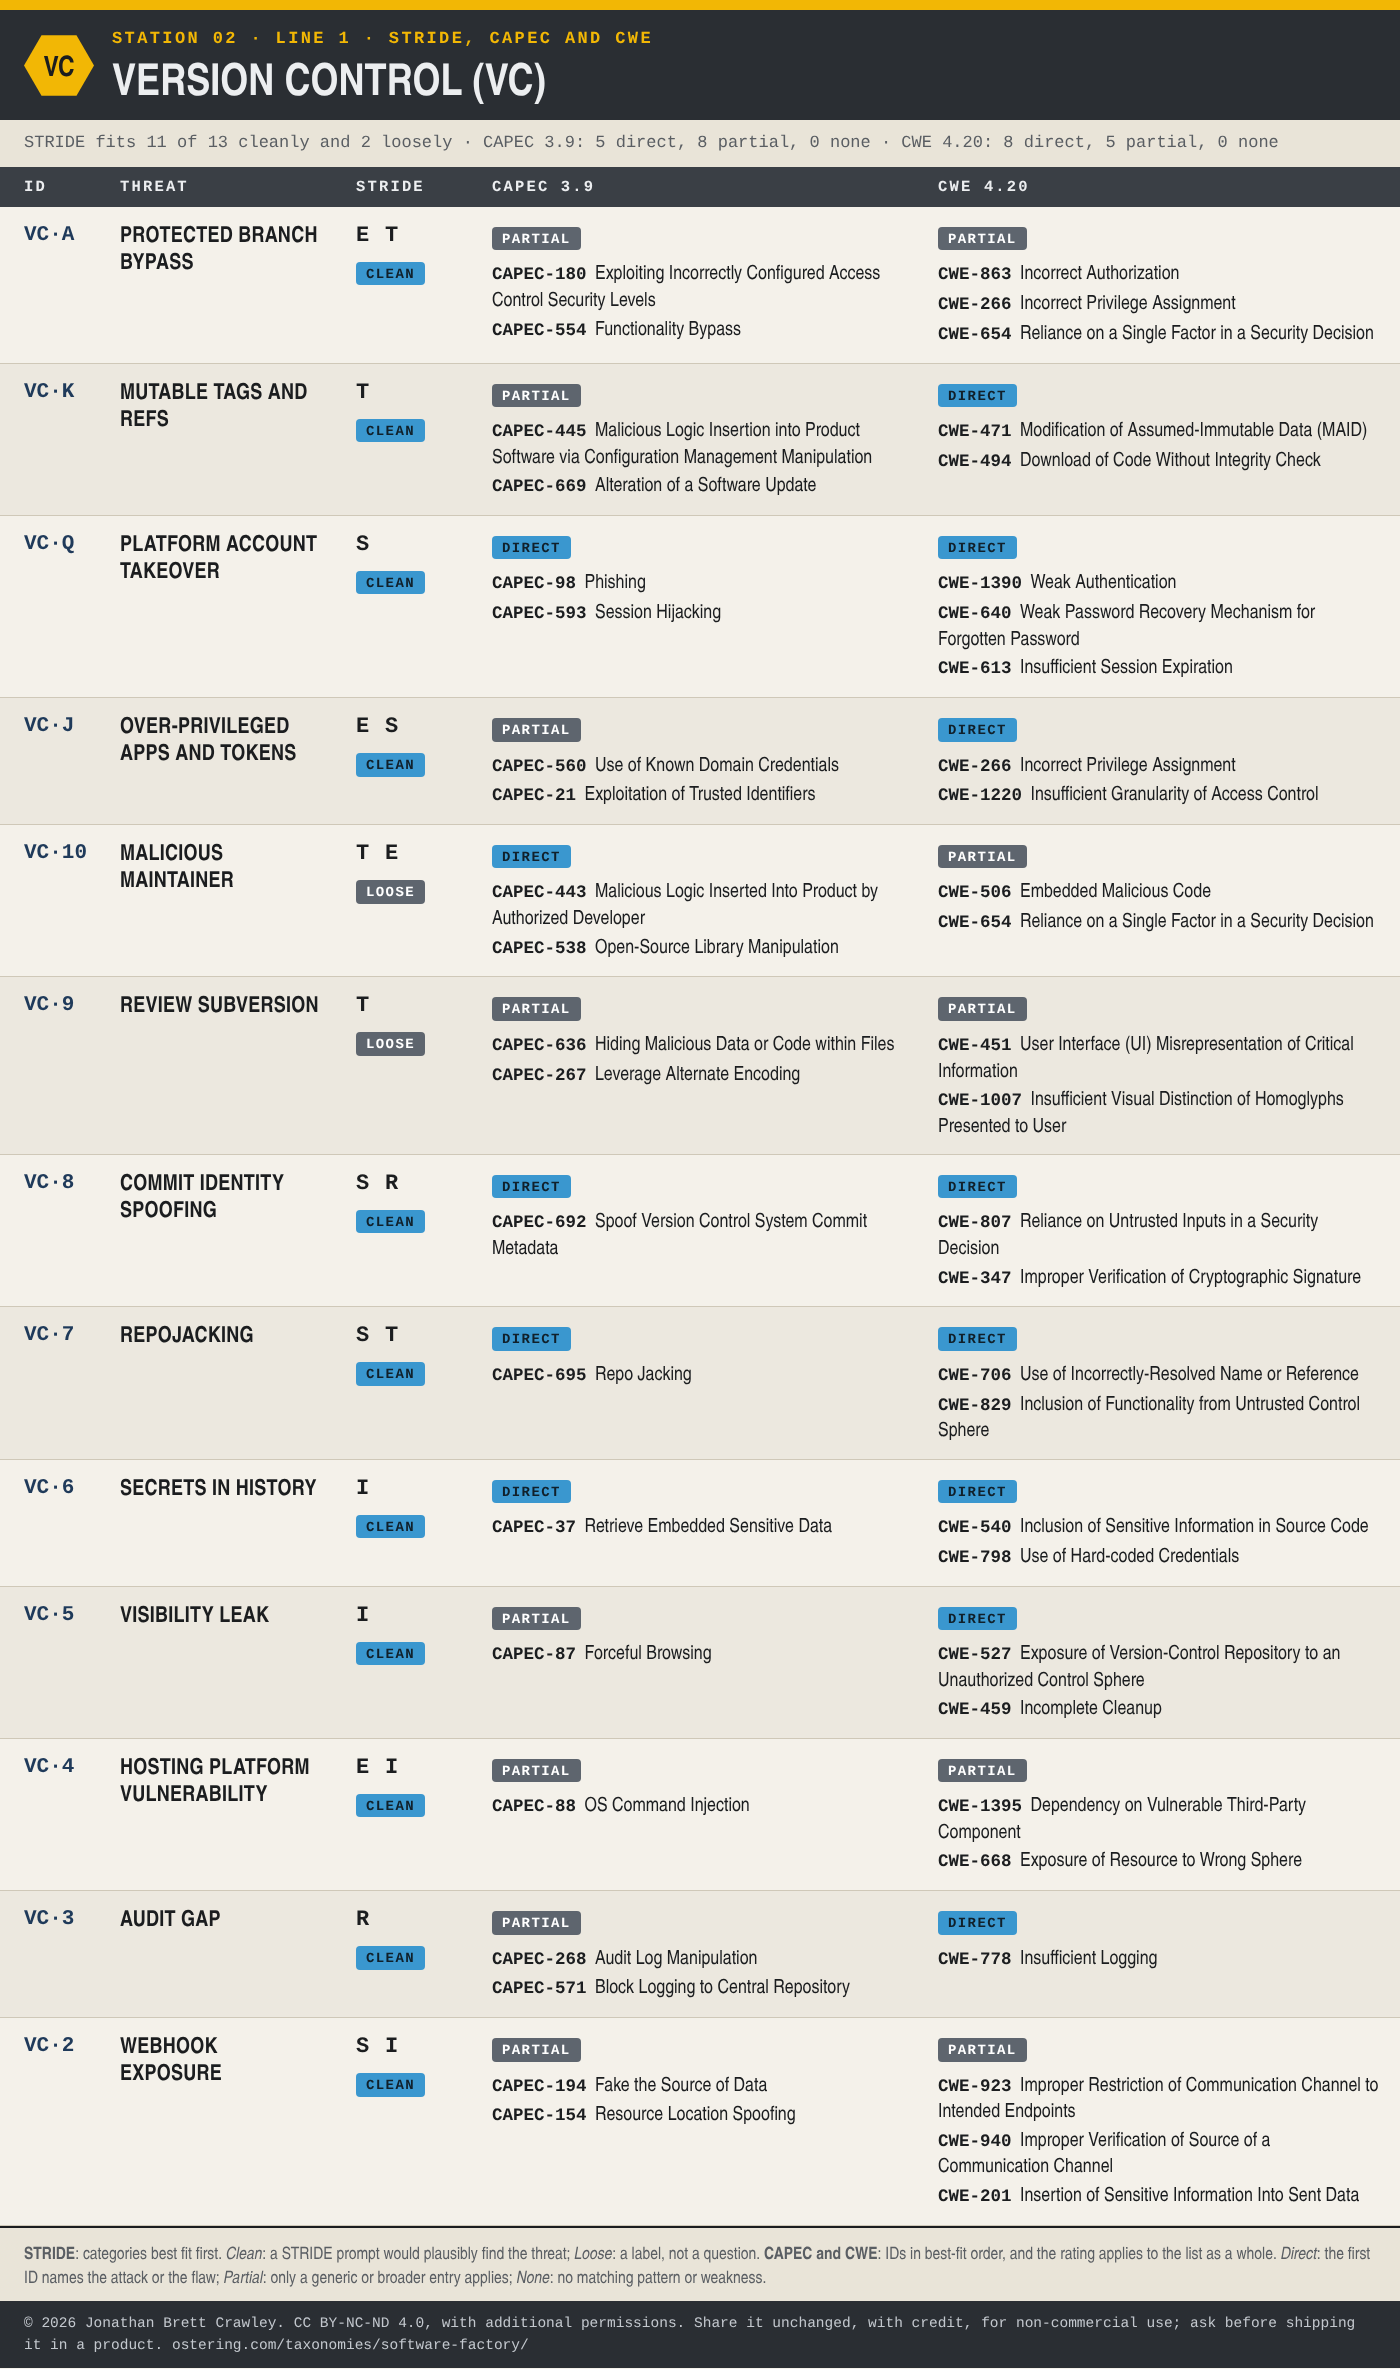
Of the 13 entries here, STRIDE fits 11 cleanly and 2 only loosely. CAPEC 3.9 has a pattern that describes 5 of them directly, and only a generic parent pattern for 8. CWE 4.20 names the weakness directly for 8, has only a broader weakness for 5,. The table below gives the mapping entry by entry, with the names of the CAPEC patterns and CWE weaknesses; what the mapping shows across the whole taxonomy is in Mapping the Software Factory Threat Taxonomy to STRIDE, CAPEC and CWE. The Excel, SKOS and STIX downloads carry the same mapping as text.
← Workstation and Agents (WS) · Software factory overview · Pipeline Definition (PD) →
© 2026 Jonathan Brett Crawley. Licensed under CC BY-NC-ND 4.0 with additional permissions: see the licence on the software factory overview.