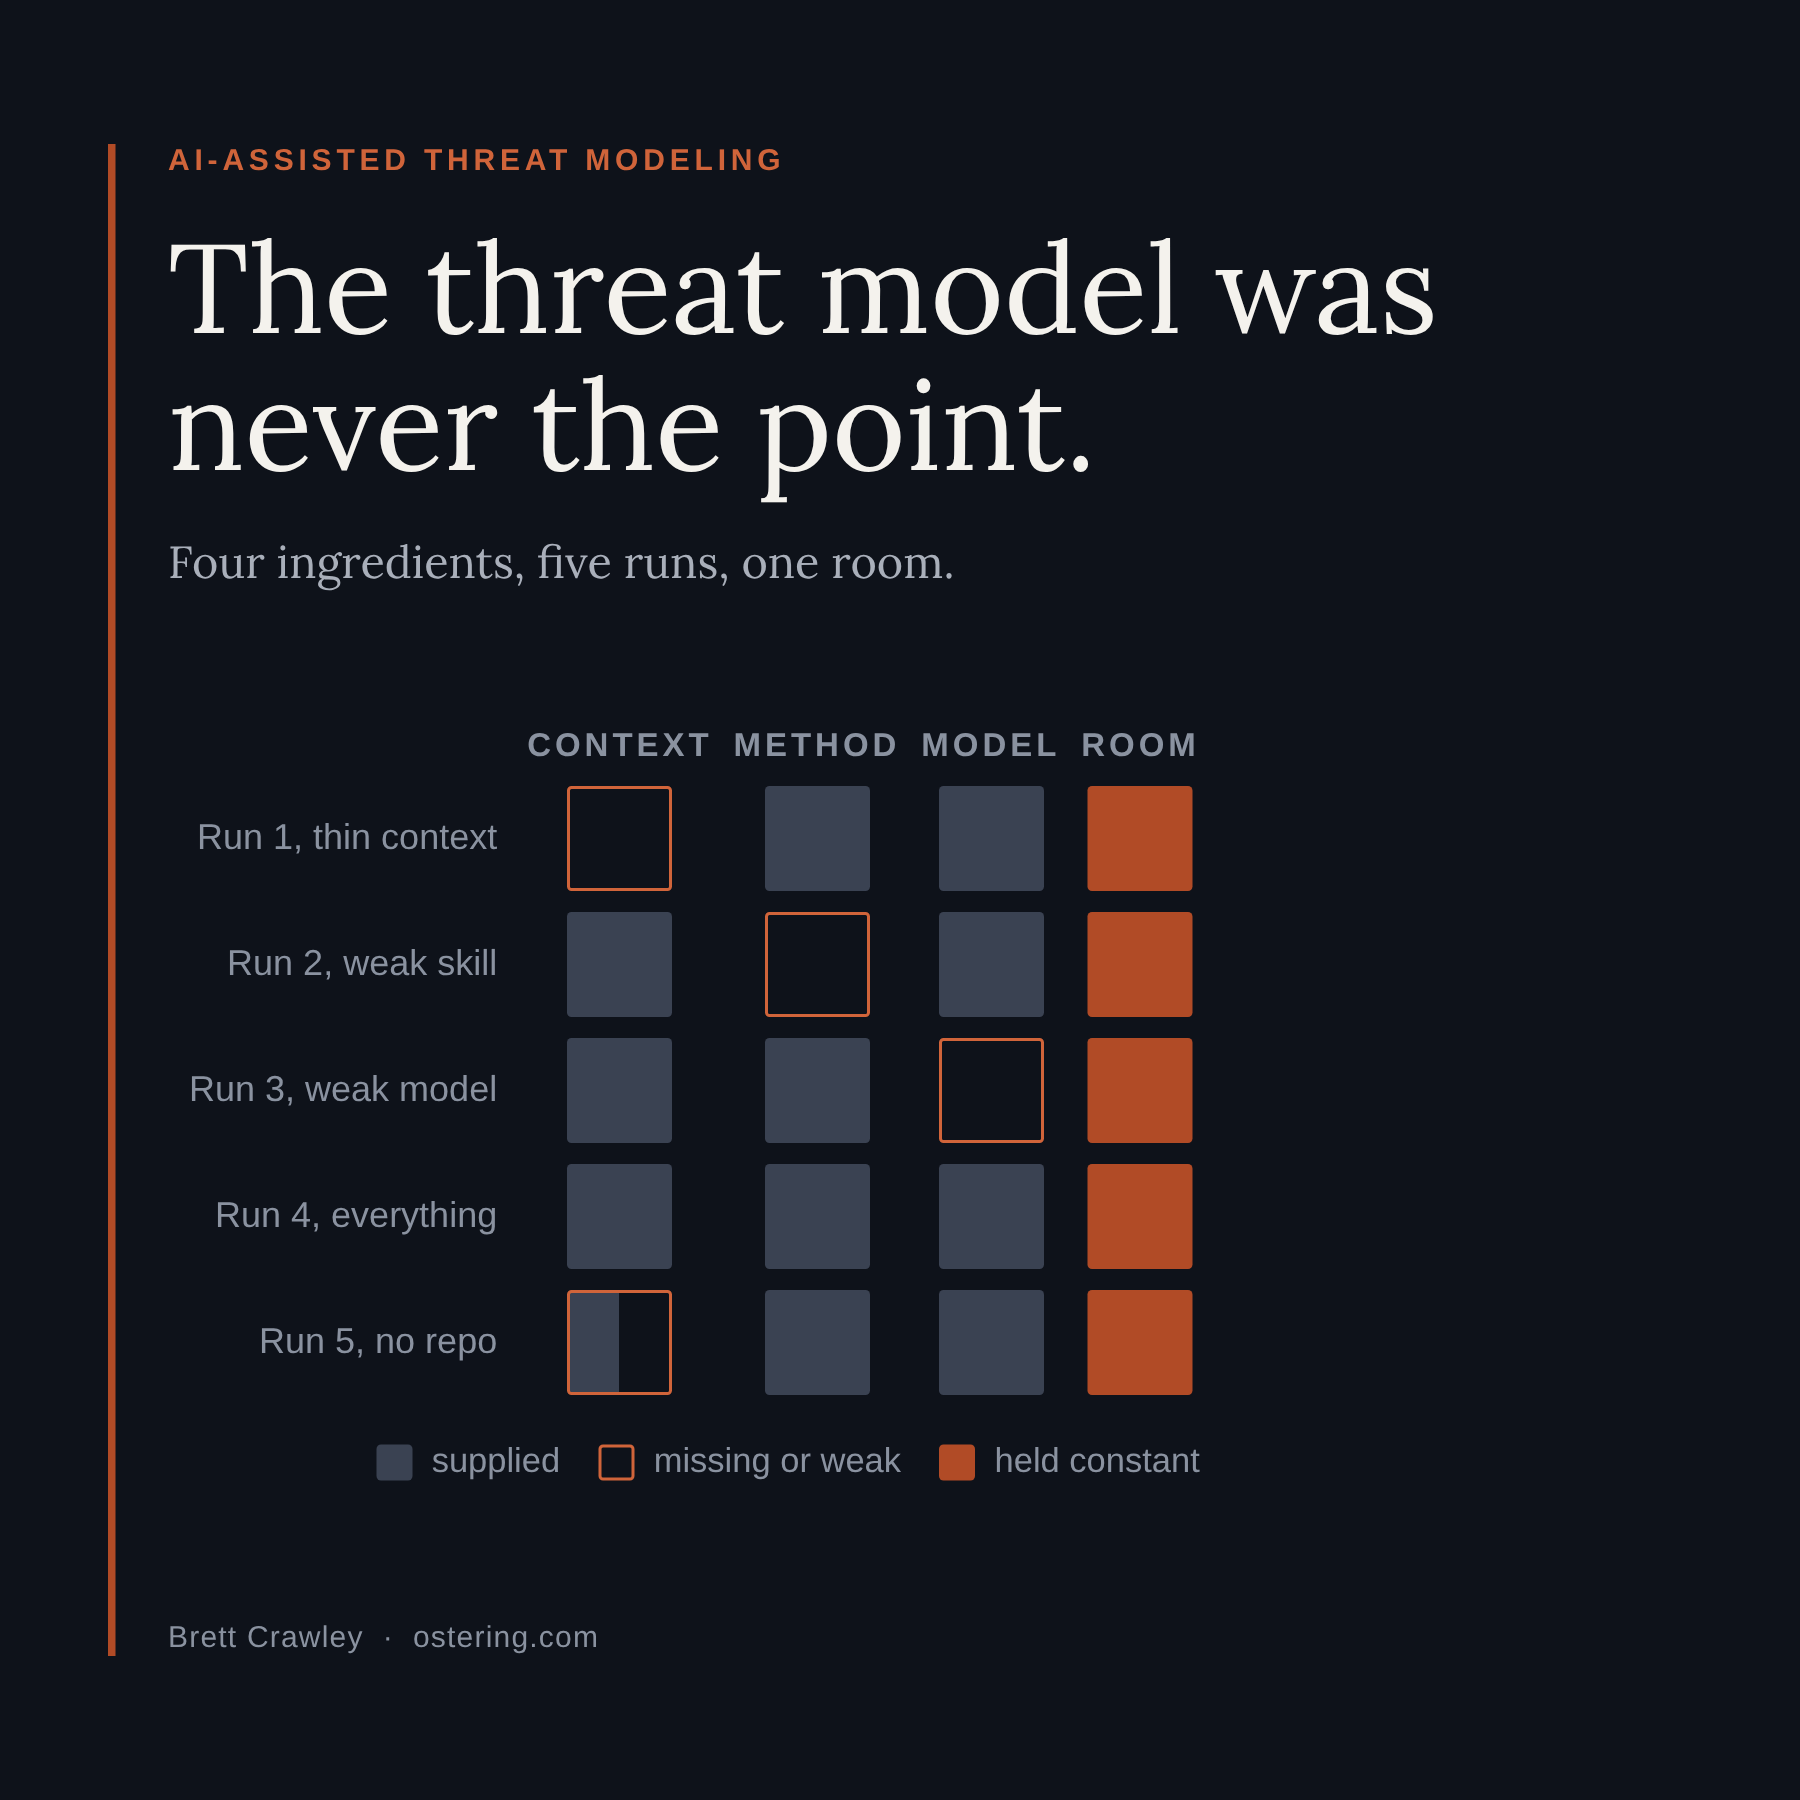
Tagged in: AI Security (11)
The Wine Has Turned to Vinegar
Why $249 Billion Can’t Fix Software Security TL;DR:...
src2sink
Back in February, in my deep dive comparing...
Threat Modeling MCP
Threat Modeling the Model Context Protocol: Your Agent...
Get PQC Ready PDQ - Part 2
The Plan, the Order, and the Bill In...
Threat Modeling AI Systems: A Complete Playbook for Practitioners
The Blast Radius - Edition [4] Over the...
Sparse or Dense? Claude Mythos, Dan Geer, and Where We Should Actually Be Spending Our Effort
Last week, Anthropic announced Claude Mythos Preview and...
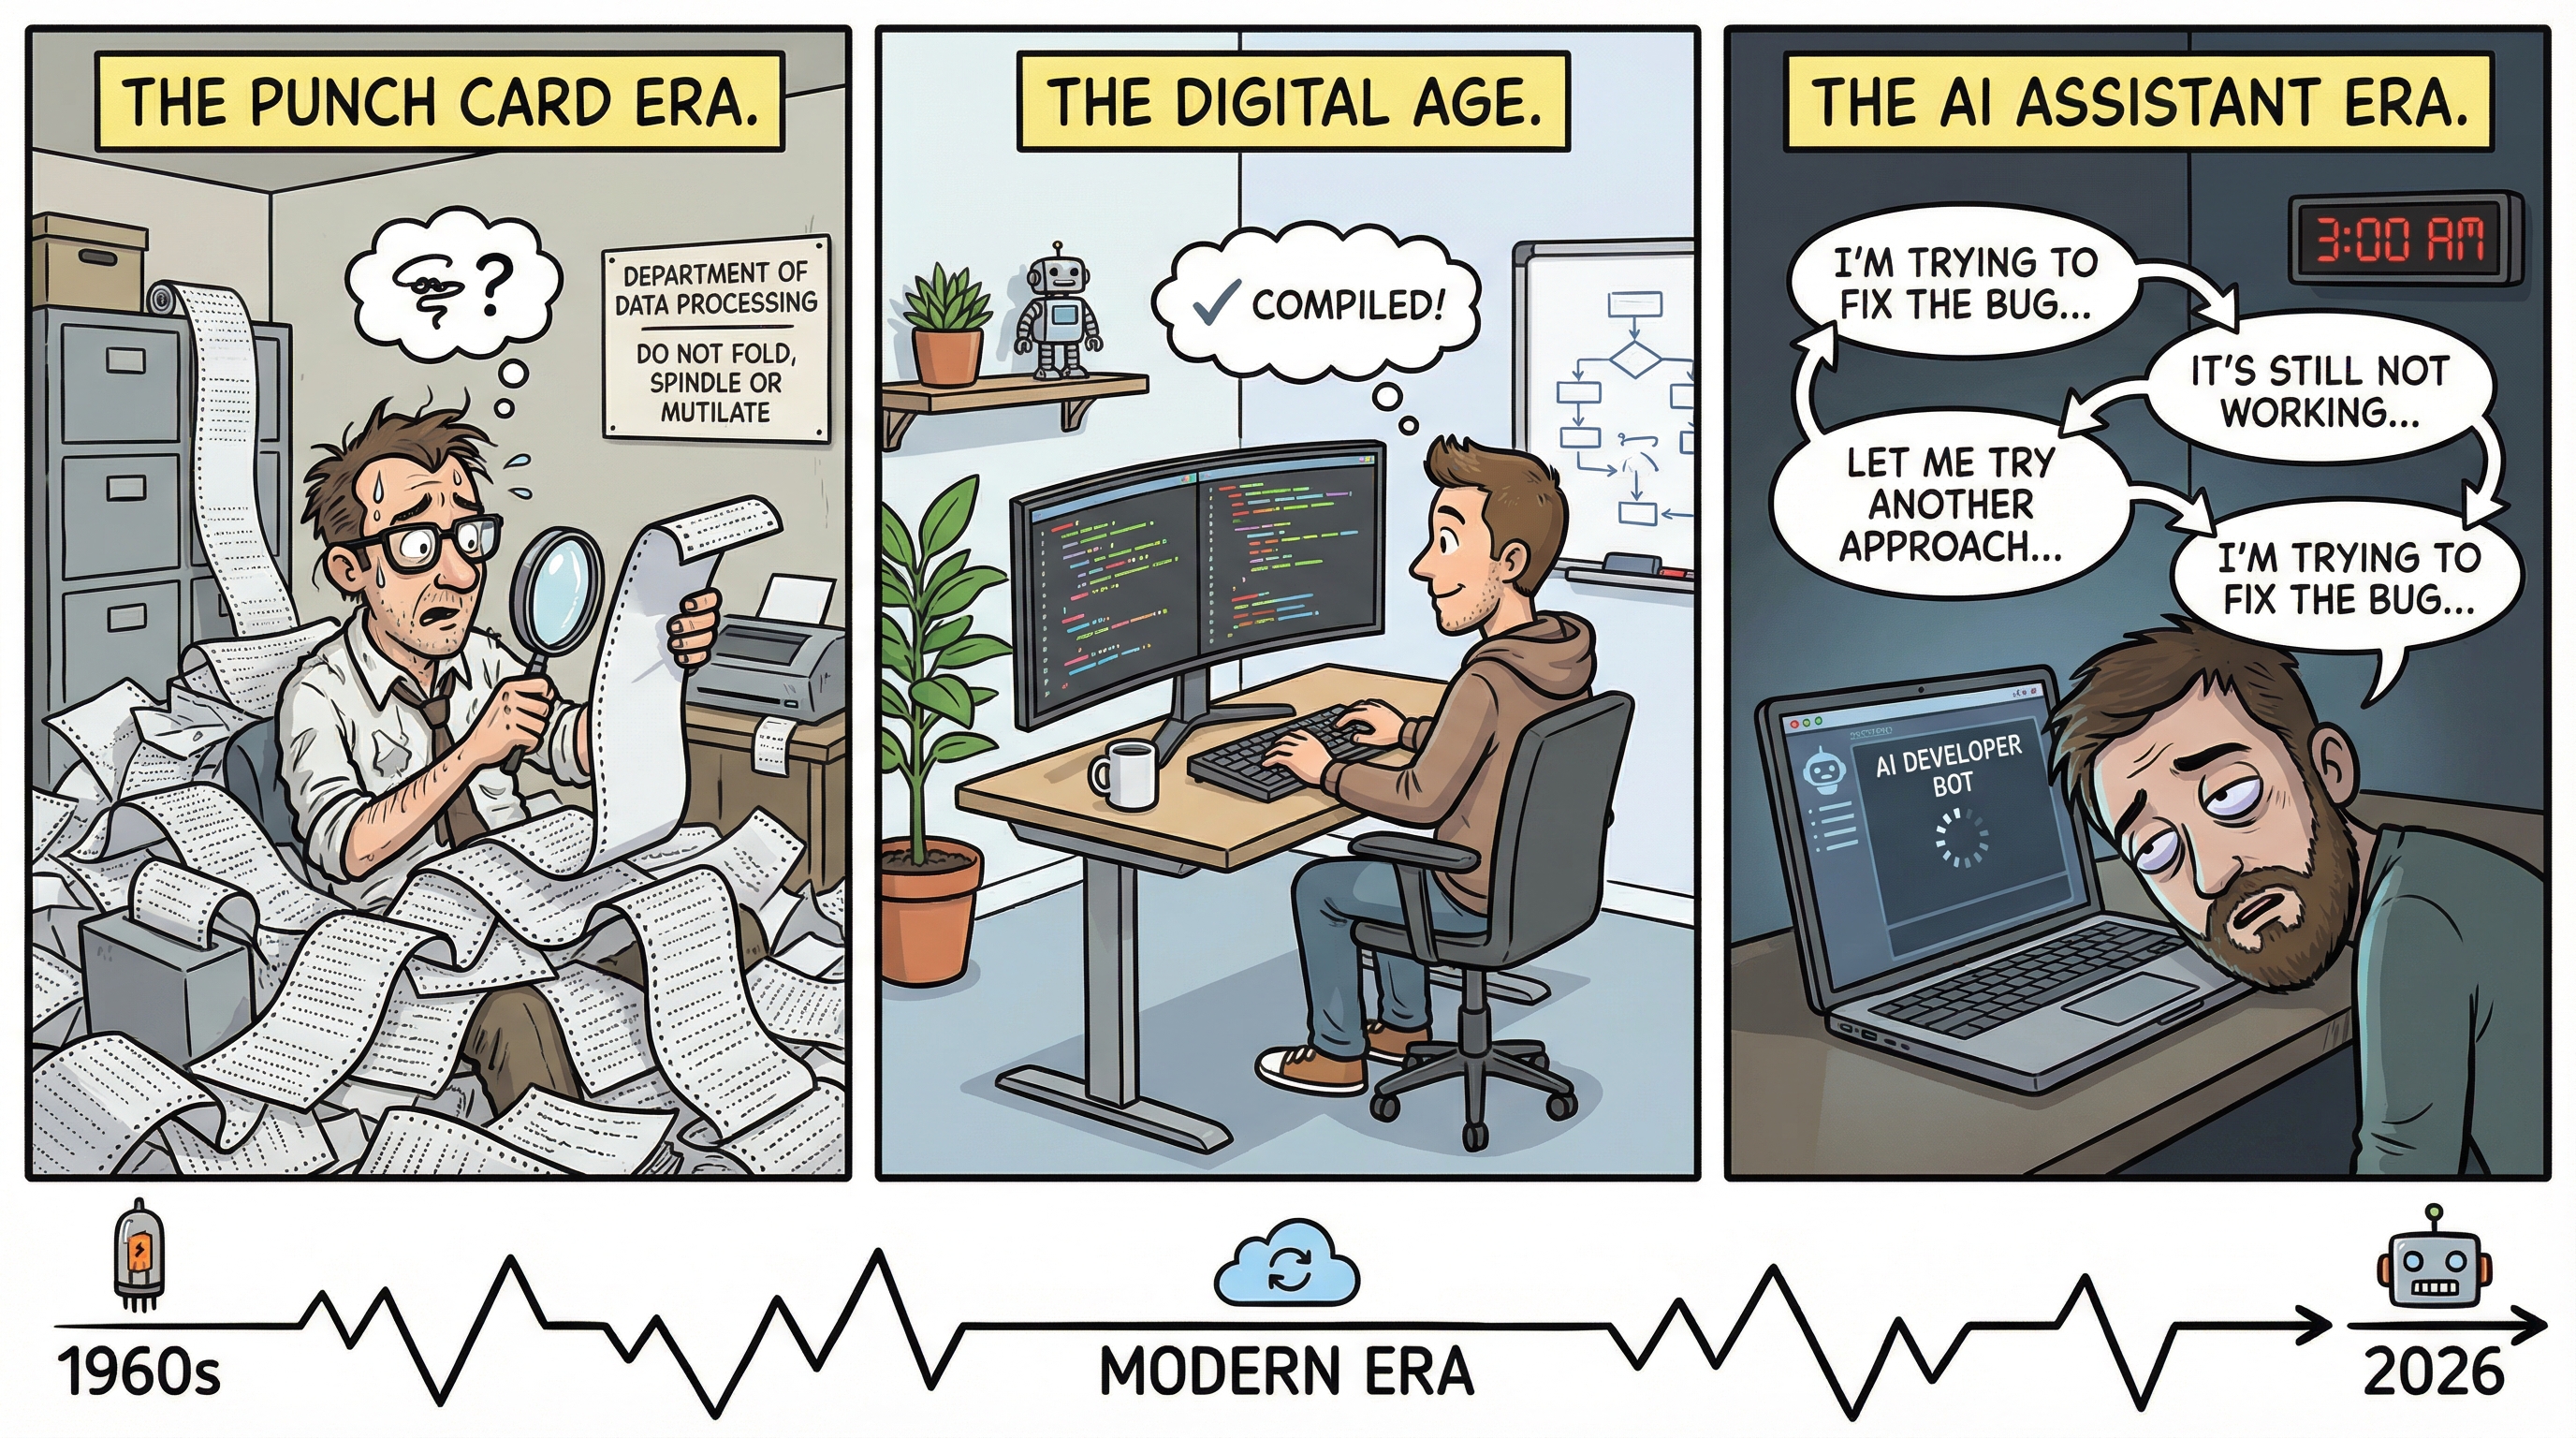
Software Engineering Has Regressed 50+ Years Since AI
Bear with me on this train of thought....
SAST vs Claude Code Security: A Deep Dive
SAST vs Claude Code Security: A Deep Dive...
Cursor as your Secure Dev Team
Cursor as your Secure Dev Team What I...
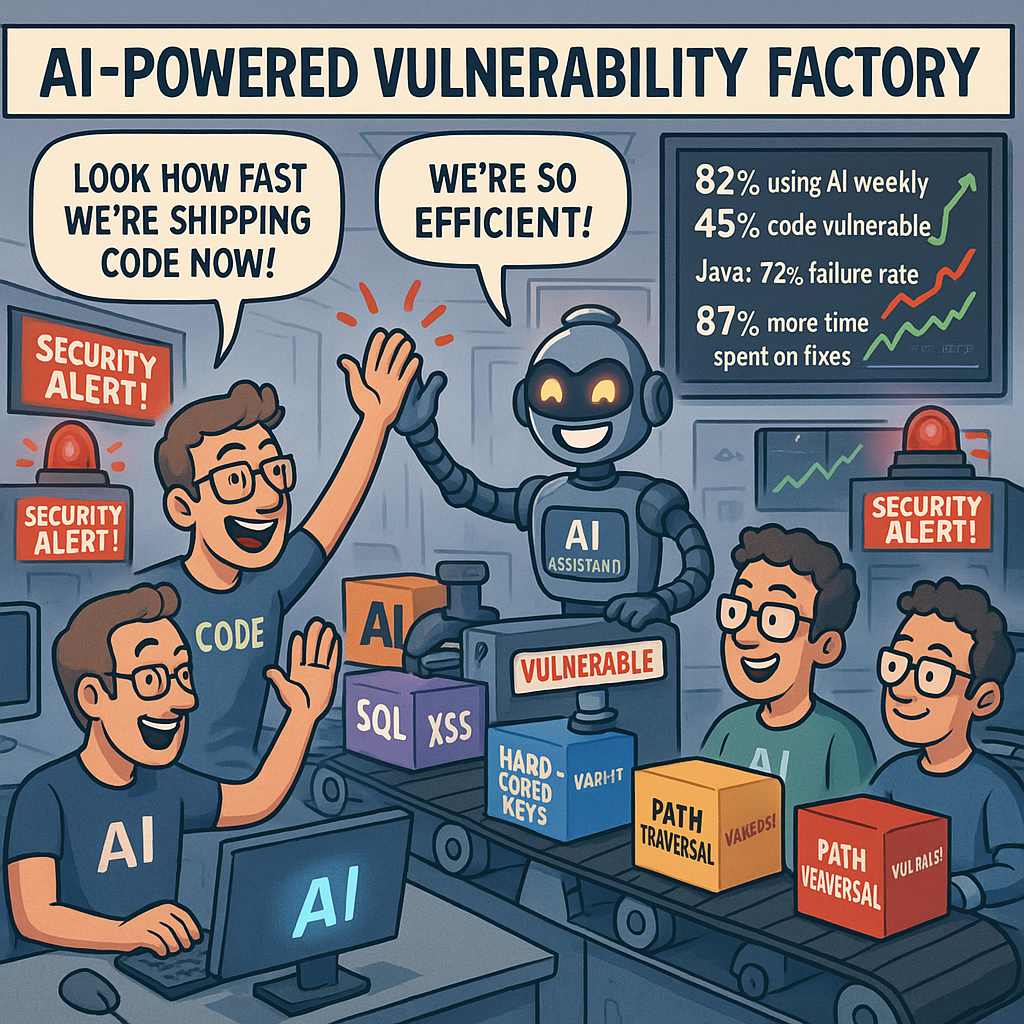
Is Your AI Philosophy Broken?
AI-Generated Code: Productivity Gains, Security Pains, and the...
Browse all Topics
- Agentic AI
- AI Security
- Application Security
- Auth
- AWS
- CAPEC
- Catasto
- Change
- Claude Code Security
- Cloud Security
- Compliance
- CRA
- Cryptography
- Culture
- Cursor AI
- Cybersecurity
- Dark Patterns
- DevSecOps
- DIY
- DORA
- Elevation of Privilege
- Games
- Garden Wildlife
- Graph Analysis
- Hedgehog
- Inner-Source
- Java
- JavaScript
- KMS
- languages
- learning
- Miro
- Mitre
- Model Context Protocol
- NIS2
- Open-Source
- Origins
- Osteria
- OWASP
- Post Quantum Cryptography
- Privacy
- Privacy by Design
- Python
- Risk
- Running
- SAST
- SBOM
- scarno
- Secure by Design
- Security
- Security by Design
- Security Culture
- Security Maturity
- SLSA
- Social Engineering
- Software Architecture
- Software Design
- Software Development
- Software Engineering
- Software Quality
- src2sink
- Strategy
- STRIDE
- Supply Chain Security
- Technical Dept
- Threat Modeling
- TRIM
- Woodworking