Workstation and Agents (WS)
Taxonomies › Software factory › Workstation and Agents
Station 01 of 17 · Line 1, Source to Artifact · 13 threats · prefix WS
The developer’s machine holds credentials to everything downstream and runs more unvetted code than any server. These cards cover IDEs, extensions, dev containers, local tooling, and the AI assistants and agents that now act with a developer’s authority.
Scope: IDEs, extensions, dev containers, local credentials, AI coding assistants and agents, pre-commit hooks.
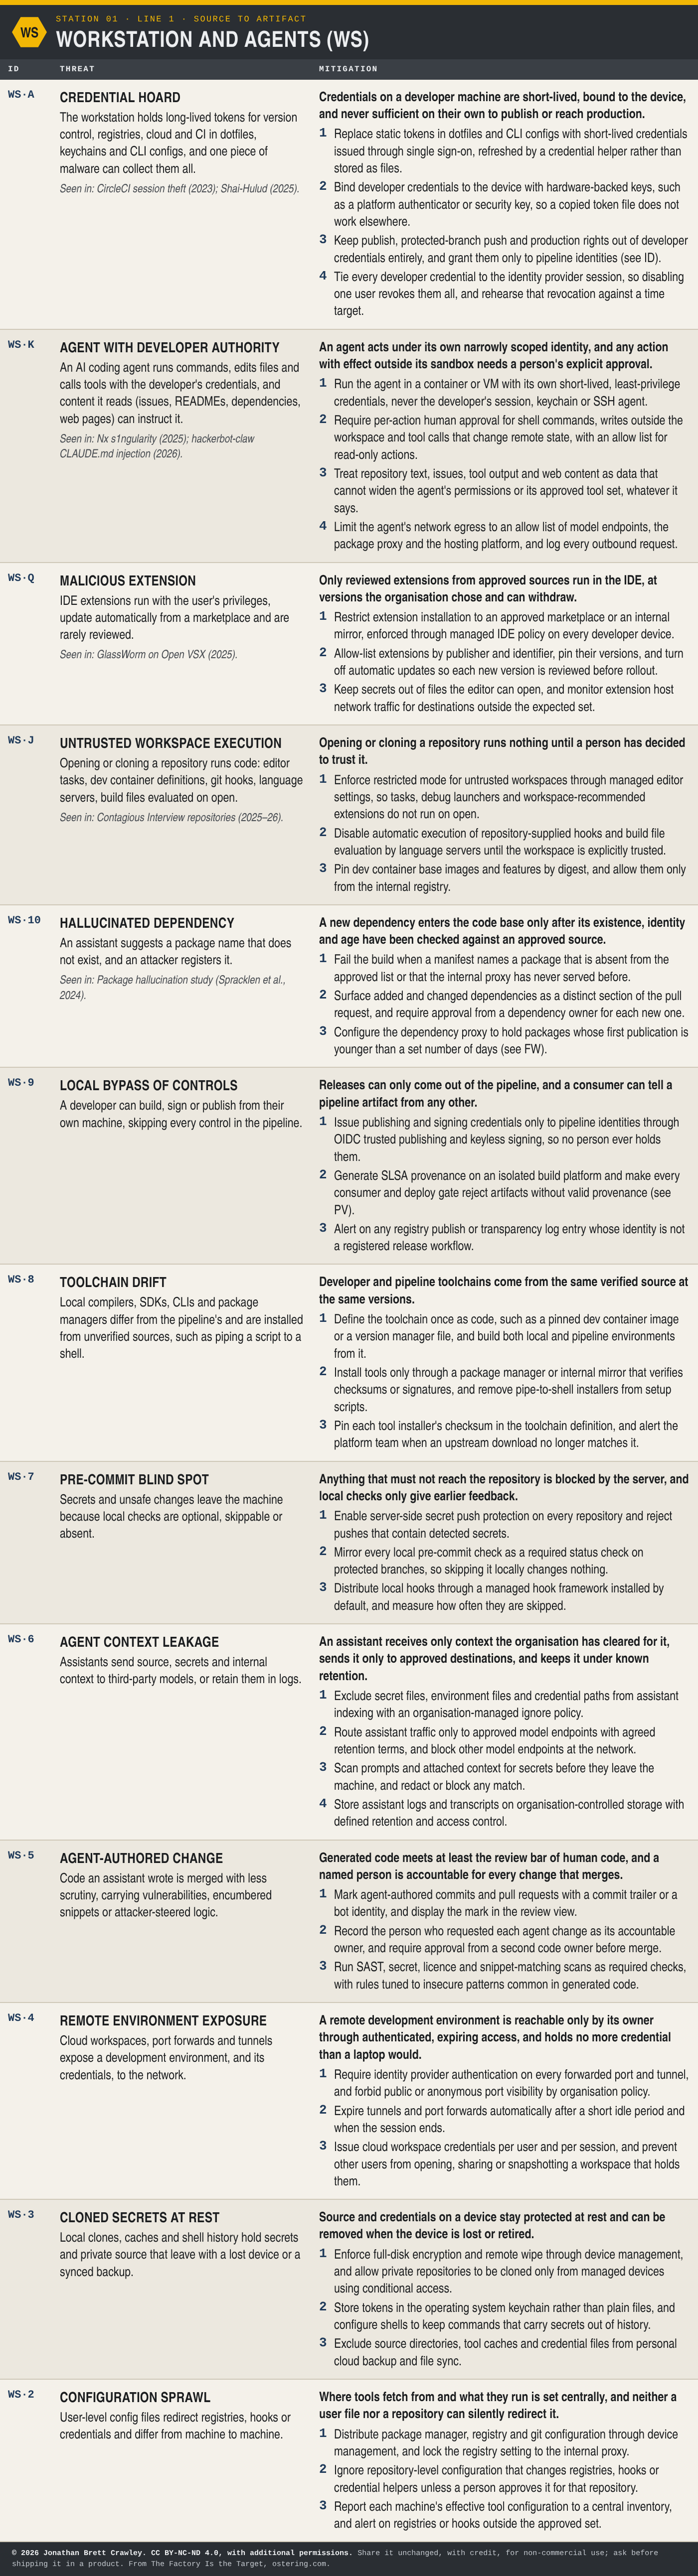
Text version: every entry on this page is in the PDF and Excel downloads on the overview page, where it can be searched and copied.
The threats
- WS·A Credential Hoard
- WS·K Agent with Developer Authority
- WS·Q Malicious Extension
- WS·J Untrusted Workspace Execution
- WS·10 Hallucinated Dependency
- WS·9 Local Bypass of Controls
- WS·8 Toolchain Drift
- WS·7 Pre-Commit Blind Spot
- WS·6 Agent Context Leakage
- WS·5 Agent-Authored Change
- WS·4 Remote Environment Exposure
- WS·3 Cloned Secrets at Rest
- WS·2 Configuration Sprawl
Seen in the wild
- WS·A Credential Hoard: CircleCI session theft (2023); Shai-Hulud (2025).
- WS·K Agent with Developer Authority: Nx s1ngularity (2025); hackerbot-claw CLAUDE.md injection (2026).
- WS·Q Malicious Extension: GlassWorm on Open VSX (2025).
- WS·J Untrusted Workspace Execution: Contagious Interview repositories (2025–26).
- WS·10 Hallucinated Dependency: Package hallucination study (Spracklen et al., 2024).
Sources for each case are listed on the overview page.
STRIDE, CAPEC and CWE
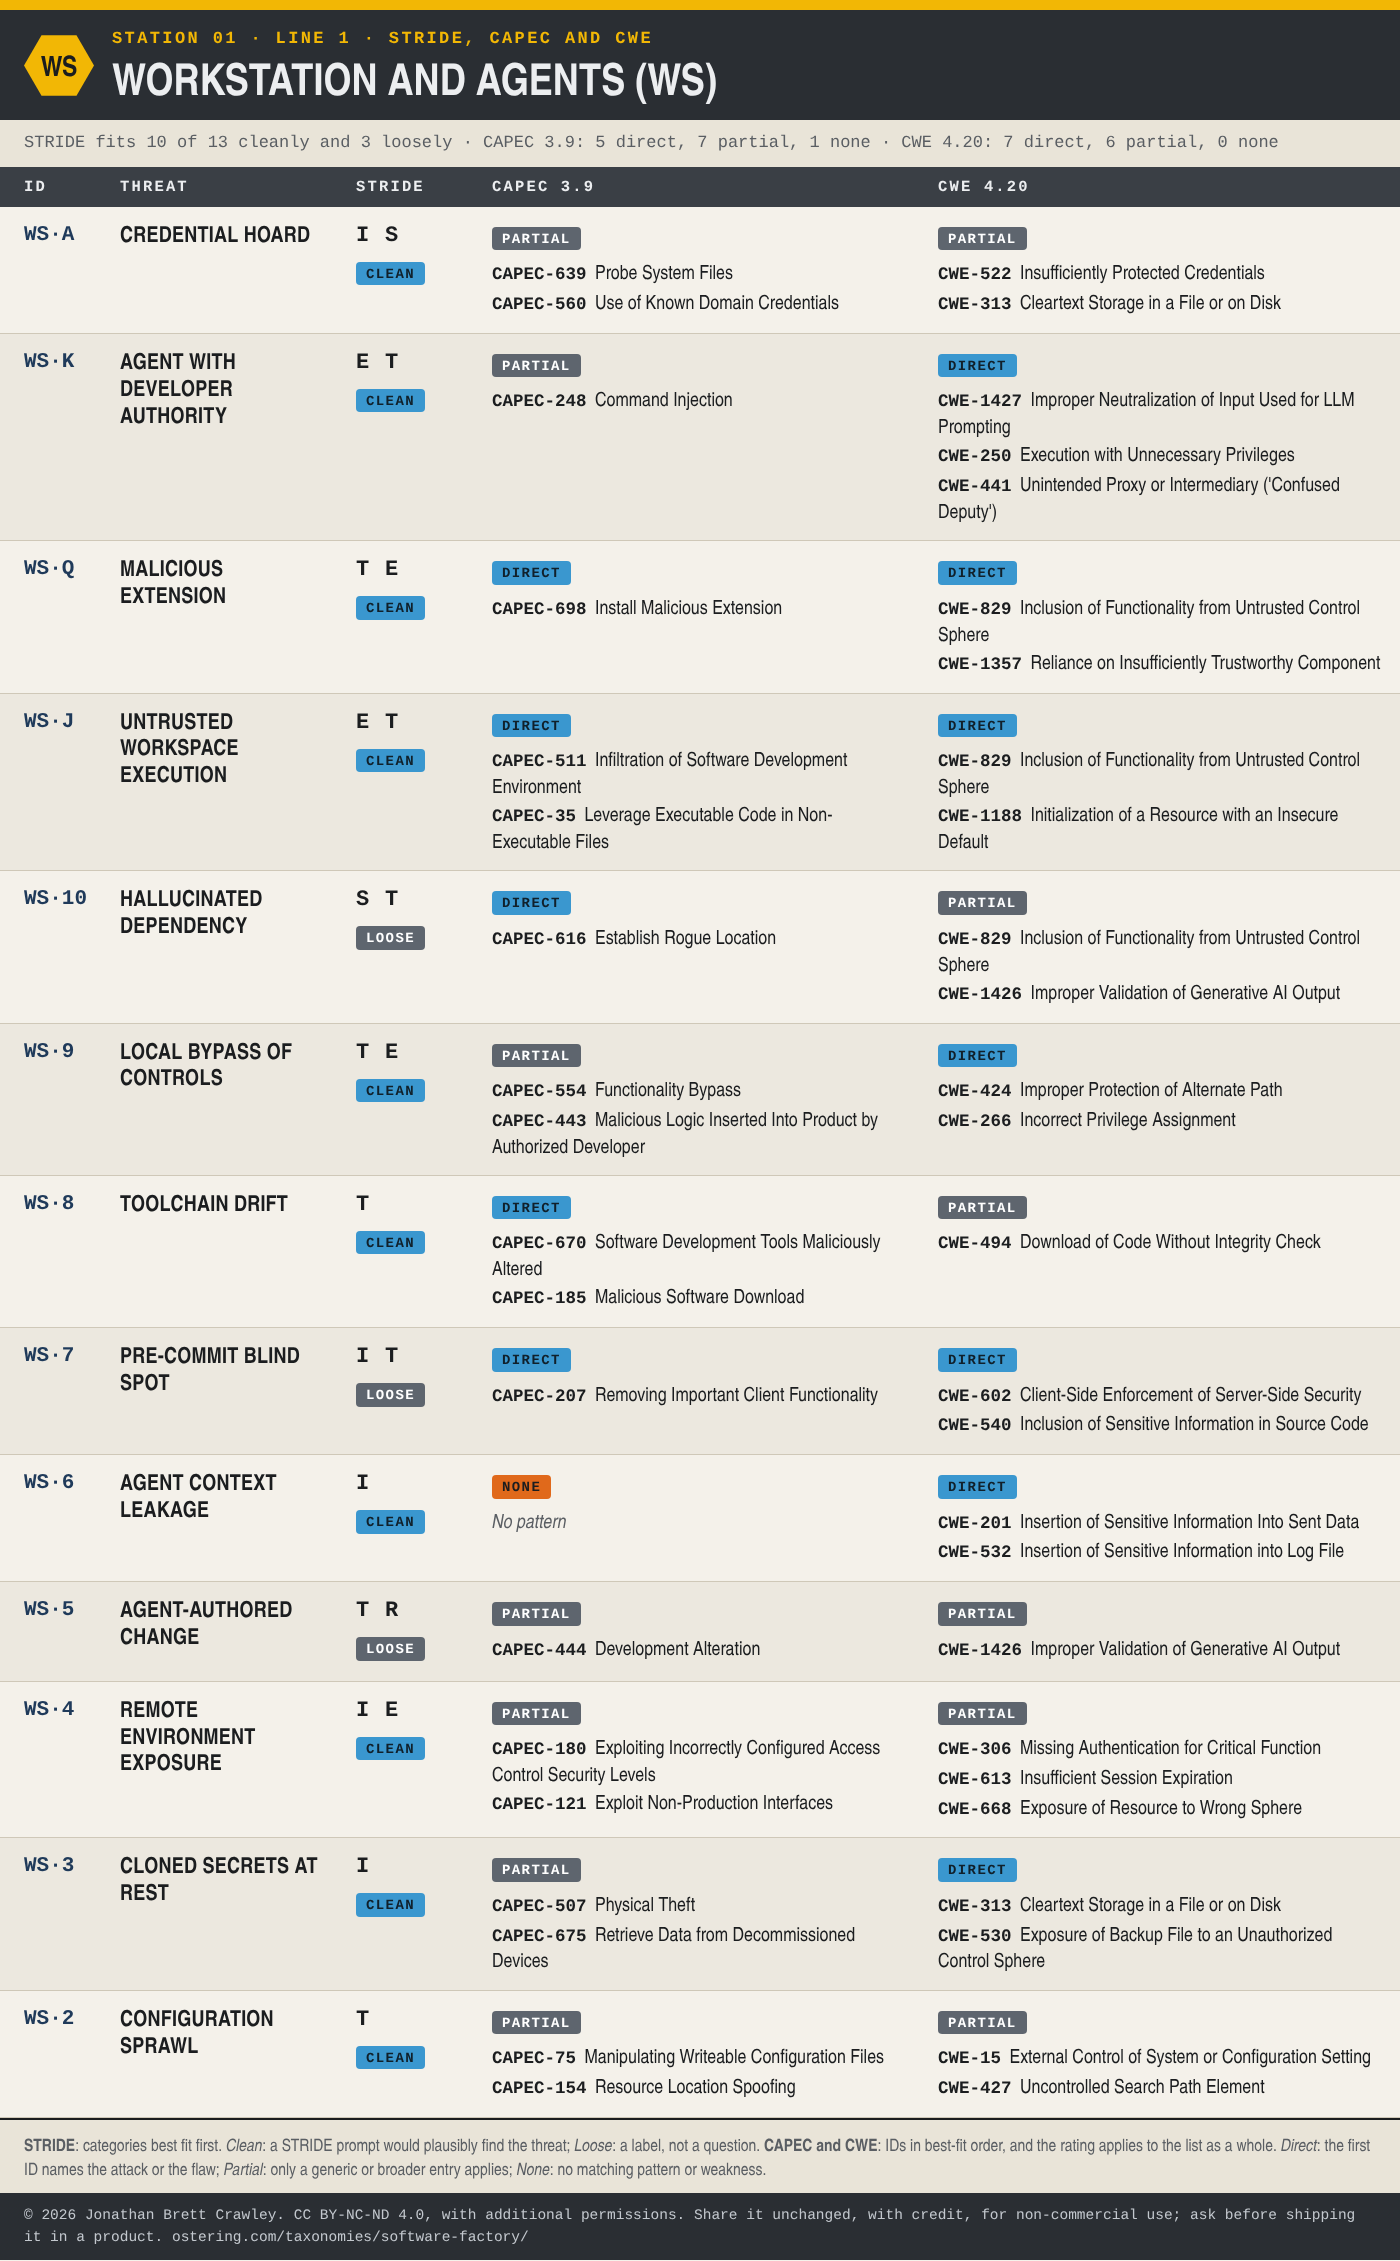
Of the 13 entries here, STRIDE fits 10 cleanly and 3 only loosely. CAPEC 3.9 has a pattern that describes 5 of them directly, only a generic parent pattern for 7, and nothing for 1. CWE 4.20 names the weakness directly for 7, has only a broader weakness for 6,. The table below gives the mapping entry by entry, with the names of the CAPEC patterns and CWE weaknesses; what the mapping shows across the whole taxonomy is in Mapping the Software Factory Threat Taxonomy to STRIDE, CAPEC and CWE. The Excel, SKOS and STIX downloads carry the same mapping as text.
Software factory overview · Version Control (VC) →
© 2026 Jonathan Brett Crawley. Licensed under CC BY-NC-ND 4.0 with additional permissions: see the licence on the software factory overview.