Threat Modeling AI Systems: A Complete Playbook for Practitioners
The Blast Radius - Edition [4] Over the...
Brett Crawley is a principal application security engineer and the author of Threat Modeling Gameplay with EoP (Packt, 2024). He created SBOM-Graph and the Elevation of Autonomy card deck for threat modelling AI, LLM and agentic systems, contributes to OWASP, and writes The Blast Radius newsletter on supply chain security, AI security and EU regulation.
The Blast Radius - Edition [4] Over the...
Last week, Anthropic announced Claude Mythos Preview and...
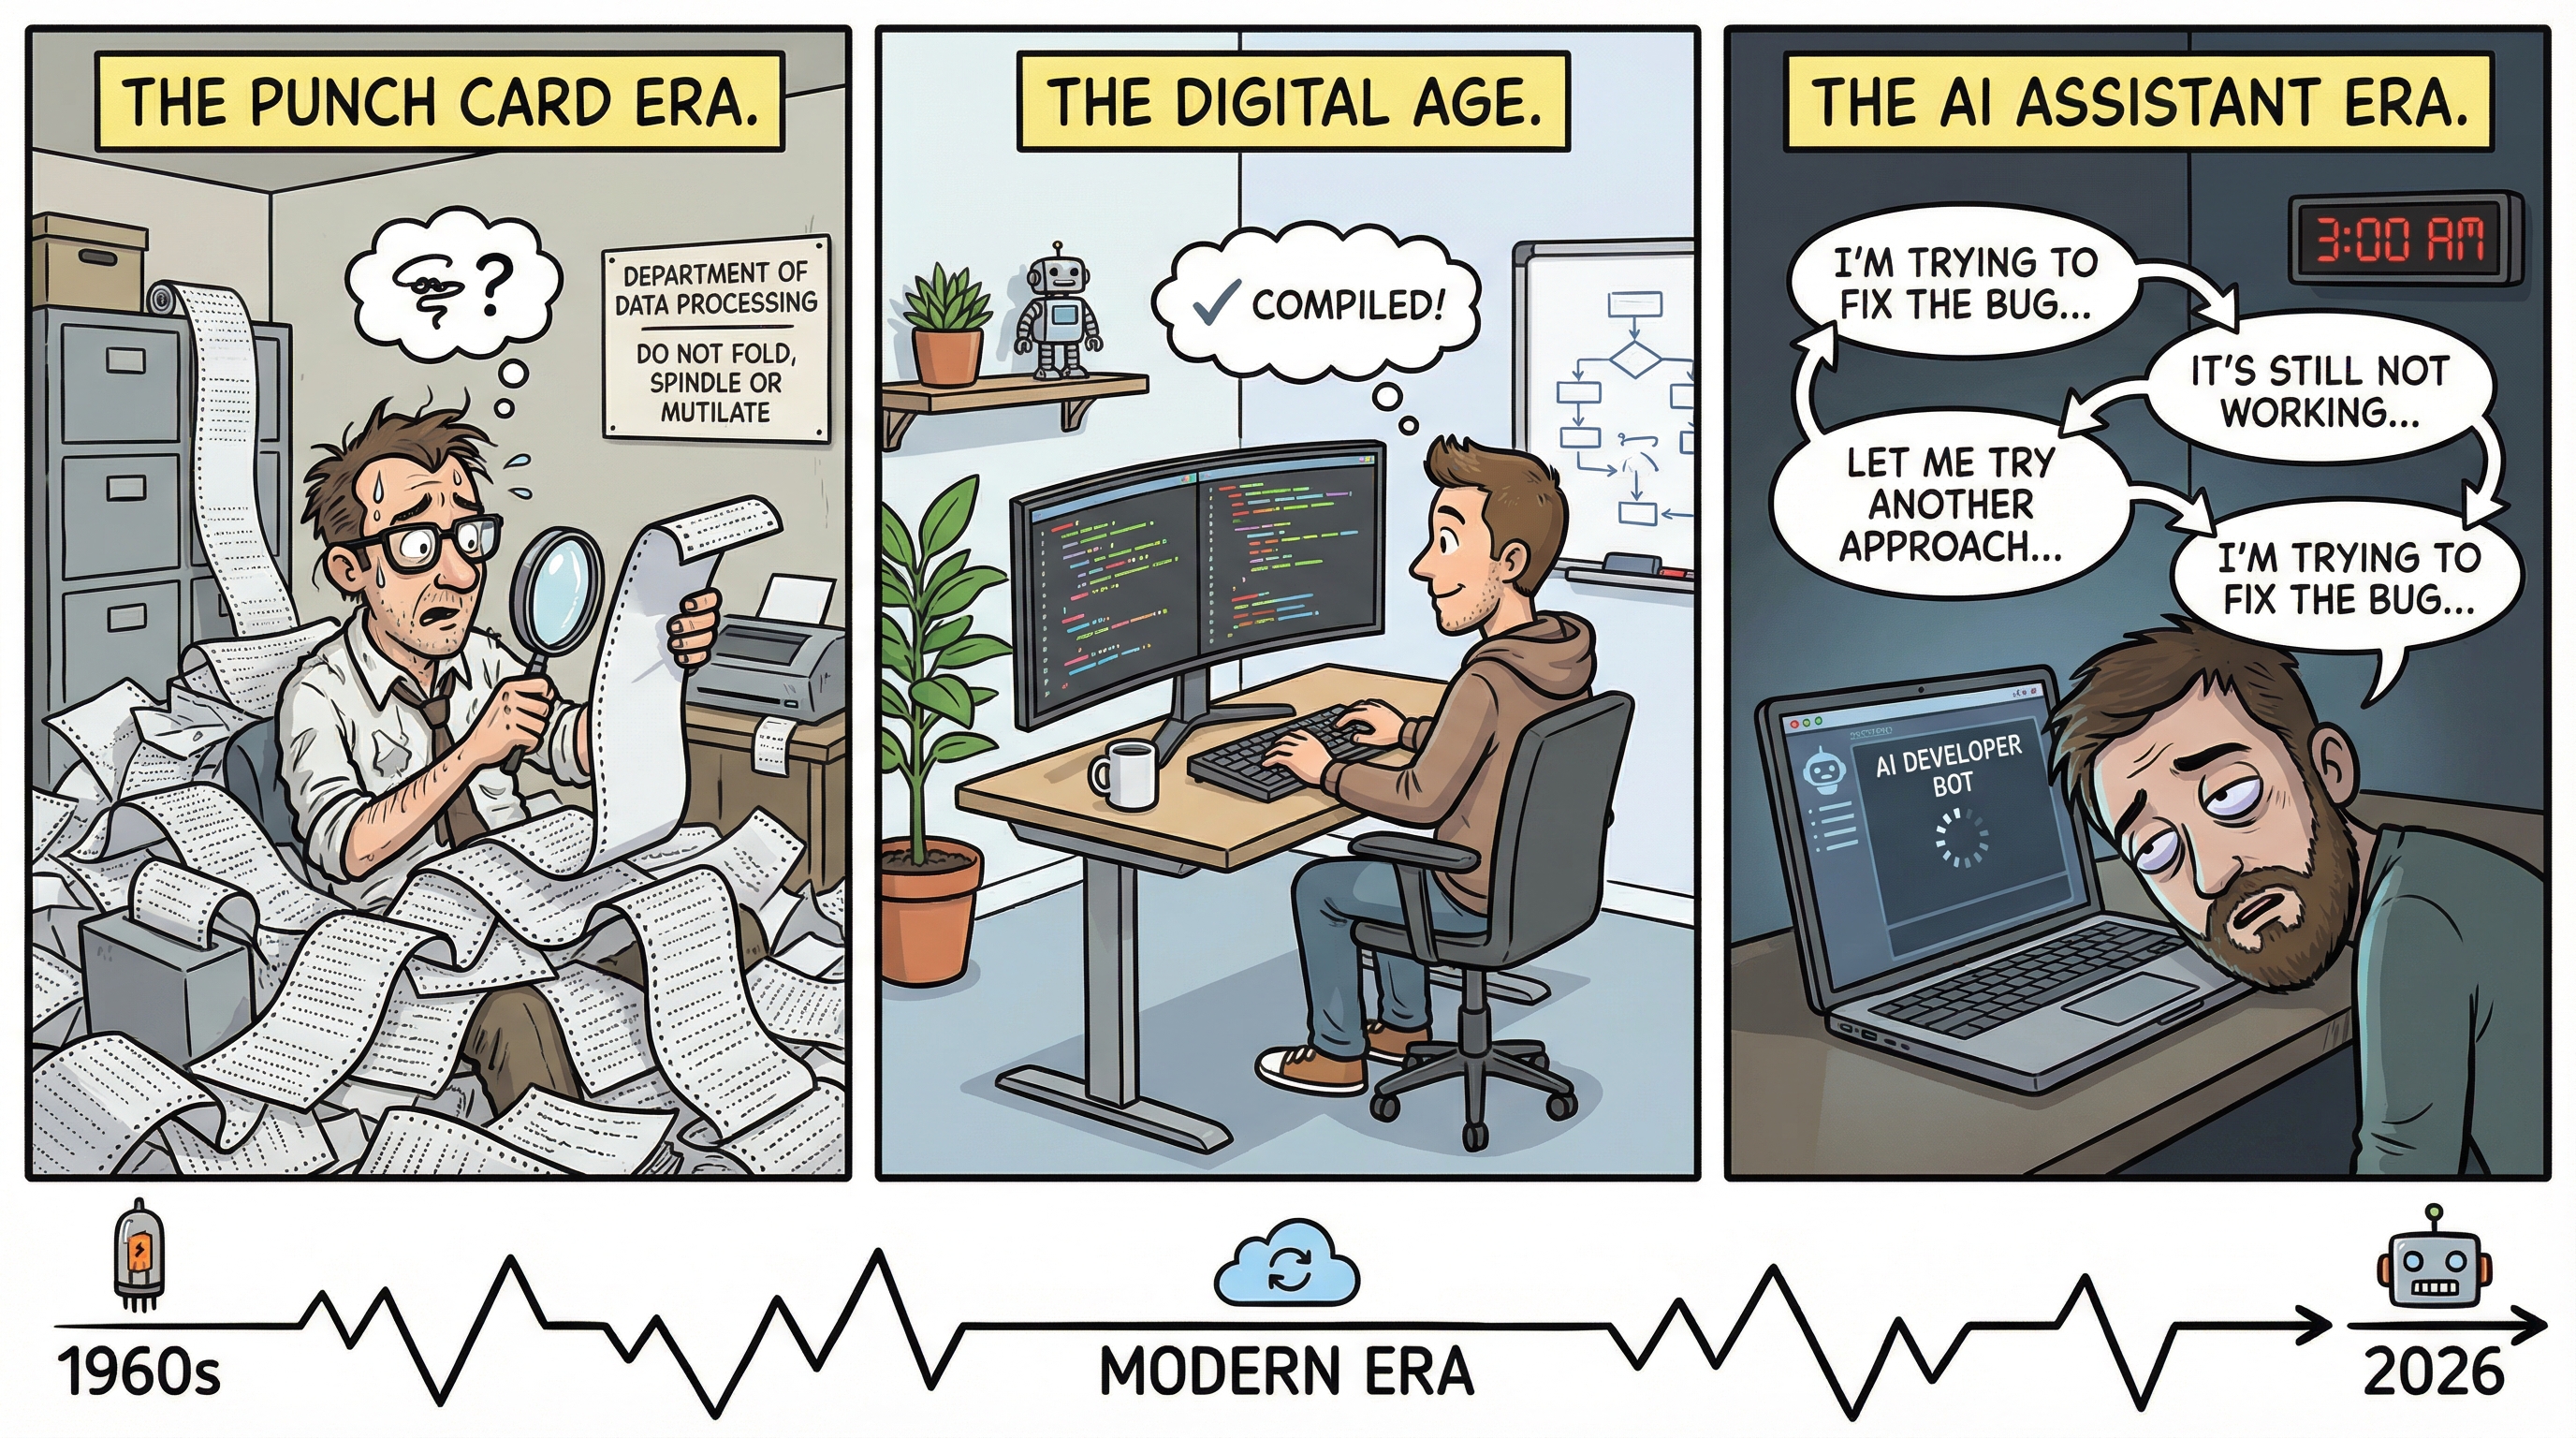
Bear with me on this train of thought....
Cutting the Dead Wood from Your Dependency Graph...
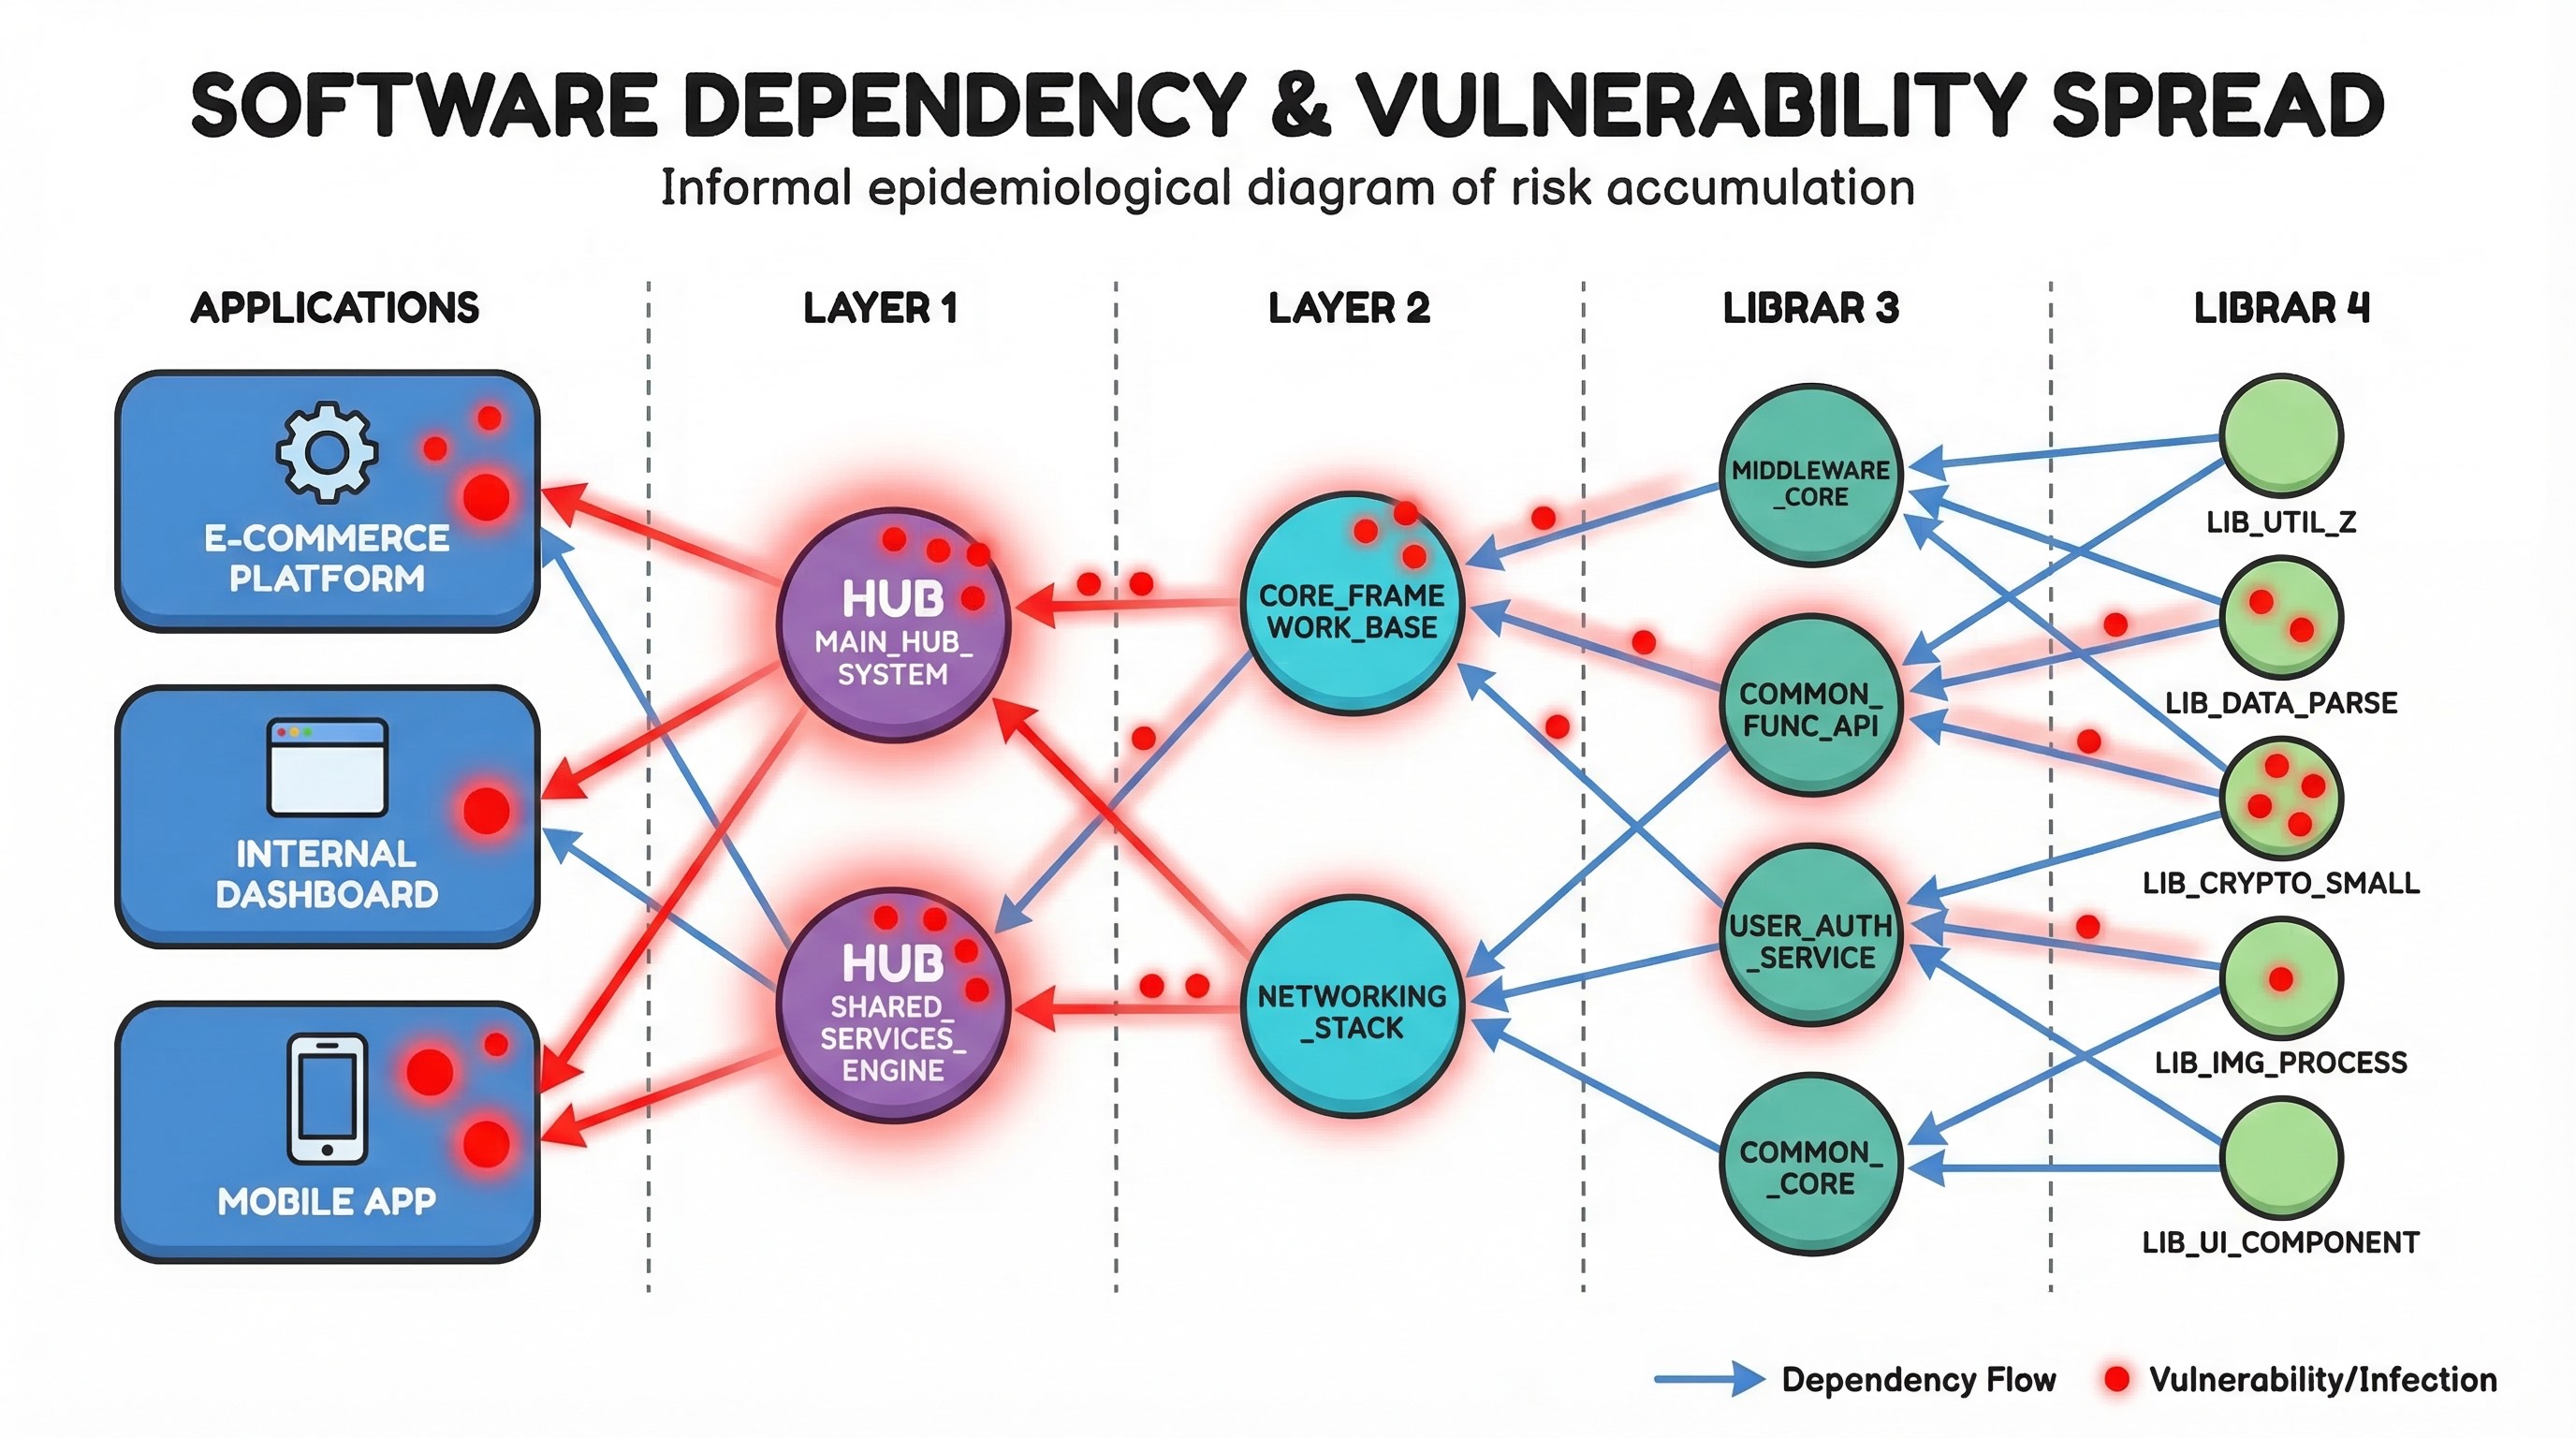
Mitigating Third-Party Component Risk: Swapping the Cancer for...
How One Bad Library Can Poison Your Entire...
I’ve been talking about graphs for dependency analysis...
SAST vs Claude Code Security: A Deep Dive...
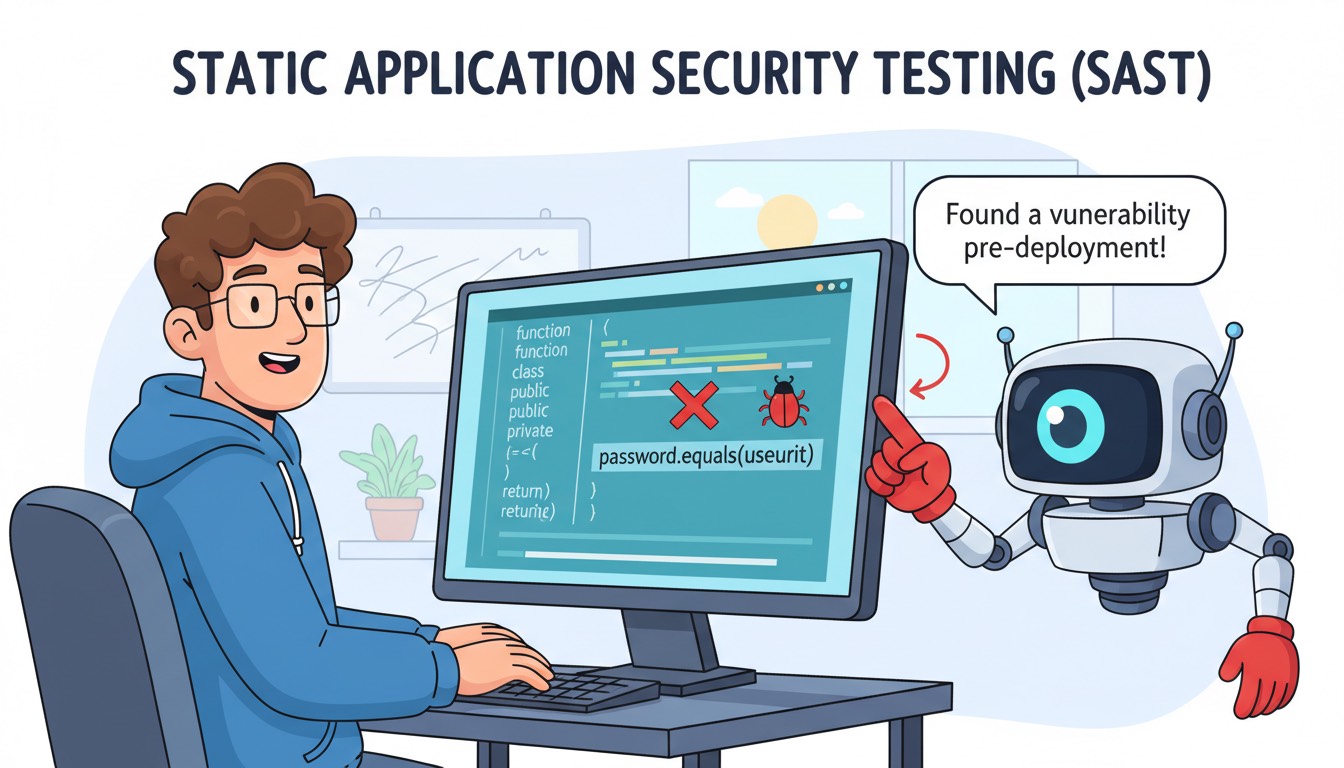
Why SAST is broken, and how it could...
Cursor as your Secure Dev Team What I...
Building an AppSec Program: A Collaborative Approach Are...
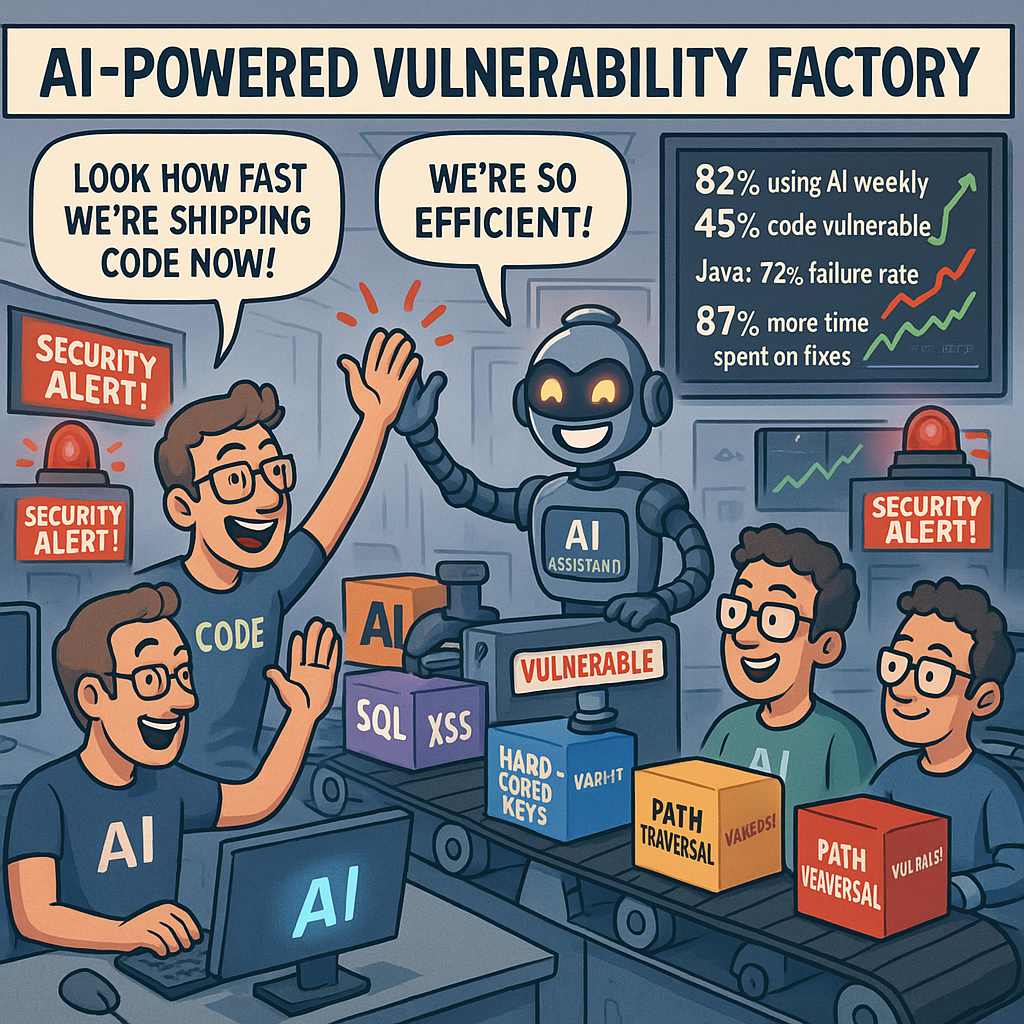
AI-Generated Code: Productivity Gains, Security Pains, and the...
There are lots of ways we can optimise what we do, through a data driven approach, but we need to be careful and use critical and creative thinking.
Why are so many people just diving, straight into the code? A minimum of requirements and design? Perhaps a threat Model?
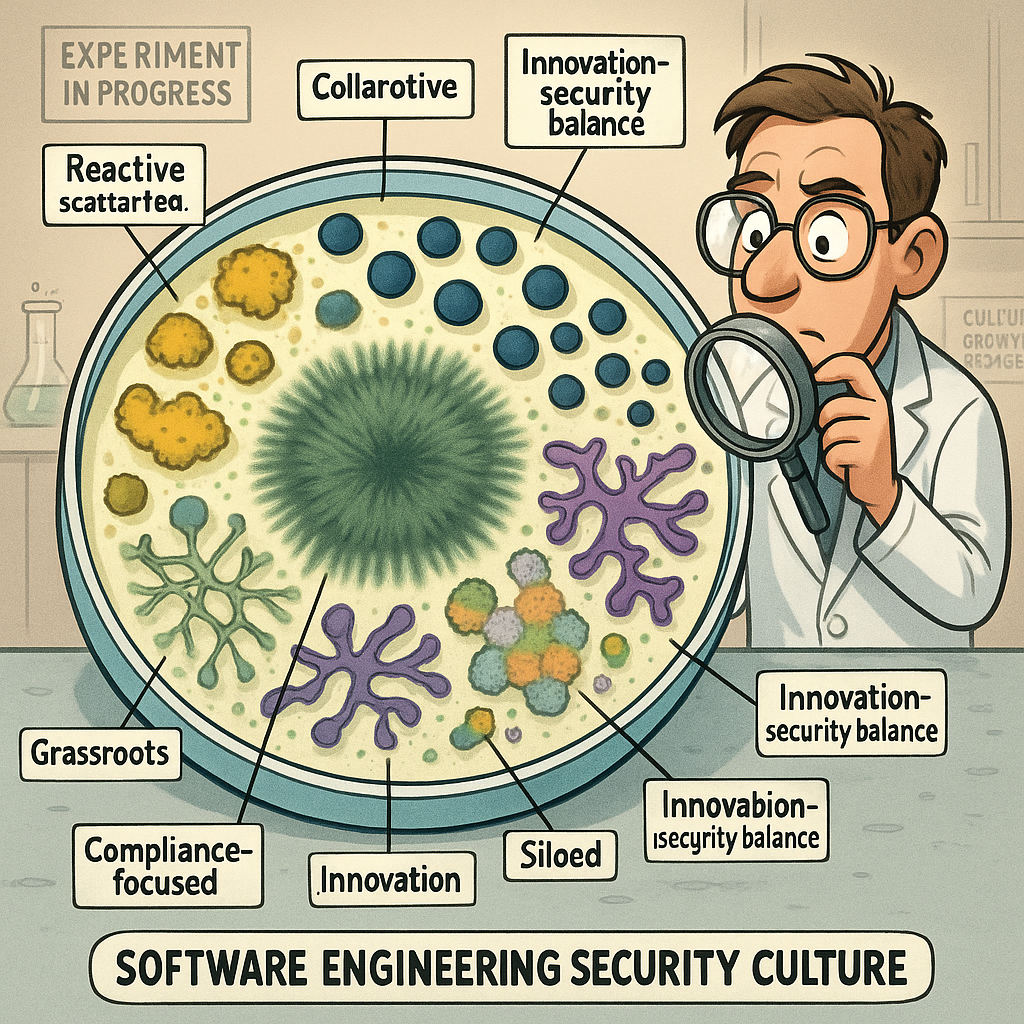
We need to fix the culture, from top to bottom in the software engineering industry. Here are just some of the issues as I see them and what we should be doing about them.
Coming soon to a bookshelf near you, Threat Modeling Gameplay with EoP: A reference manual for spotting threats in software architecture